> ## Documentation Index
> Fetch the complete documentation index at: https://link.datarelay.run/llms.txt
> Use this file to discover all available pages before exploring further.

# OCI Network and VM

> Create the OCI network, Ubuntu VM, and Reserved Public IPv4 for a DataRelay Link server.

# Part I — Build the OCI network and VM

## 1. Open Virtual Cloud Networks

From the OCI Home page, enter **Networking → Virtual Cloud Networks**. The image below is the **original Picture 1** from the field-deployment Word guide; it is used without conversion or downscaling.
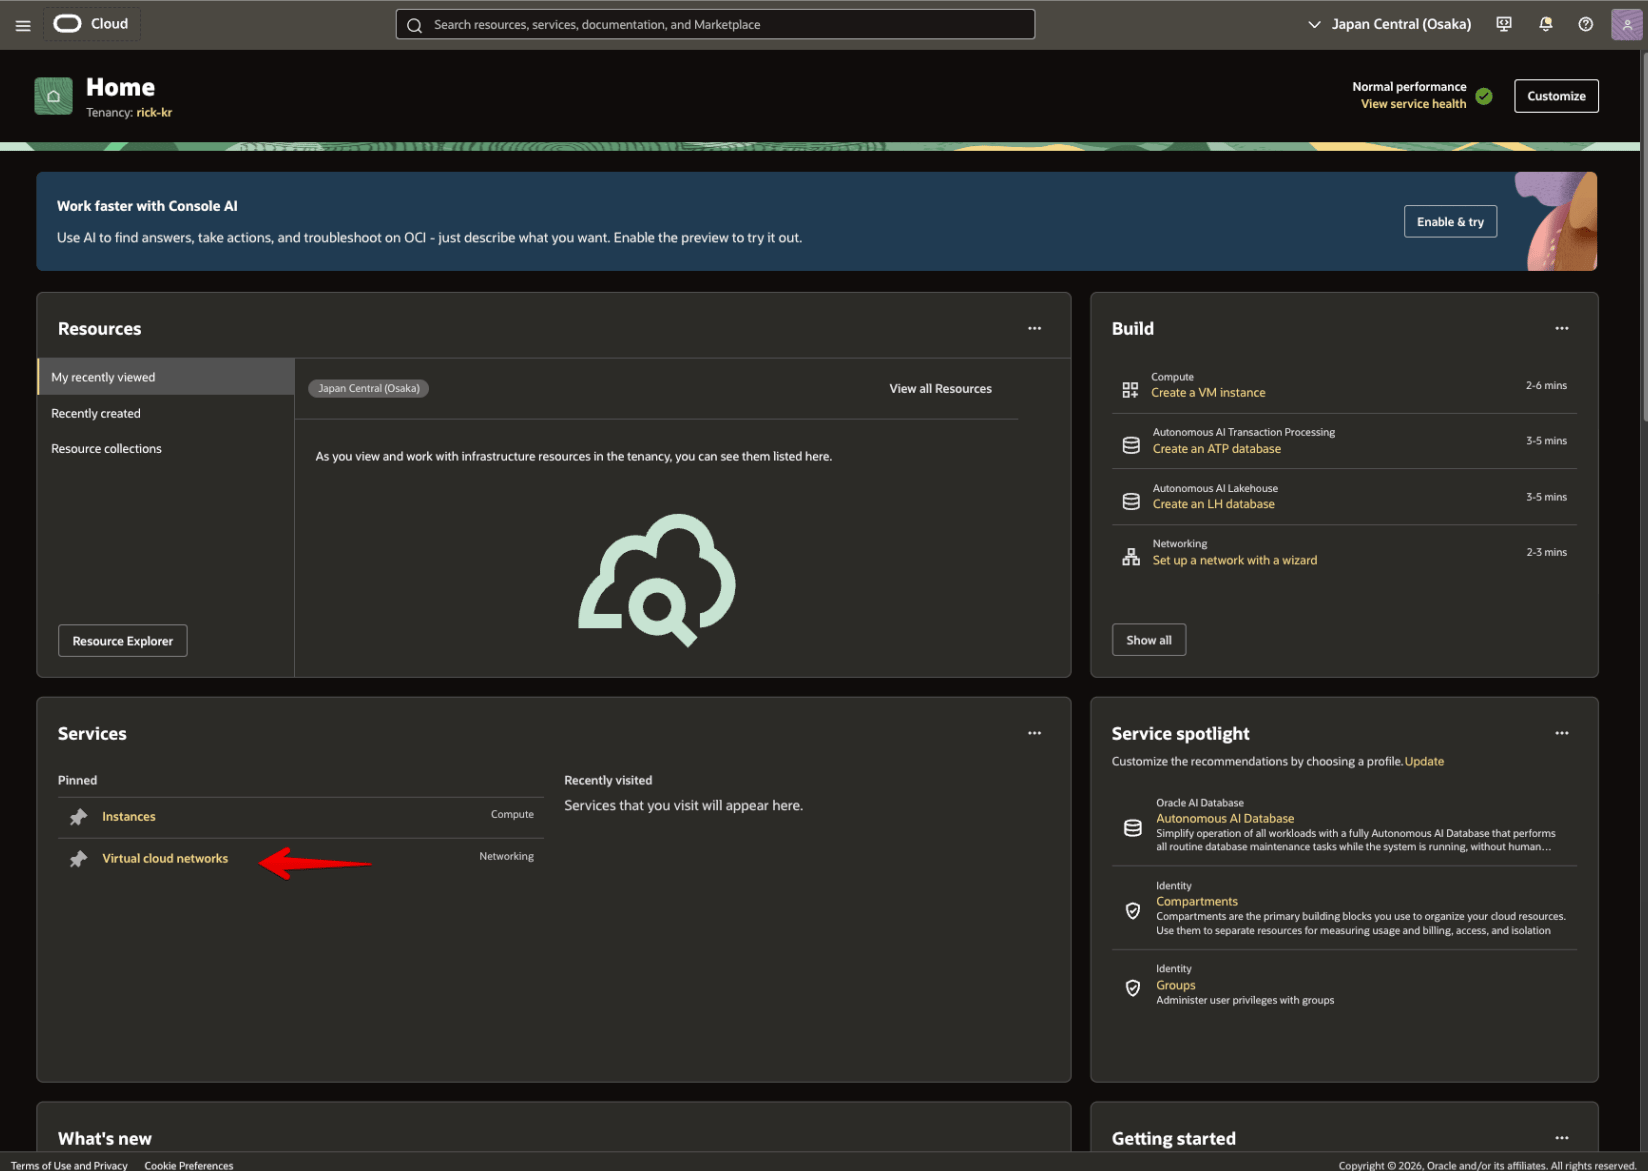
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/1.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=bdf4607ae65b0f110e0516dbe57945ee" alt="Picture 1. OCI Home - enter Networking / Instances" width="1648" height="1171" data-path="images/oci/1.png" />

## 2. Create the VCN, Internet Gateway, route, subnet, and ingress rules

Use these values:

```text theme={null}
VCN name             data-relay-vcn
VCN IPv4 CIDR         10.0.0.0/16
Internet Gateway      data-relay-internet-gateway
Default route         0.0.0.0/0 -> Internet Gateway
Public subnet         data-relay-public-subnet
Public subnet CIDR    10.0.0.0/24
Subnet type           Regional / Public
```

### 2-1. Create the VCN

Open **Virtual Cloud Networks → Create VCN**.
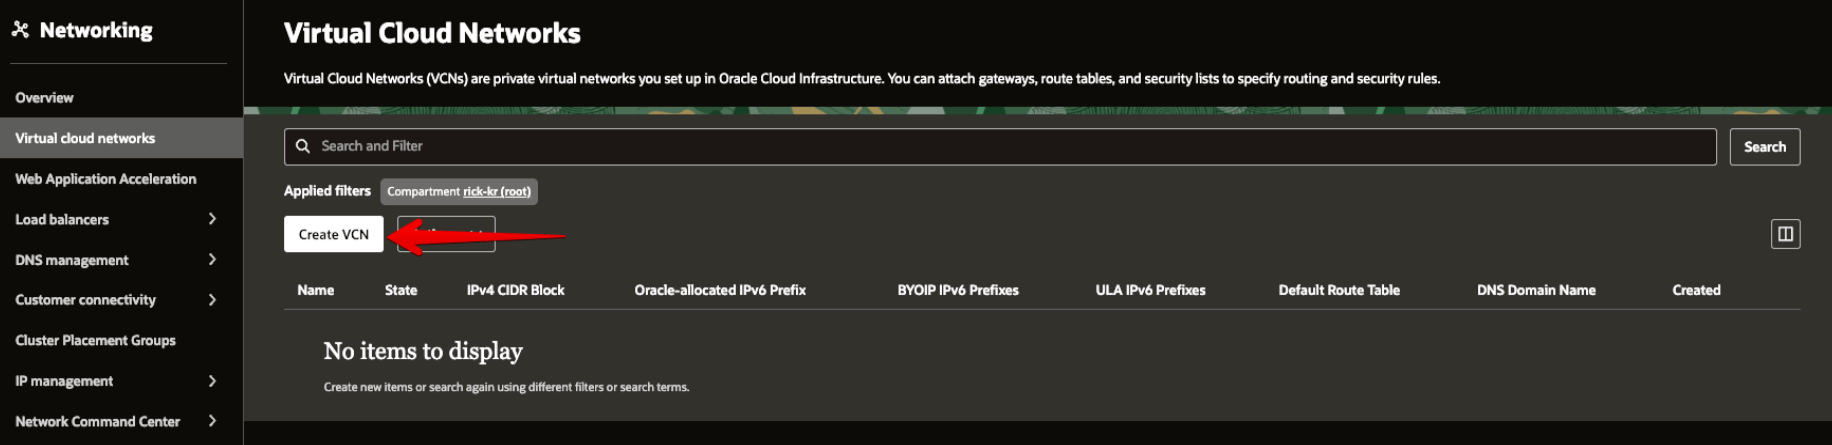
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/2.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=863f7f0a49ae4ae50a3eaddbc37f5aec" alt="Picture 2. Select Create VCN in Virtual Cloud Networks" width="1832" height="445" data-path="images/oci/2.png" />

Set the VCN name to `data-relay-vcn` and the IPv4 CIDR to `10.0.0.0/16`.
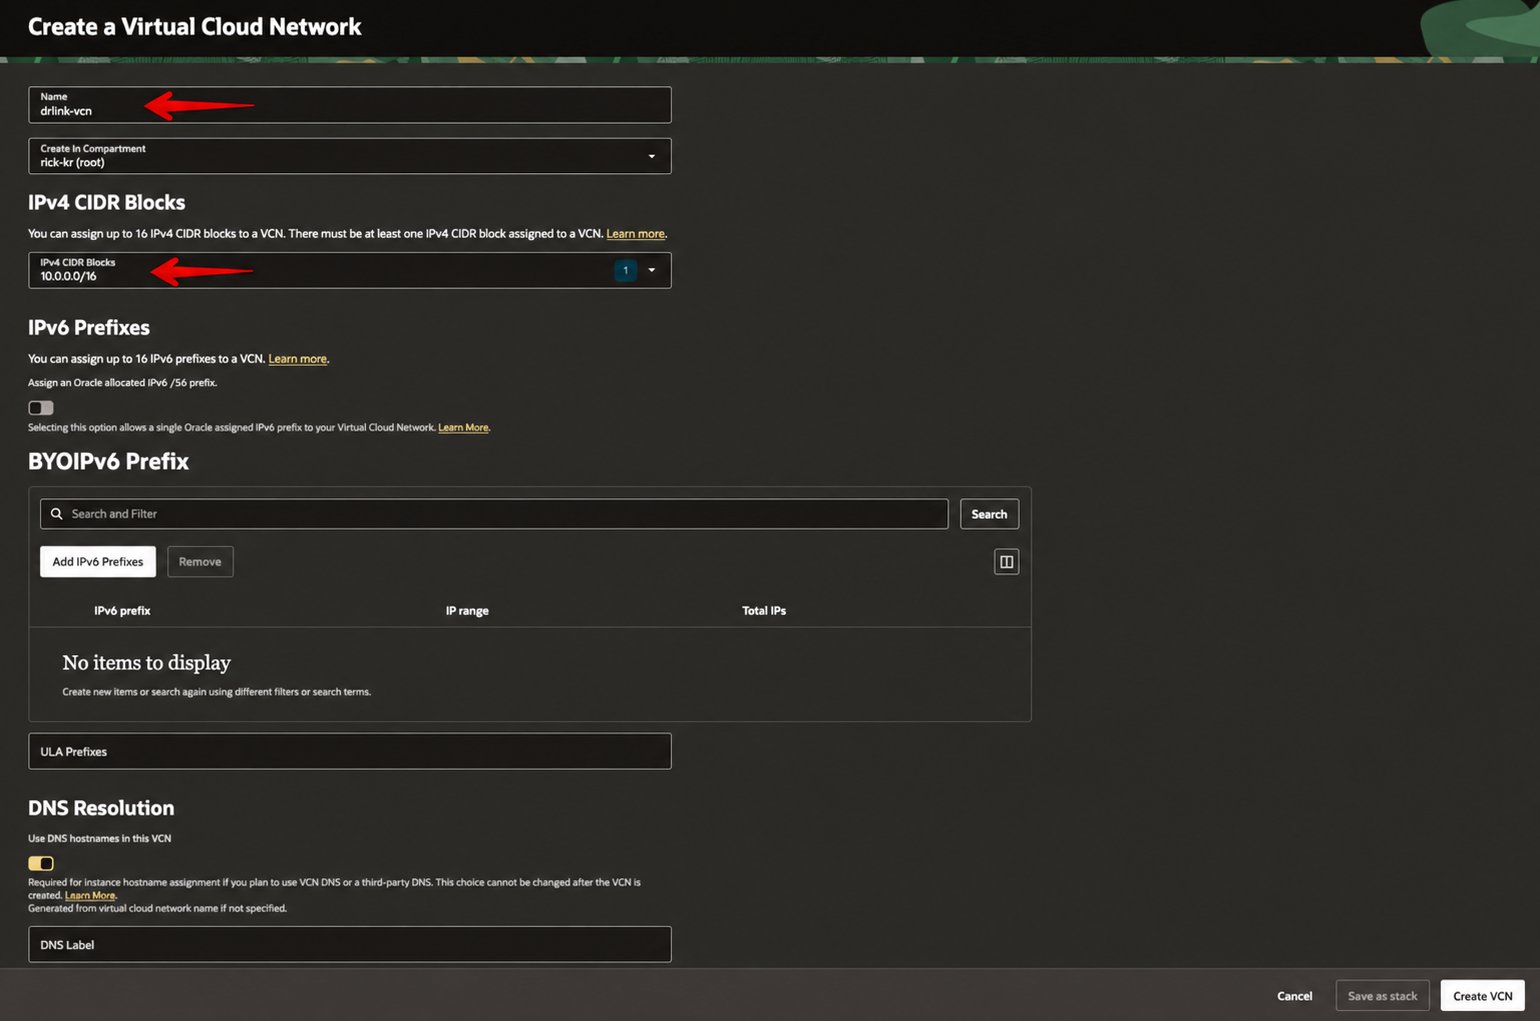
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/3.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=e2cf91fa4fb4863782f608d7f20c6e00" alt="Picture 3. Configure the VCN name and IPv4 CIDR" width="1540" height="1021" data-path="images/oci/3.png" />

### 2-2. Create the Internet Gateway

In the new `data-relay-vcn`, open the **Gateways** tab and create an Internet Gateway.
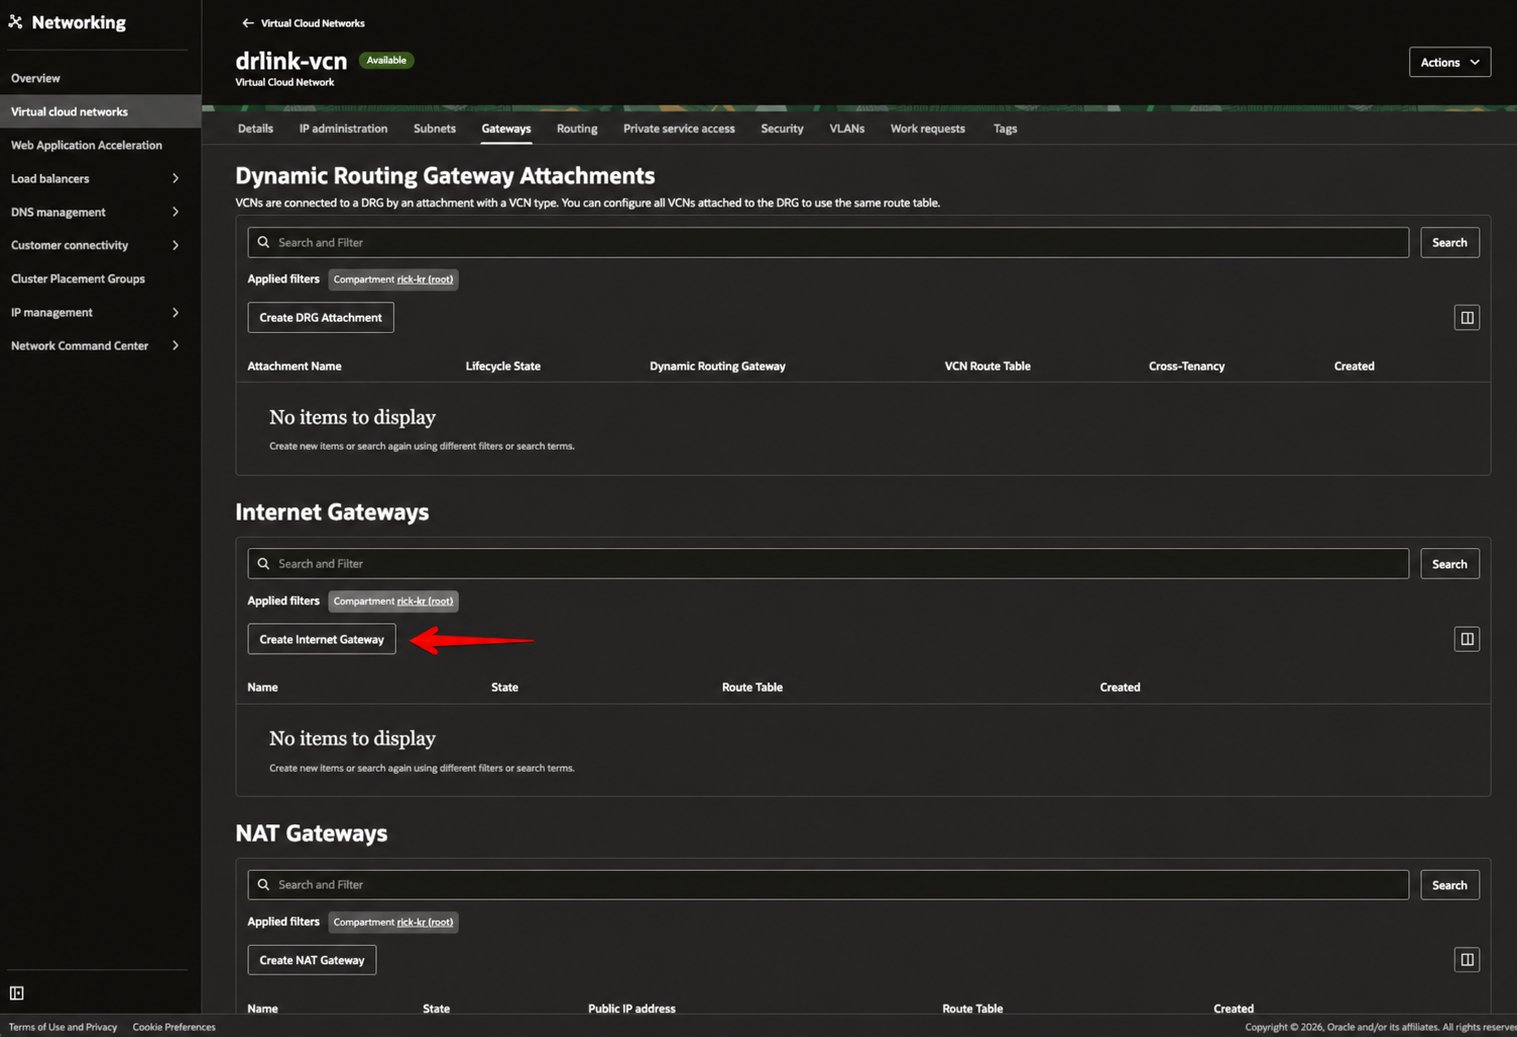
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/4.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=8677e3ce92cf435fe1f16891e2d76fe5" alt="Picture 4. Create an Internet Gateway from the VCN Gateways tab" width="1517" height="1037" data-path="images/oci/4.png" />

Use `data-relay-internet-gateway` as the example gateway name.
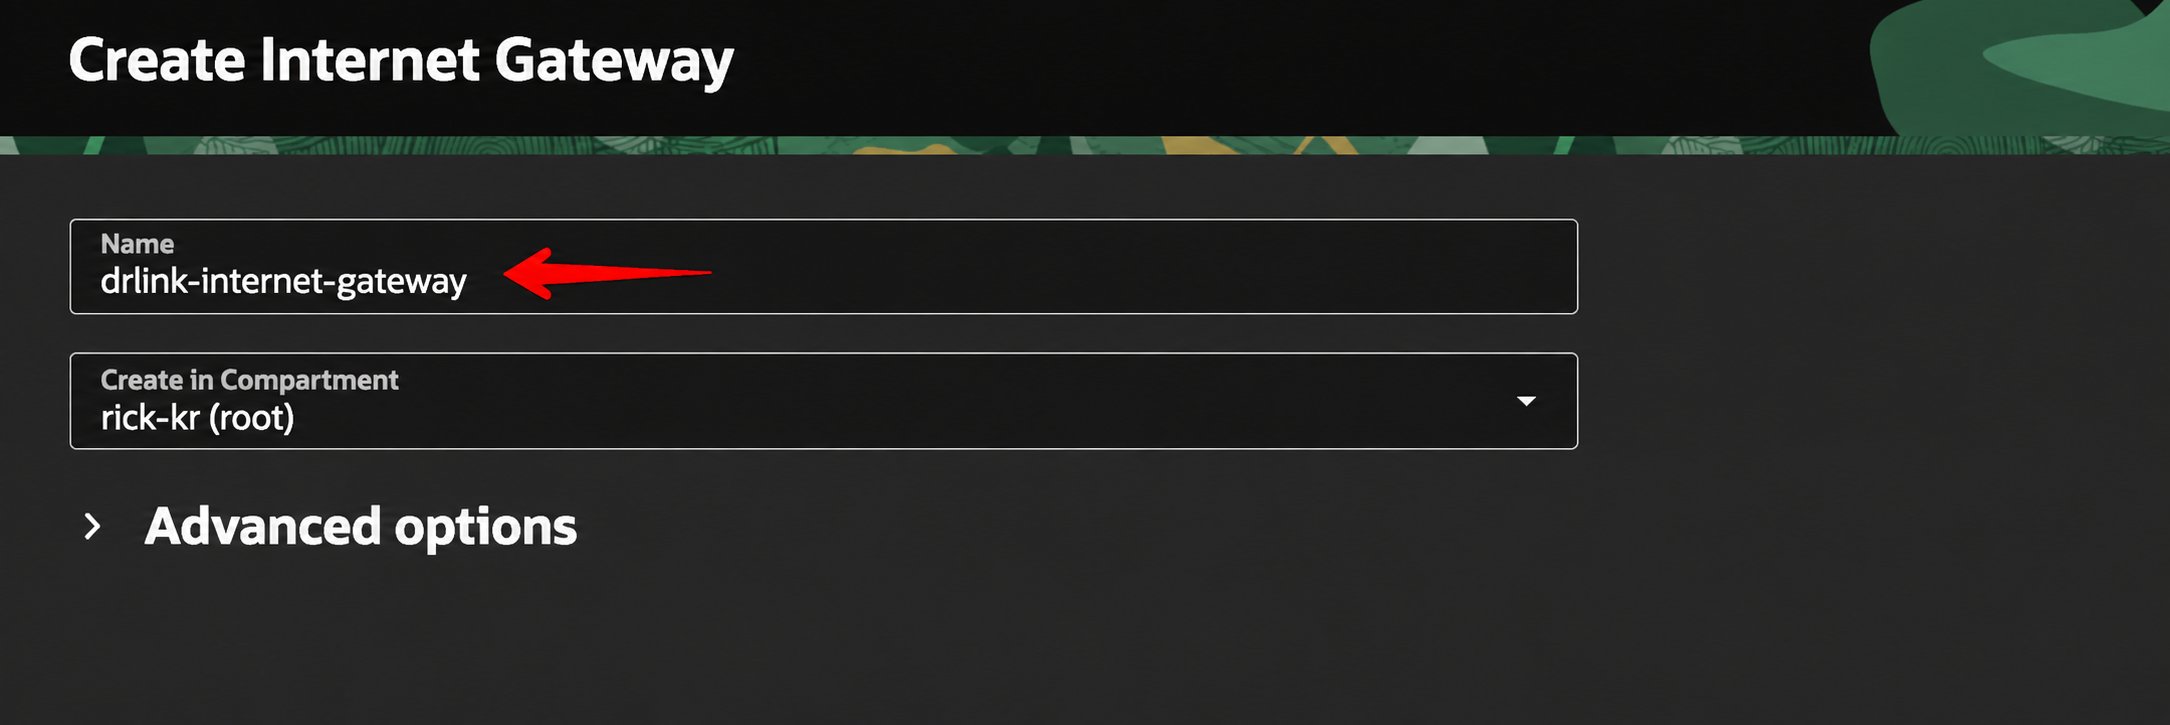
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/5.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=6784d443291fbb248f34cffa6eb025b3" alt="Picture 5. Internet Gateway name example: data-relay-internet-gateway" width="2170" height="725" data-path="images/oci/5.png" />

### 2-3. Add the Internet route to the default route table

Open the **Routing** tab and select `Default Route Table for data-relay-vcn`.
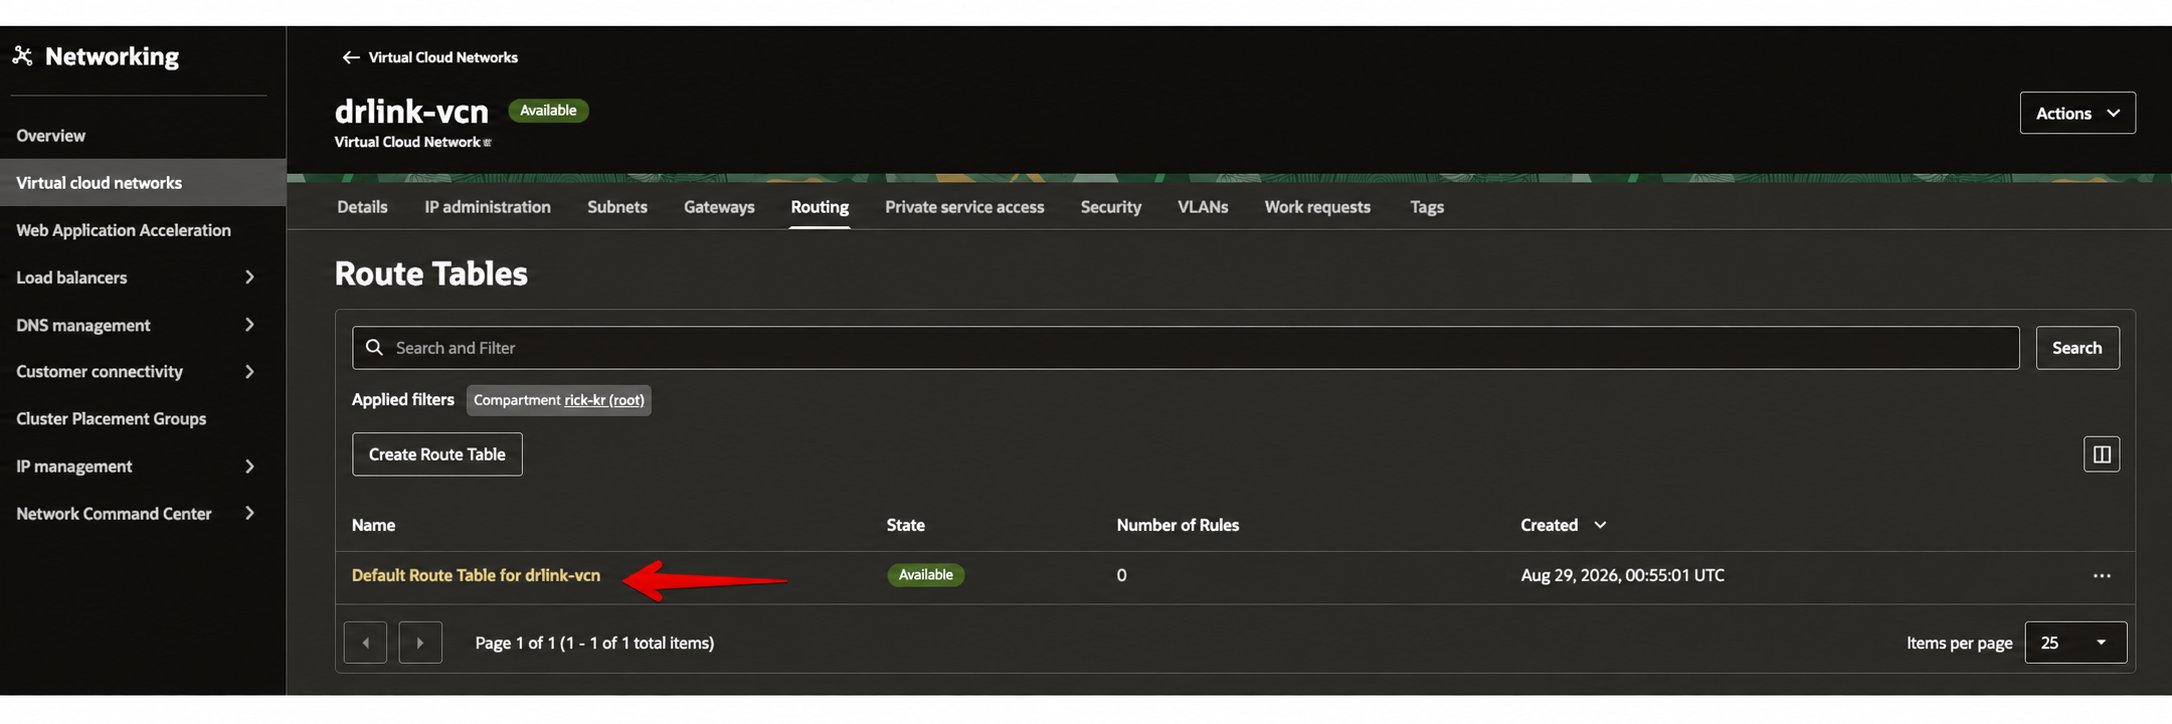
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/6.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=77c42134648fc91dfa899b1f77a2bf68" alt="Picture 6. Select the default route table from the VCN Routing tab" width="2172" height="724" data-path="images/oci/6.png" />

Choose **Route Rules → Add Route Rules**.
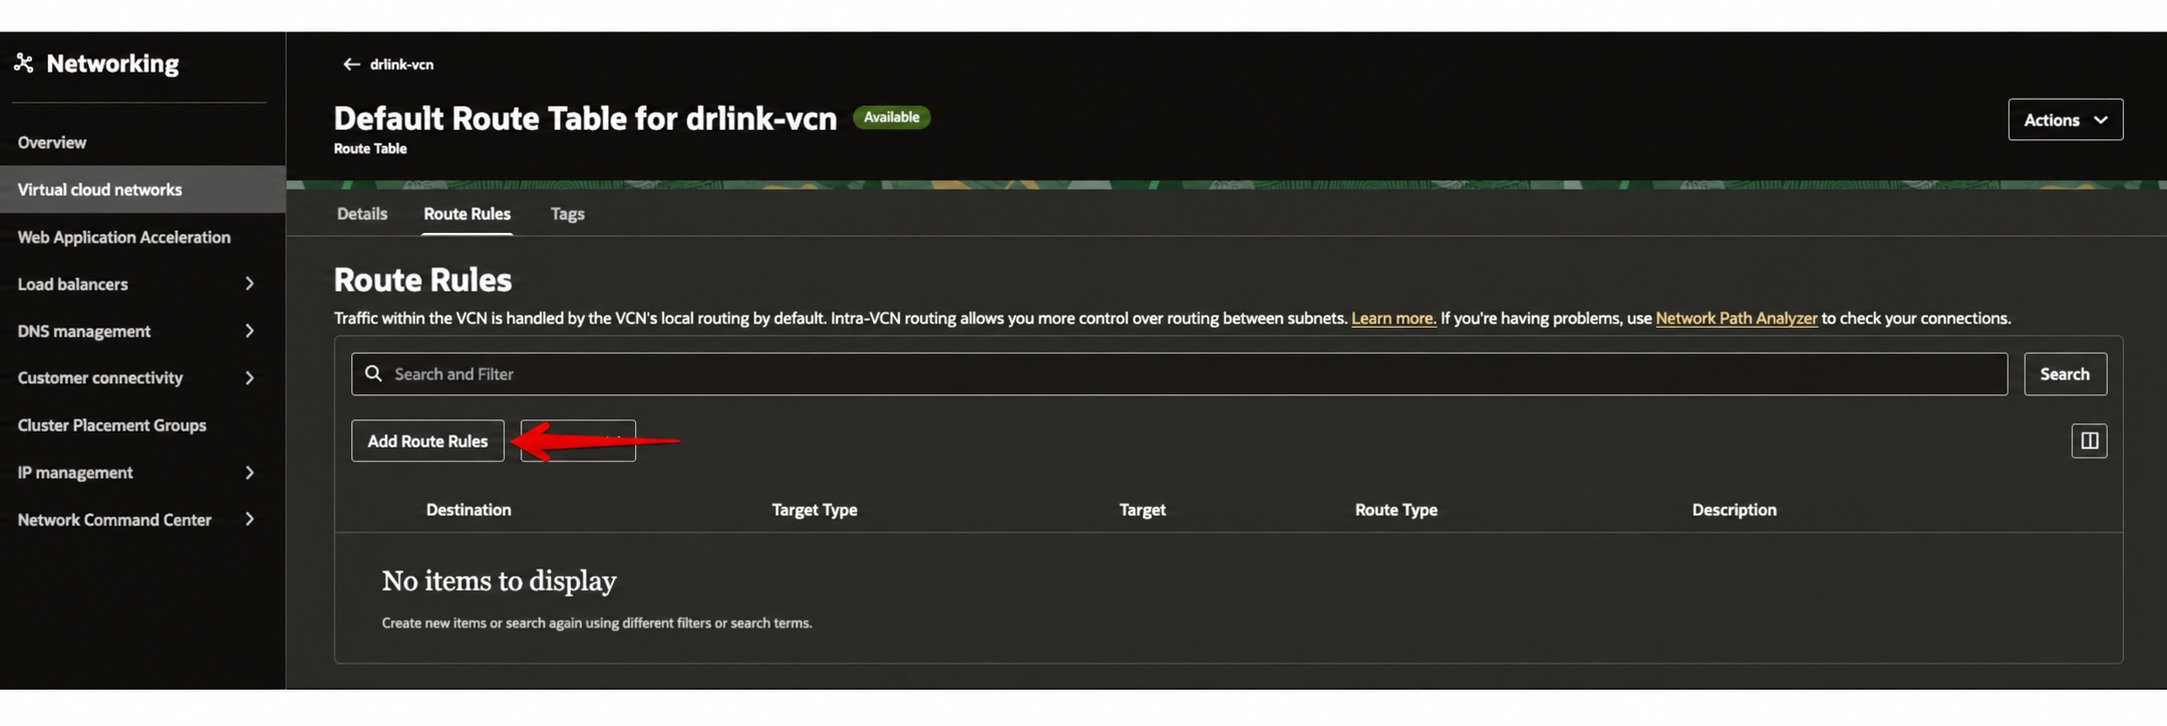
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/7.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=eb532cdc0c3beb2a337abc8050be88e6" alt="Picture 7. Add a route rule" width="2167" height="726" data-path="images/oci/7.png" />

Add the following route:

```text theme={null}
Target Type        Internet Gateway
Destination CIDR   0.0.0.0/0
Target             data-relay-internet-gateway
```
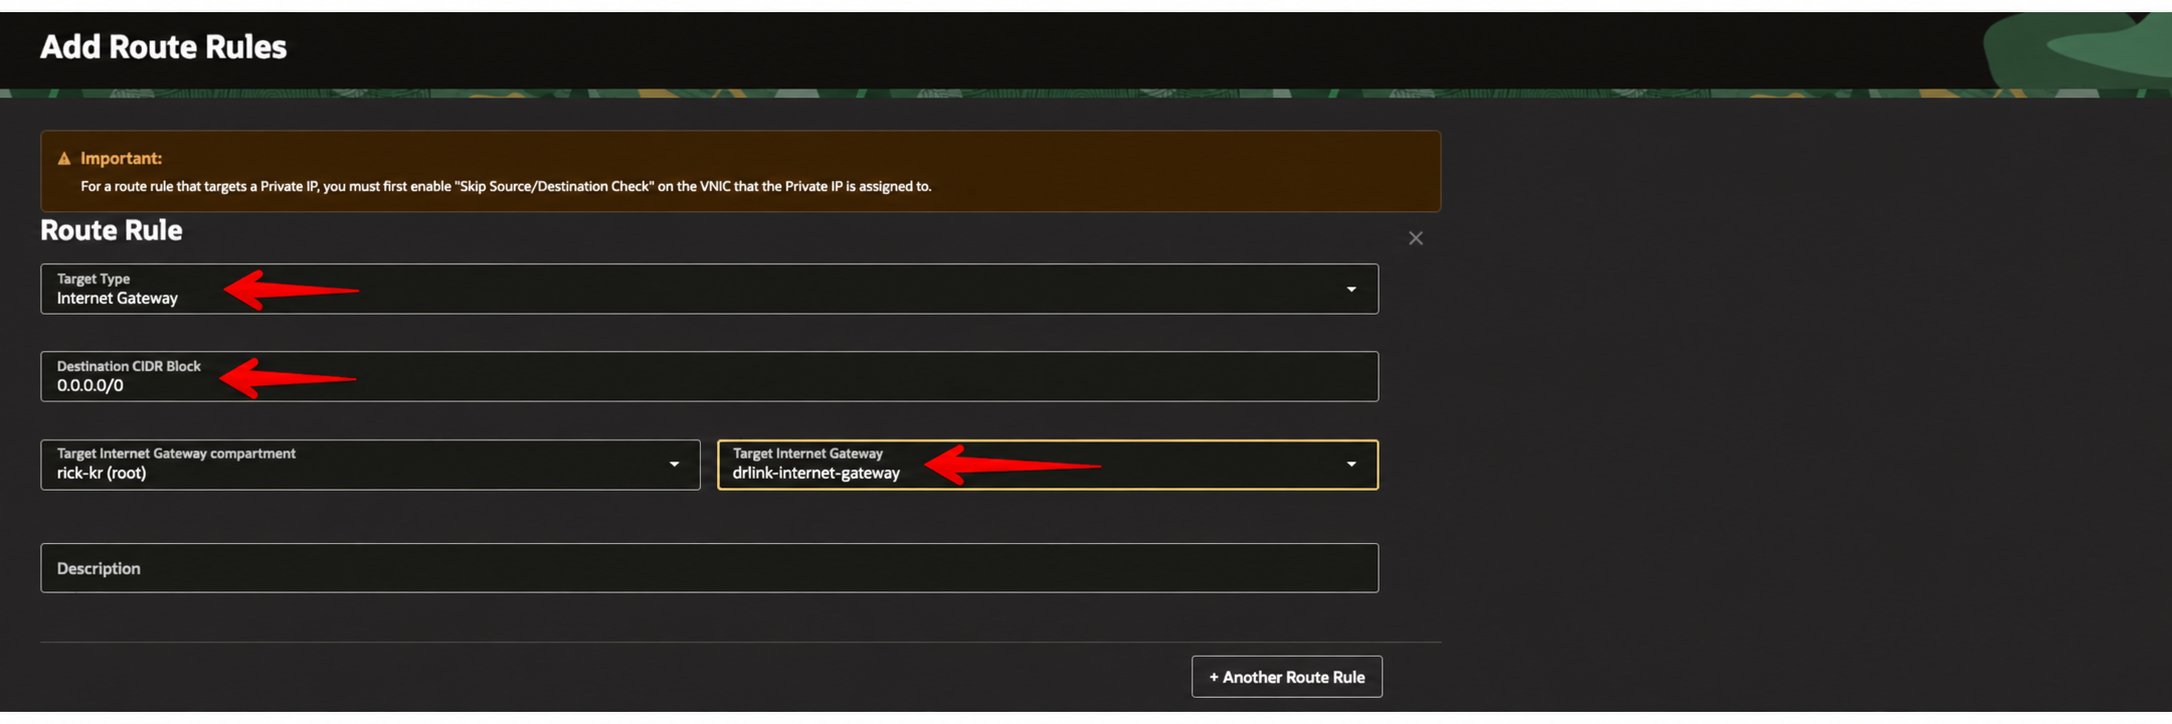
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/8.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=7d5554911ea090a1006aa2cc1dac33ed" alt="Picture 8. Add the 0.0.0.0/0 route through the Internet Gateway" width="2172" height="724" data-path="images/oci/8.png" />

Confirm that the route rule is present after saving.
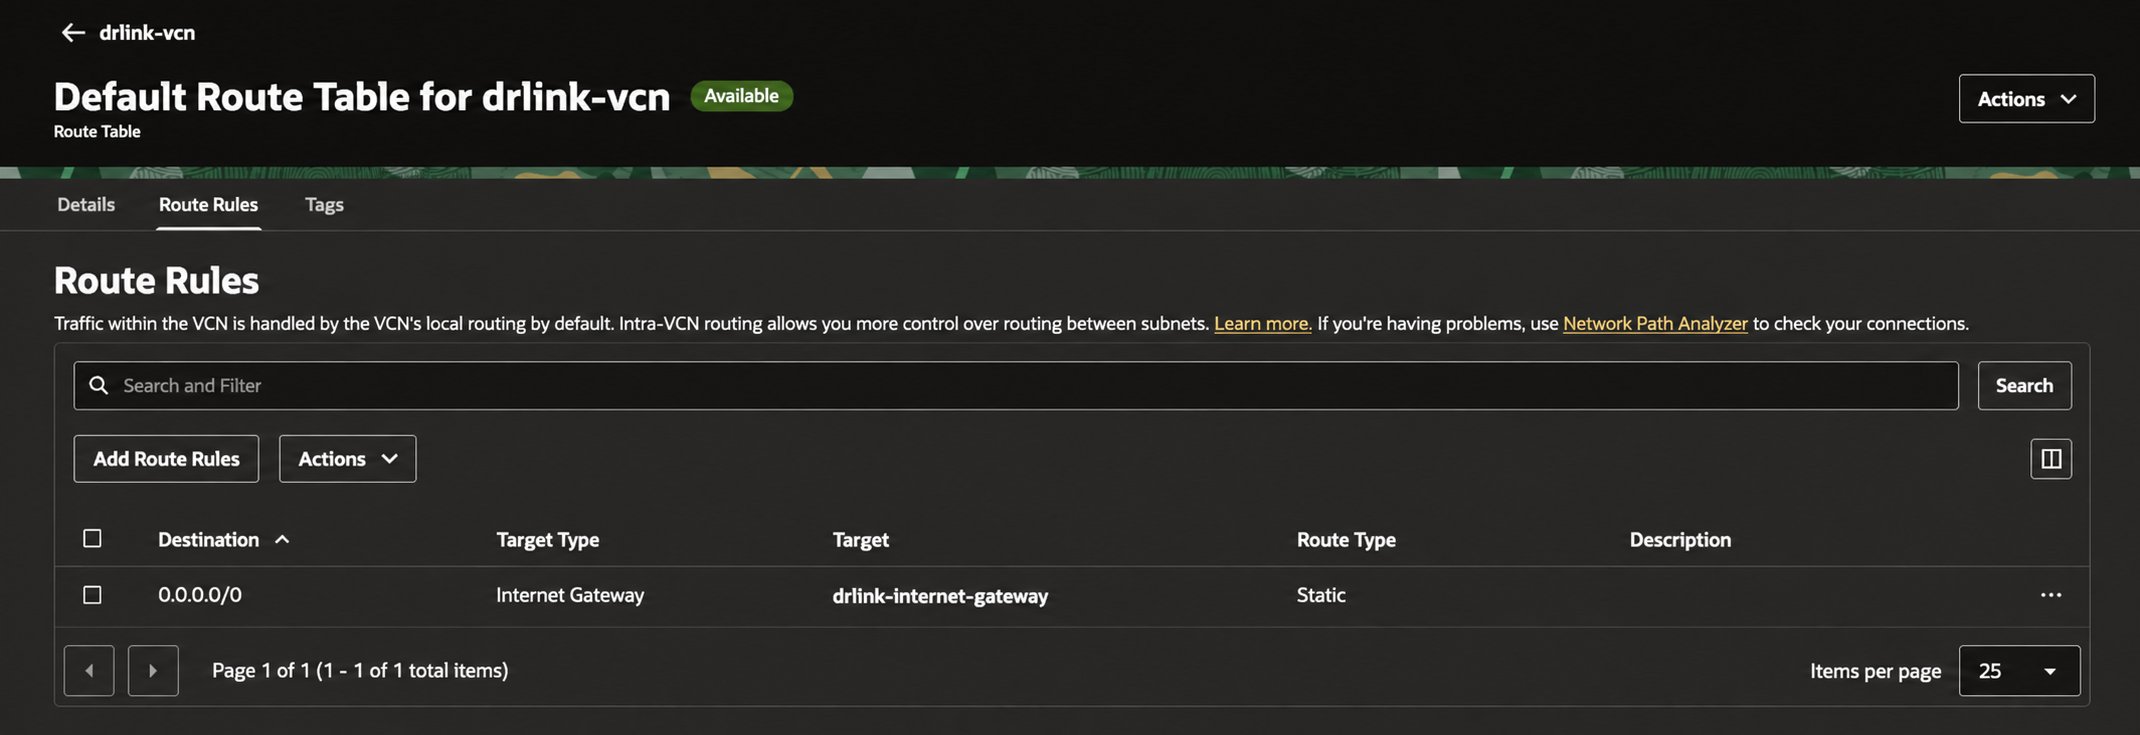
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/9.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=f6cf82009895a91dd83d795a4b24371d" alt="Picture 9. Confirm the applied route rule" width="2140" height="735" data-path="images/oci/9.png" />

### 2-4. Start creating the public subnet

Open the **Subnets** tab and select **Create Subnet**.
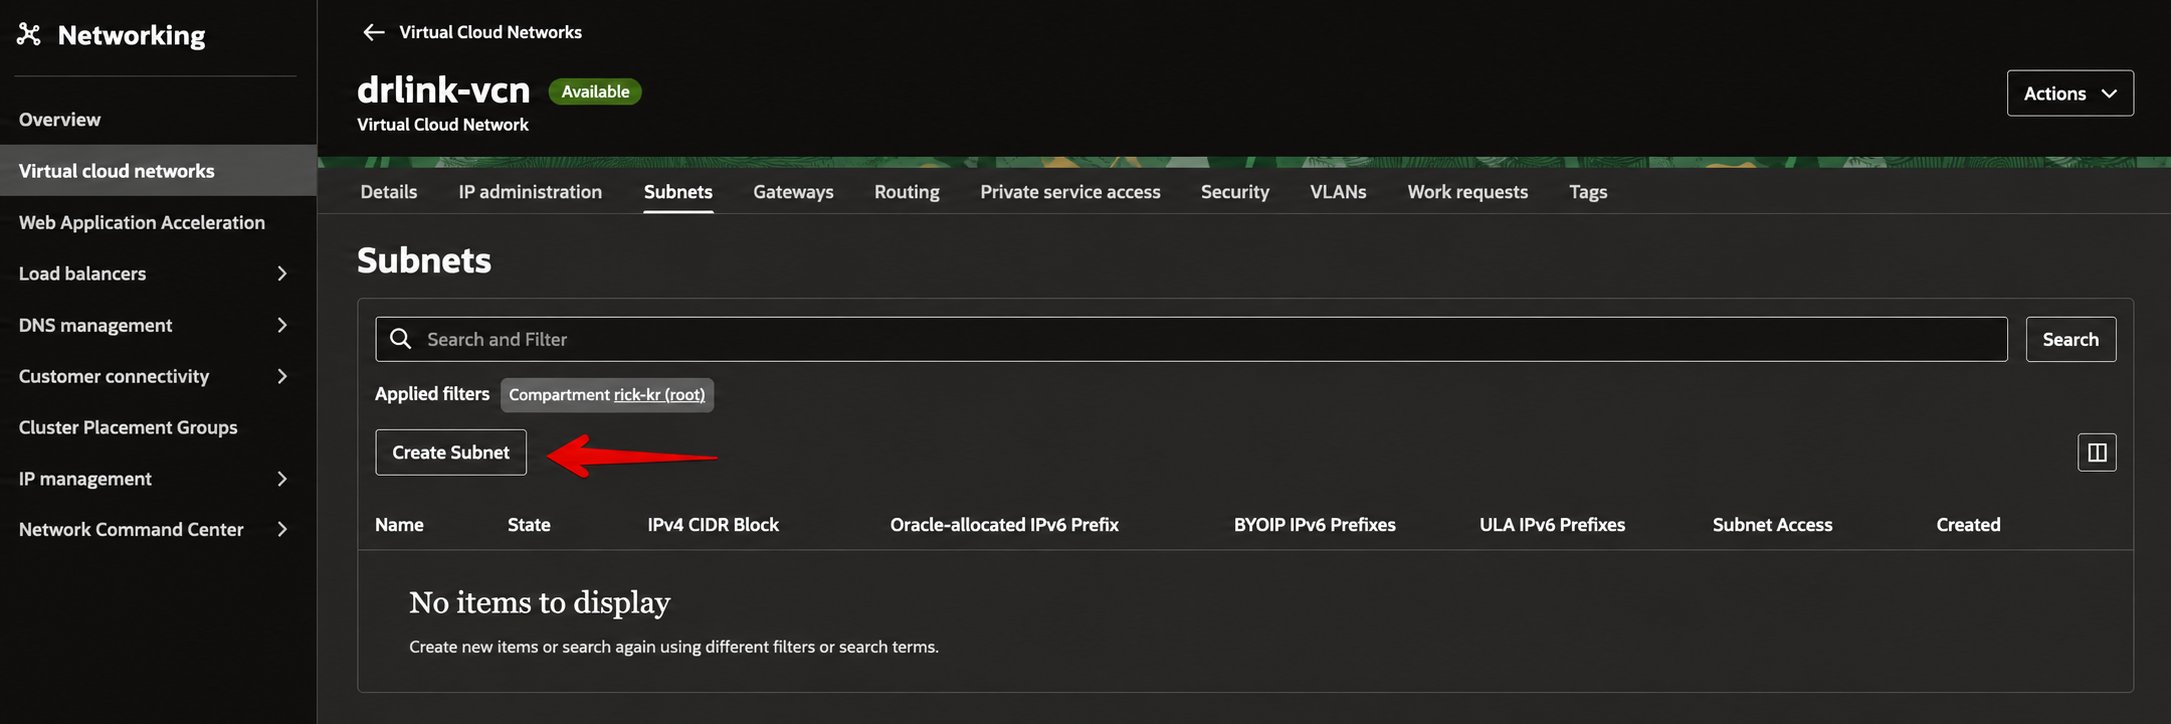
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/10.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=bf812beeceba09ddf7629464dbc2efbc" alt="Picture 10. Start creating the public subnet" width="2171" height="724" data-path="images/oci/10.png" />

### 2-5. Configure the public subnet

Create the public subnet with the following values:

```text theme={null}
Name           data-relay-public-subnet
Subnet Type    Regional
IPv4 CIDR      10.0.0.0/24
Route Table    Default Route Table for data-relay-vcn
Subnet Access  Public Subnet
```
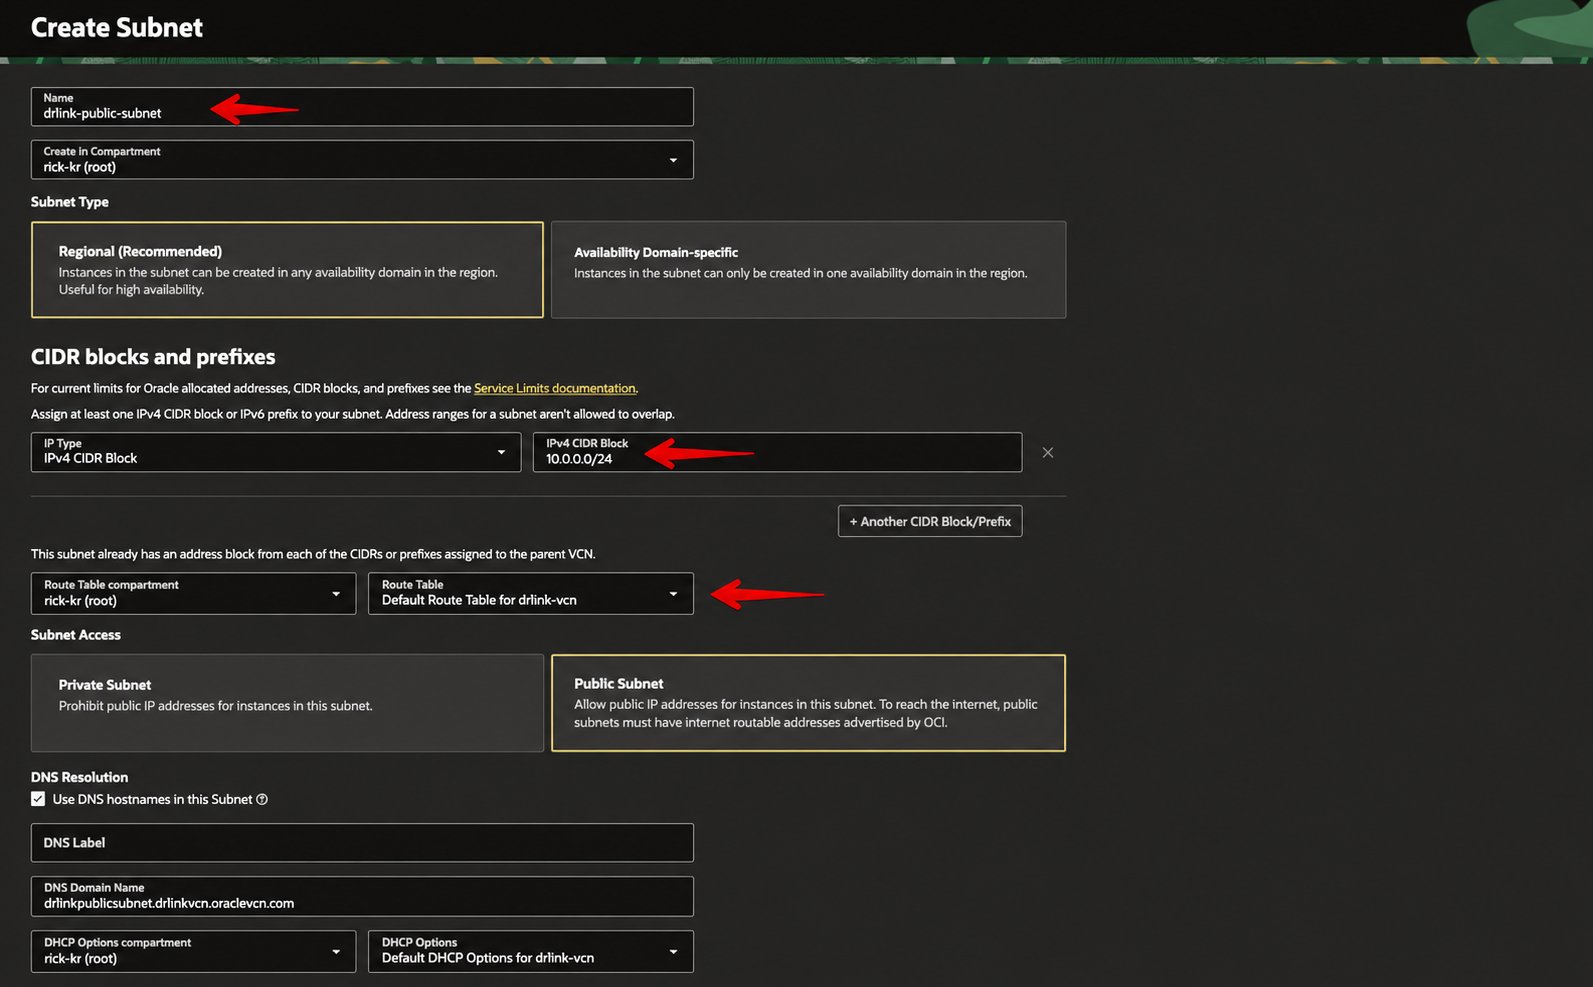
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/11.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=d2c49dc1ed92cee8365ab891bdf4ada5" alt="Picture 11. Configure the public subnet" width="1593" height="987" data-path="images/oci/11.png" />

### 2-6. Configure the Security List

Open the VCN's **Security Lists** page.
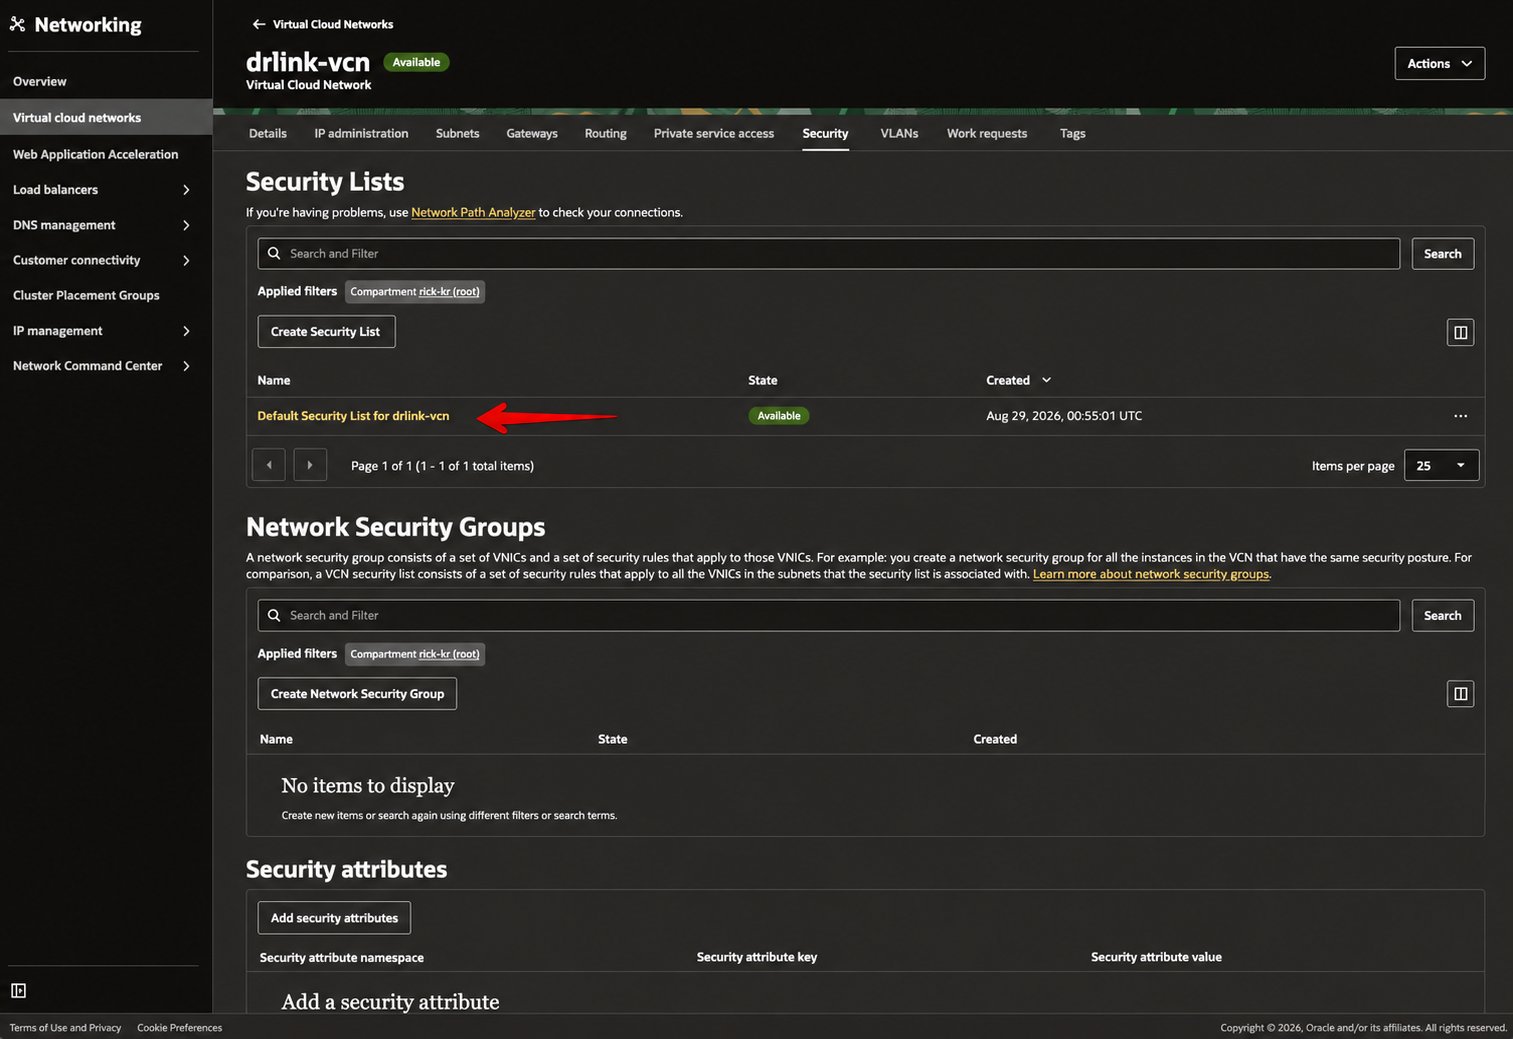
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/12.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=d33f12d55bbb6ea339750faf56de5960" alt="Picture 12. Open the VCN Security Lists page" width="1513" height="1039" data-path="images/oci/12.png" />

Review the ingress rules on the **Default Security List**.
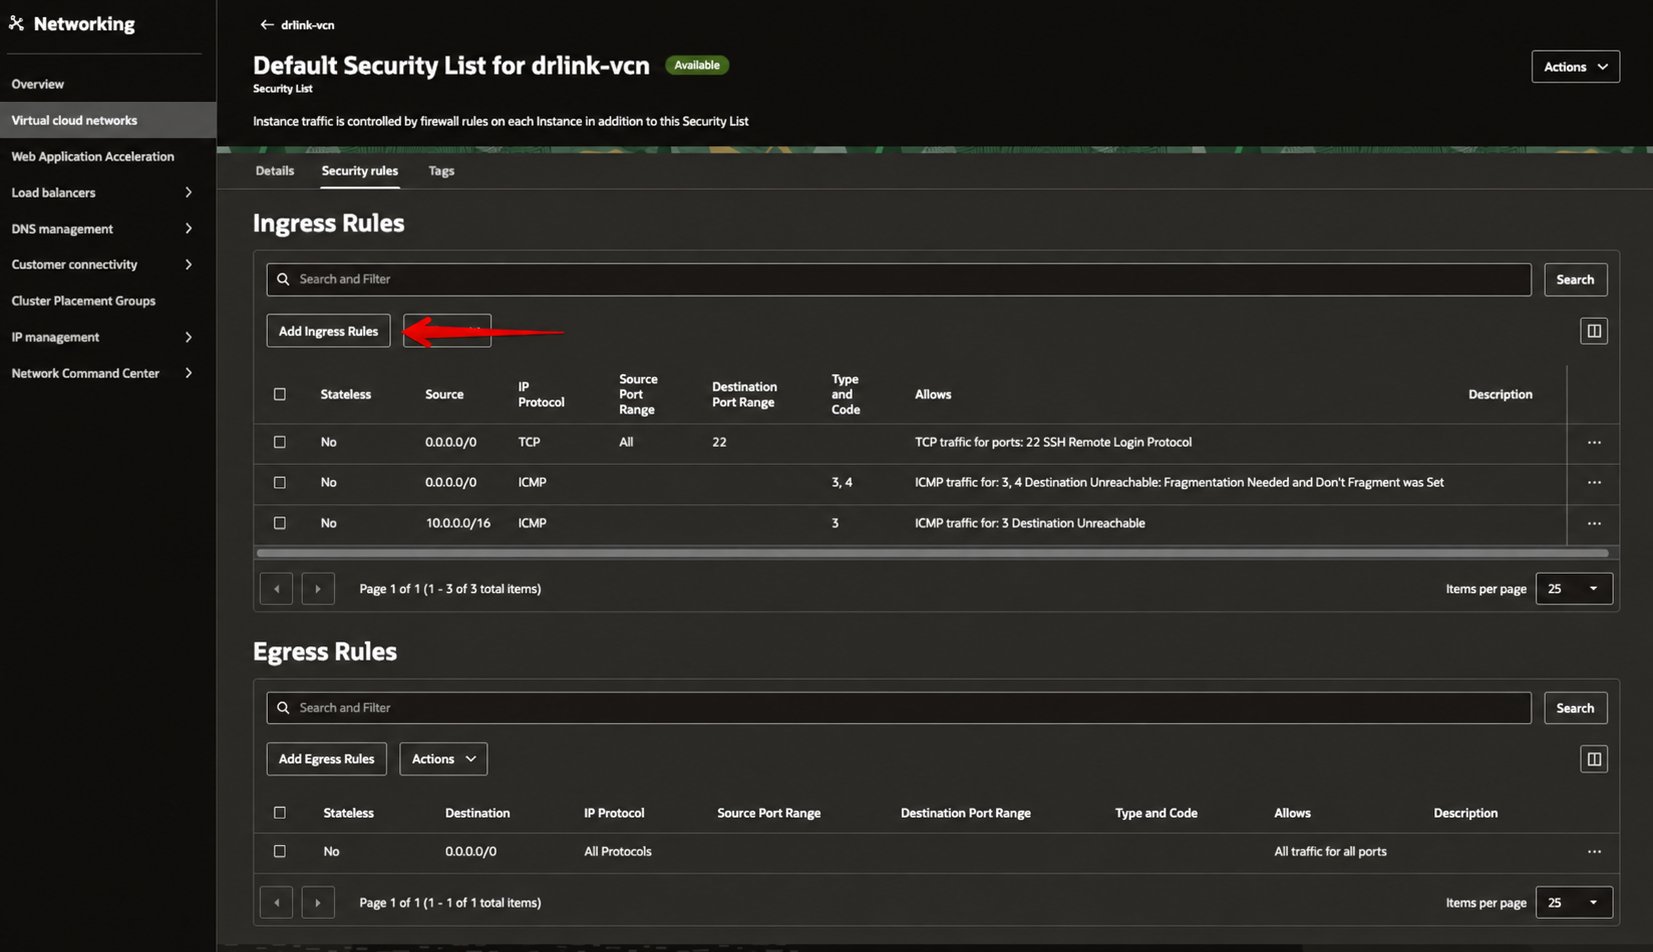
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/13.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=5a8fe95532c9fd593f76487632f8e76d" alt="Picture 13. Review the Default Security List ingress rules" width="1653" height="952" data-path="images/oci/13.png" />

For DataRelay Link in single-443 mode, add TCP 443 and the Remote Service endpoint pool TCP 6000-6098. Keep SSH 22 for administration, preferably restricted to your administrator public IP `/32`.
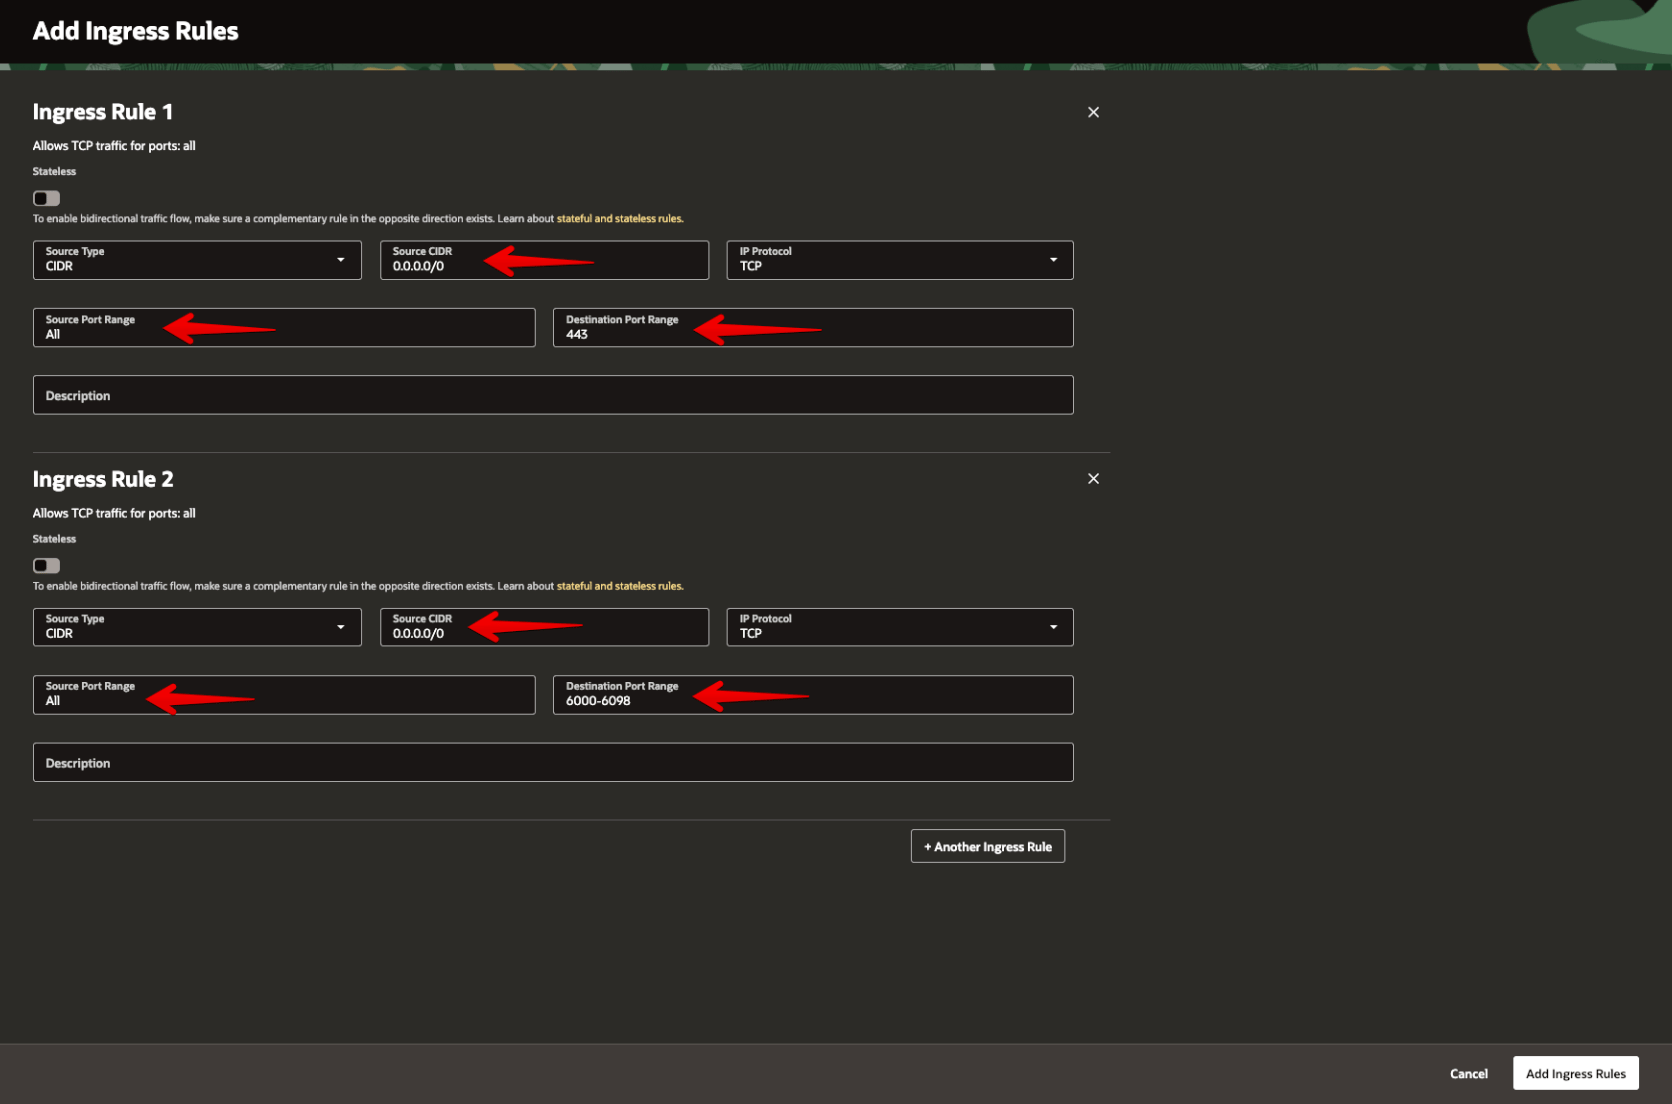
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/14.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=9bbda91395ec5c8a7e09c86e0f0a85db" alt="Picture 14. Add ingress rules for TCP 443 and TCP 6000-6098" width="1672" height="1104" data-path="images/oci/14.png" />

Confirm that the ingress rules were applied.
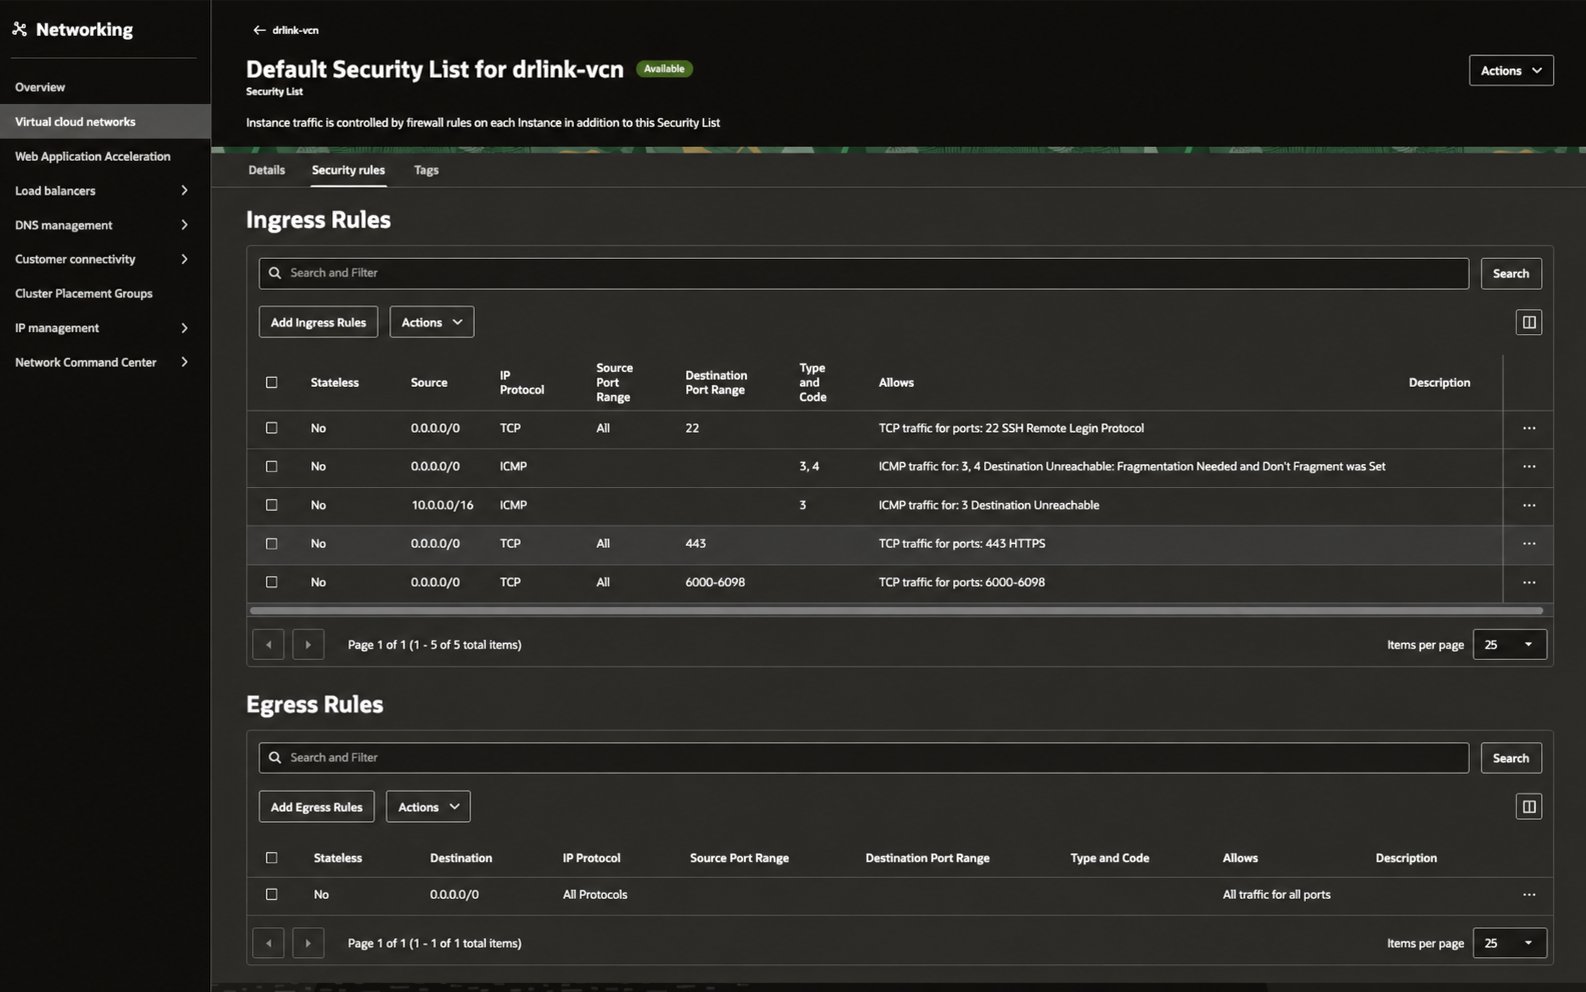
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/15.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=50c58a24384ea6446c589729e24f40cb" alt="Picture 15. Confirm the applied ingress rules" width="1586" height="992" data-path="images/oci/15.png" />

### Recommended single-443 ingress

| Protocol | Destination port | Source                                     | Purpose                             |
| -------- | ---------------: | ------------------------------------------ | ----------------------------------- |
| TCP      |               22 | **your admin public IP/32**                | SSH administration                  |
| TCP      |              443 | client networks or `0.0.0.0/0` if required | WSS control + enrollment/management |
| TCP      |        6000-6098 | only networks/users that need the services | Remote Services                     |

<Warning>
  In **single-443** mode, do not create public OCI ingress or DNAT for **6099** or **7000**. They are internal loopback backends. Also do not blindly copy a broad `All Protocols` rule from a generic OCI tutorial.
</Warning>

If you do not want the whole `6000-6098` range exposed, allow only the service ports that are actually assigned, and constrain source CIDRs where possible.

## 3. Create the Ubuntu compute instance

Recommended values for this walkthrough:

```text theme={null}
Name           data-relay-link-server
Image          Canonical Ubuntu 24.04 LTS x86_64
Shape          VM.Standard.E2.1.Micro (when Console marks it eligible/free)
VCN            data-relay-vcn
Subnet         data-relay-public-subnet
Boot volume    default
```

Before creating the Compute Instance, confirm that the VCN, Internet Gateway, route, public subnet, and Security List created above are ready, then open **Compute → Instances**.
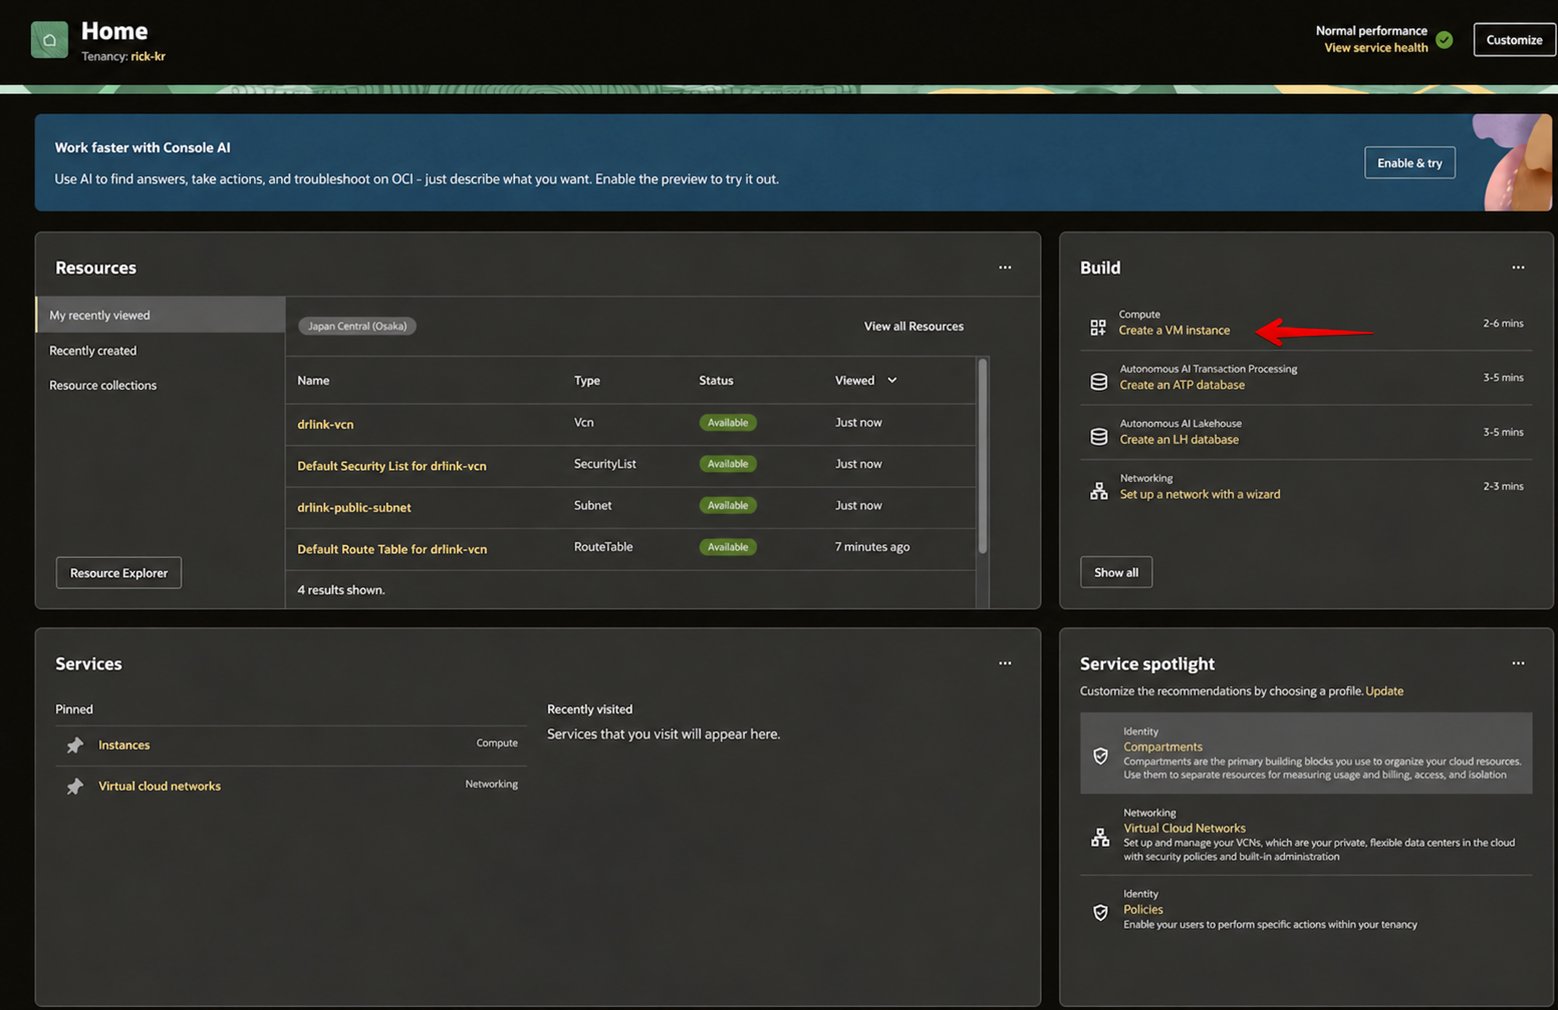
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/16.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=b10424c3645d35cc10dd1cf4352bf746" alt="Picture 16. Confirm the network resources and open Compute" width="1558" height="1010" data-path="images/oci/16.png" />

### 3-1. Enter the basic Compute Instance settings

Start on **Create compute instance** and confirm the instance name and placement.
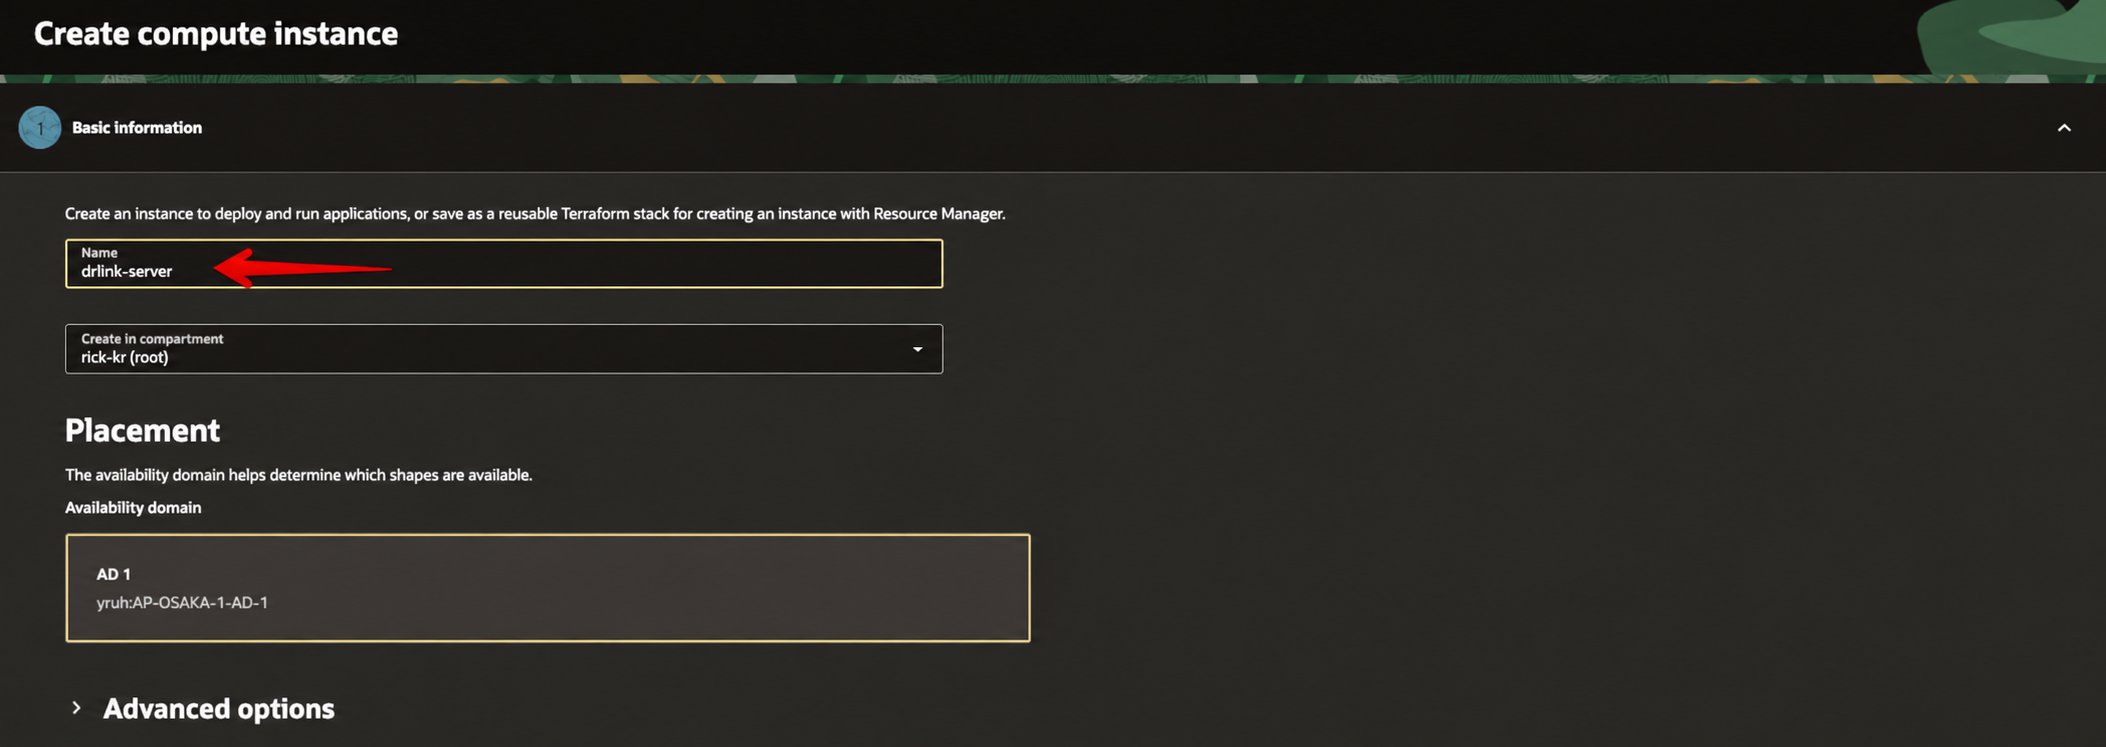
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/17.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=9a718e287e6bc7dc478cd5ca3a9a8078" alt="Picture 17. Compute Instance basic settings" width="2106" height="747" data-path="images/oci/17.png" />

### 3-2. Select Canonical Ubuntu 24.04

Choose **Change image** and select Canonical Ubuntu 24.04. Treat the image/version currently shown in OCI Console as authoritative.
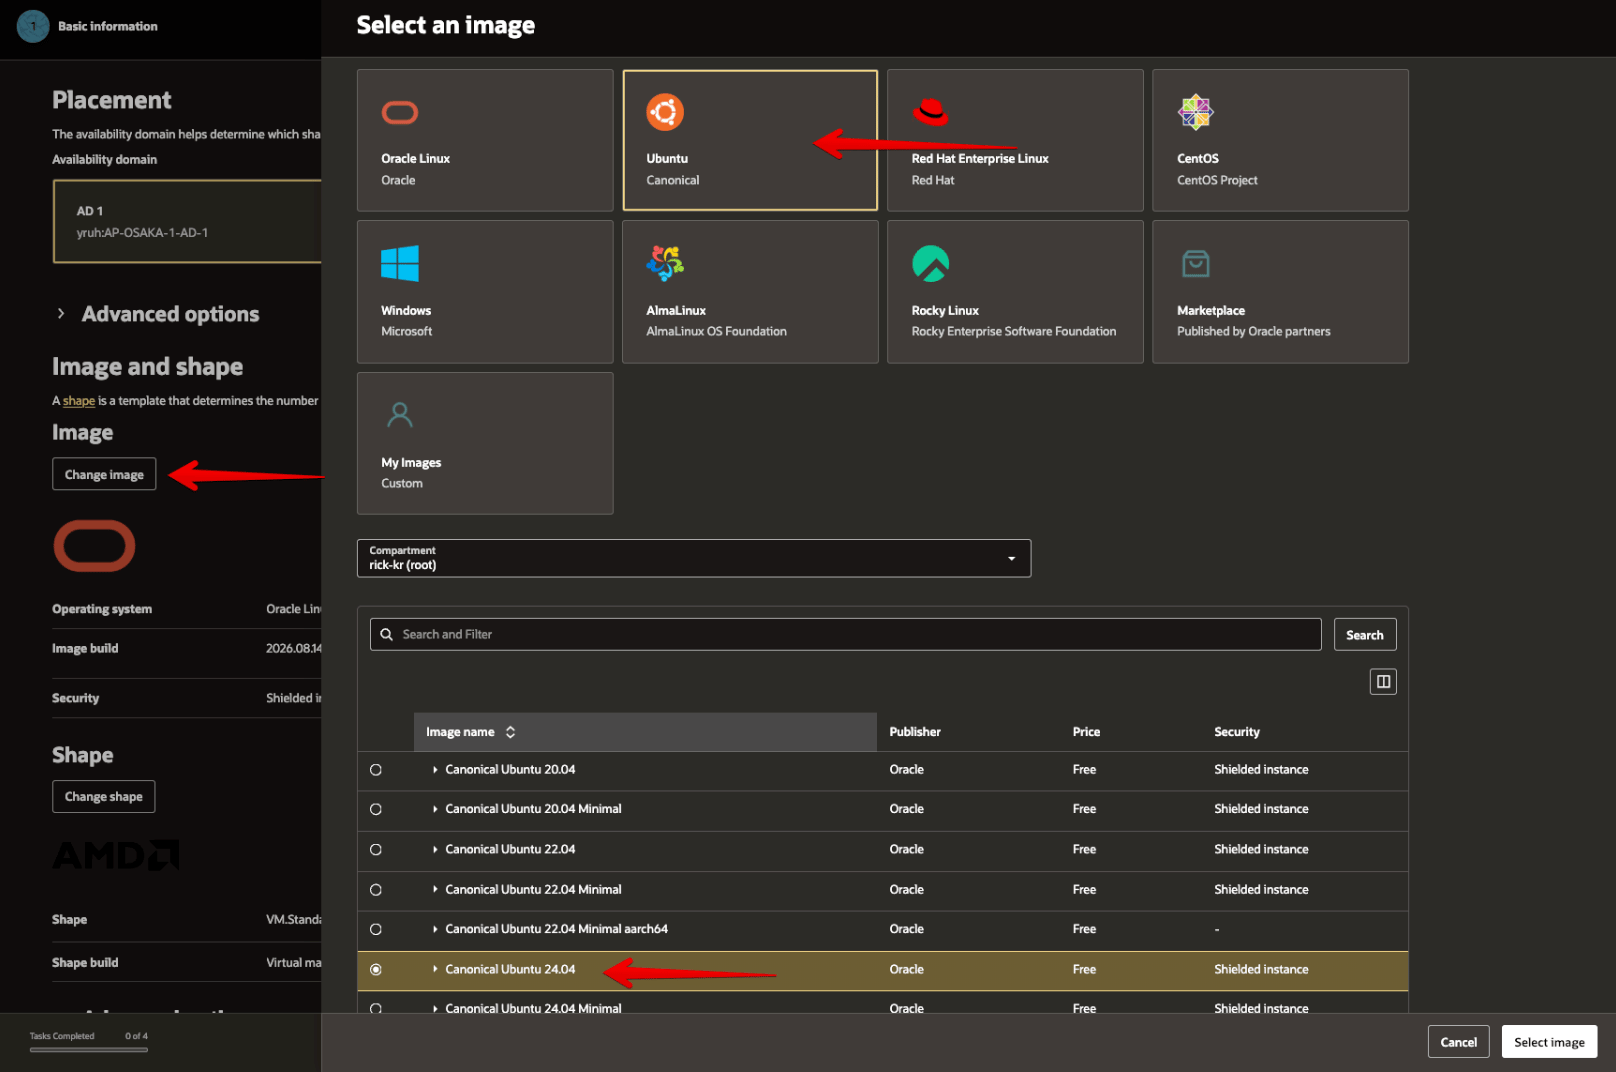
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/18.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=5918ecc8fa6c7f8584cca46ecd47066e" alt="Picture 18. Select the Ubuntu image" width="1616" height="1072" data-path="images/oci/18.png" />

Unless your environment requires something different, keep the Security settings at their defaults.
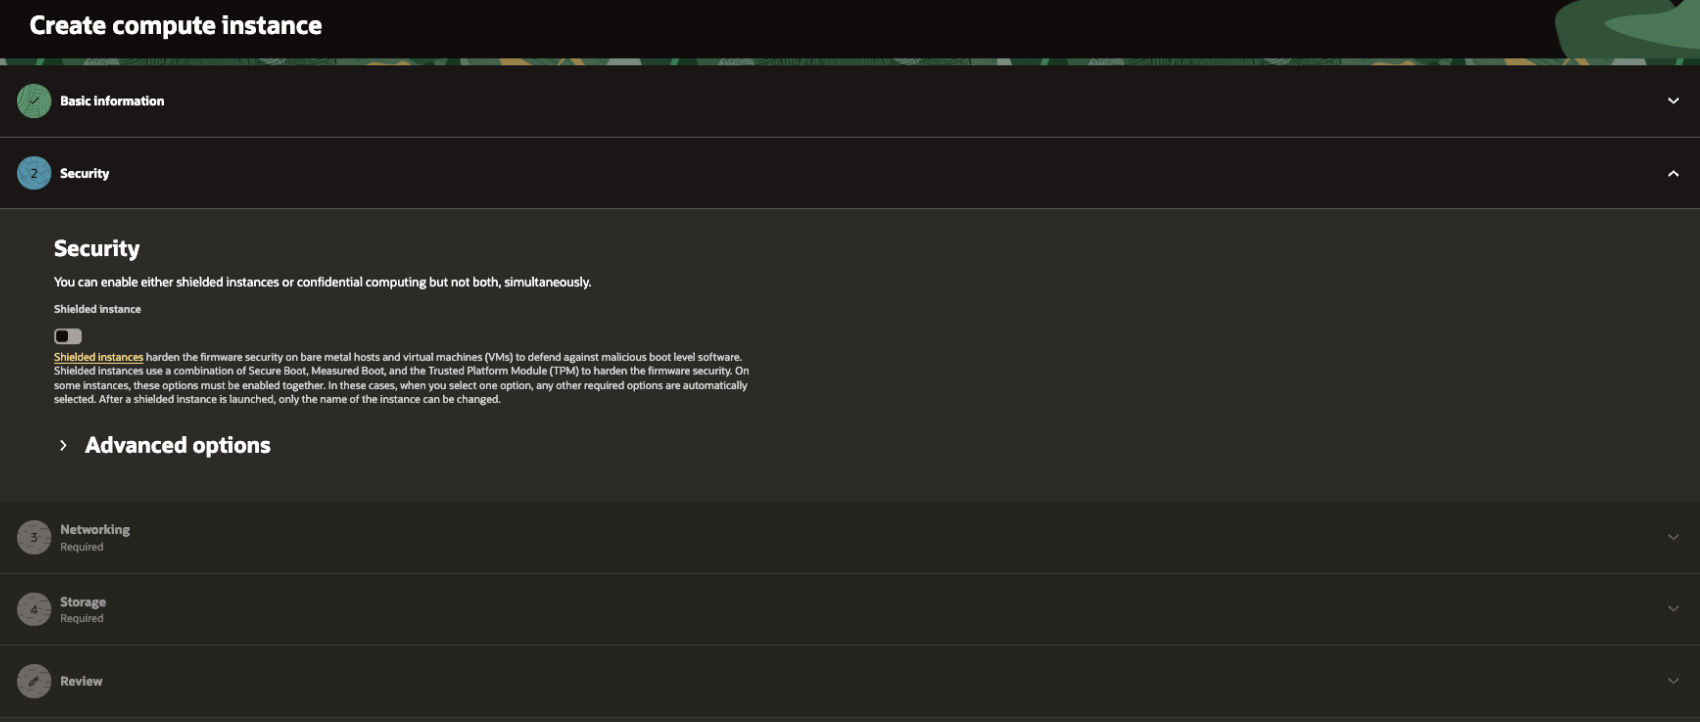
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/19.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=f958375e4fca2e72f8502367a4e59aae" alt="Picture 19. Security settings - use the defaults unless required otherwise" width="1700" height="722" data-path="images/oci/19.png" />

### 3-3. Select the VCN and public subnet

Under Primary VNIC, select the `data-relay-vcn` and `data-relay-public-subnet` created earlier.
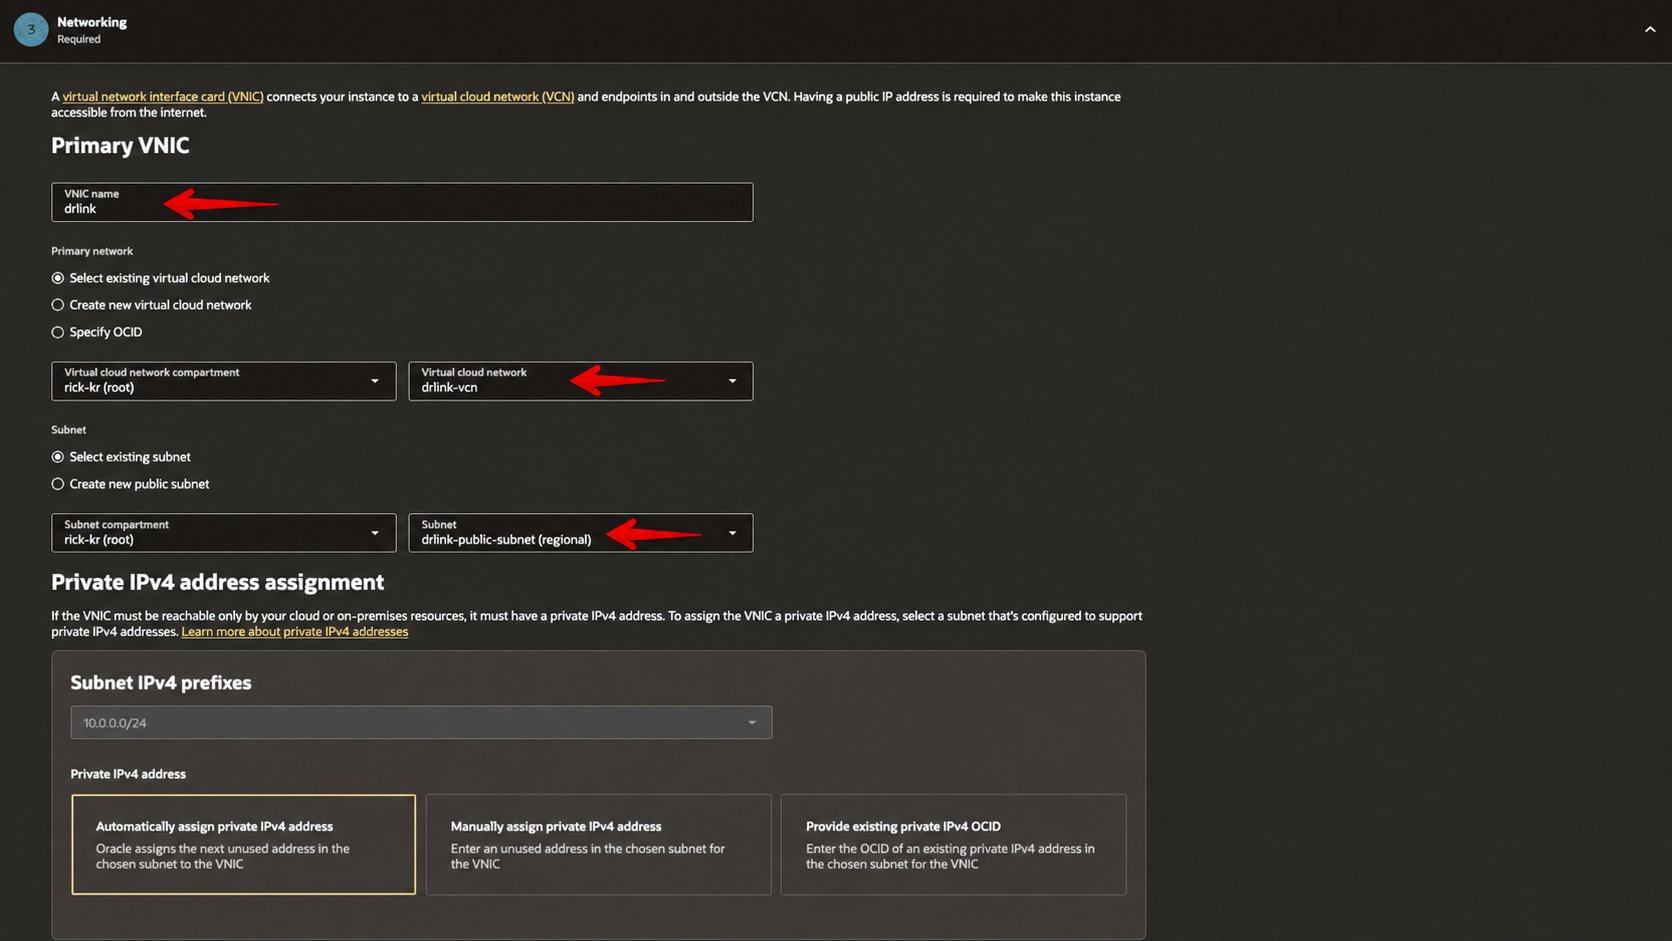
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/20.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=79c6b89d7a584dd9810a3724a5afe74f" alt="Picture 20. Select the existing data-relay-vcn and data-relay-public-subnet" width="1672" height="941" data-path="images/oci/20.png" />

### 3-4. Disable automatic public IPv4 and configure the SSH key

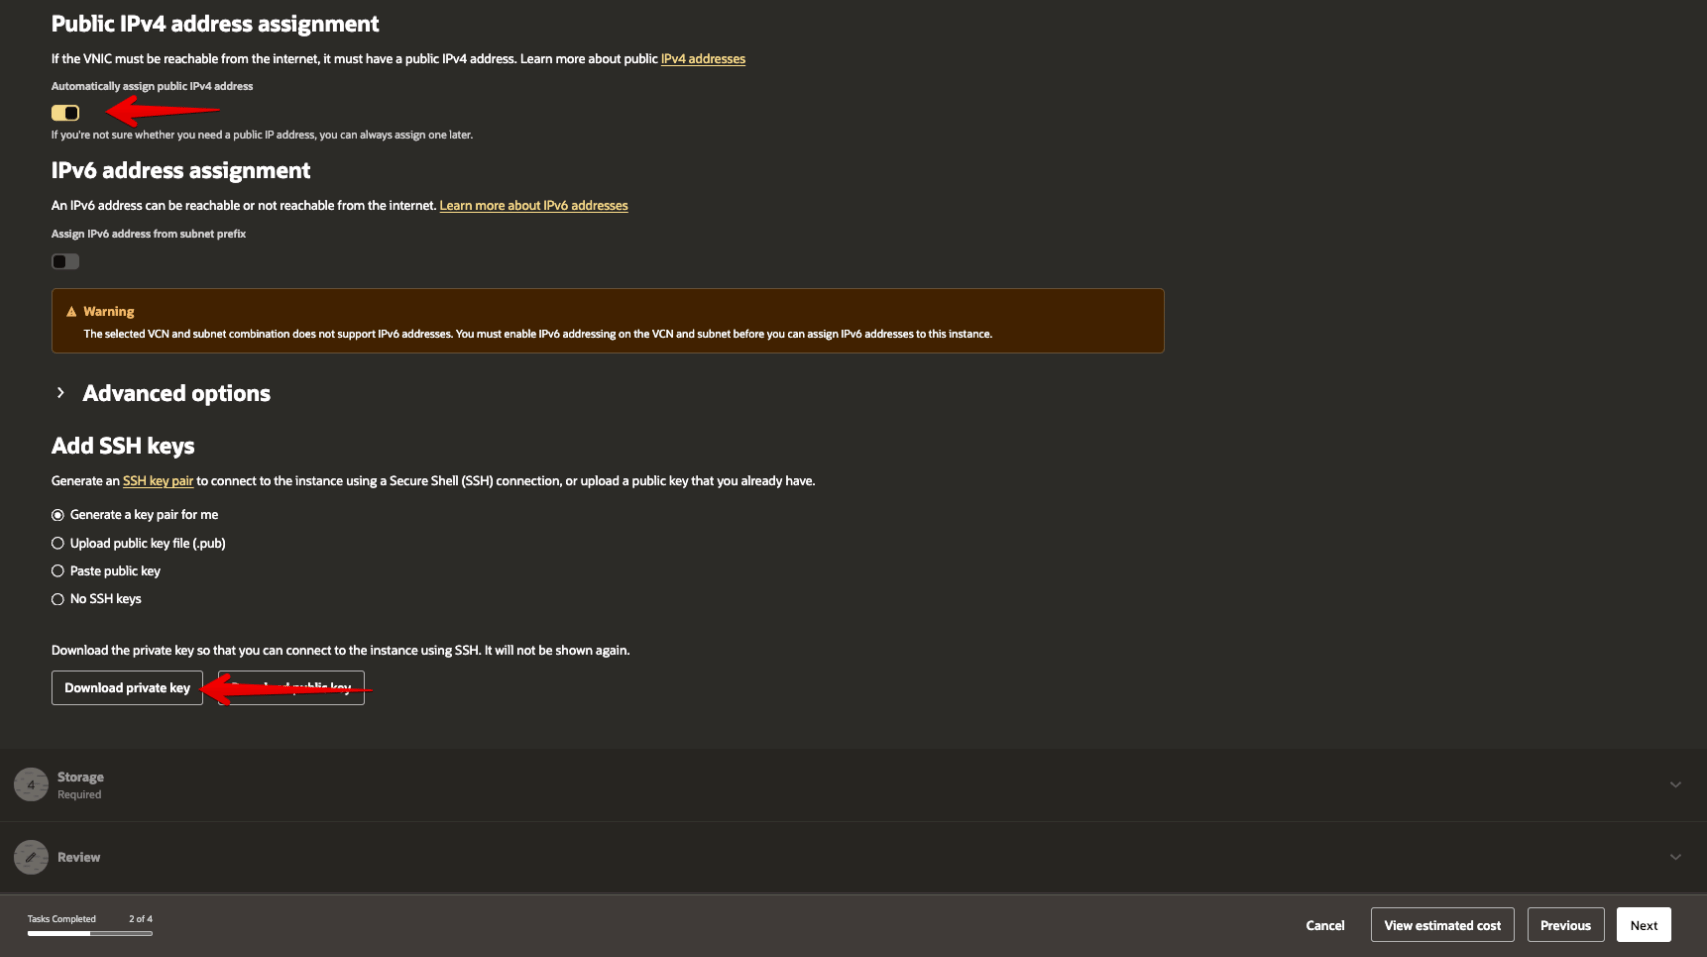
Because this guide attaches a Reserved Public IP later, turn off **Automatically assign public IPv4 address**. Then upload an existing SSH public key or let OCI generate a new key pair, and store the private key securely.
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/21.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=b24ff9d6608b23619edda24a2959e0a9" alt="Picture 21. Disable automatic public IPv4 and create/download the SSH key" width="1707" height="957" data-path="images/oci/21.png" />

### 3-5. Review the boot volume

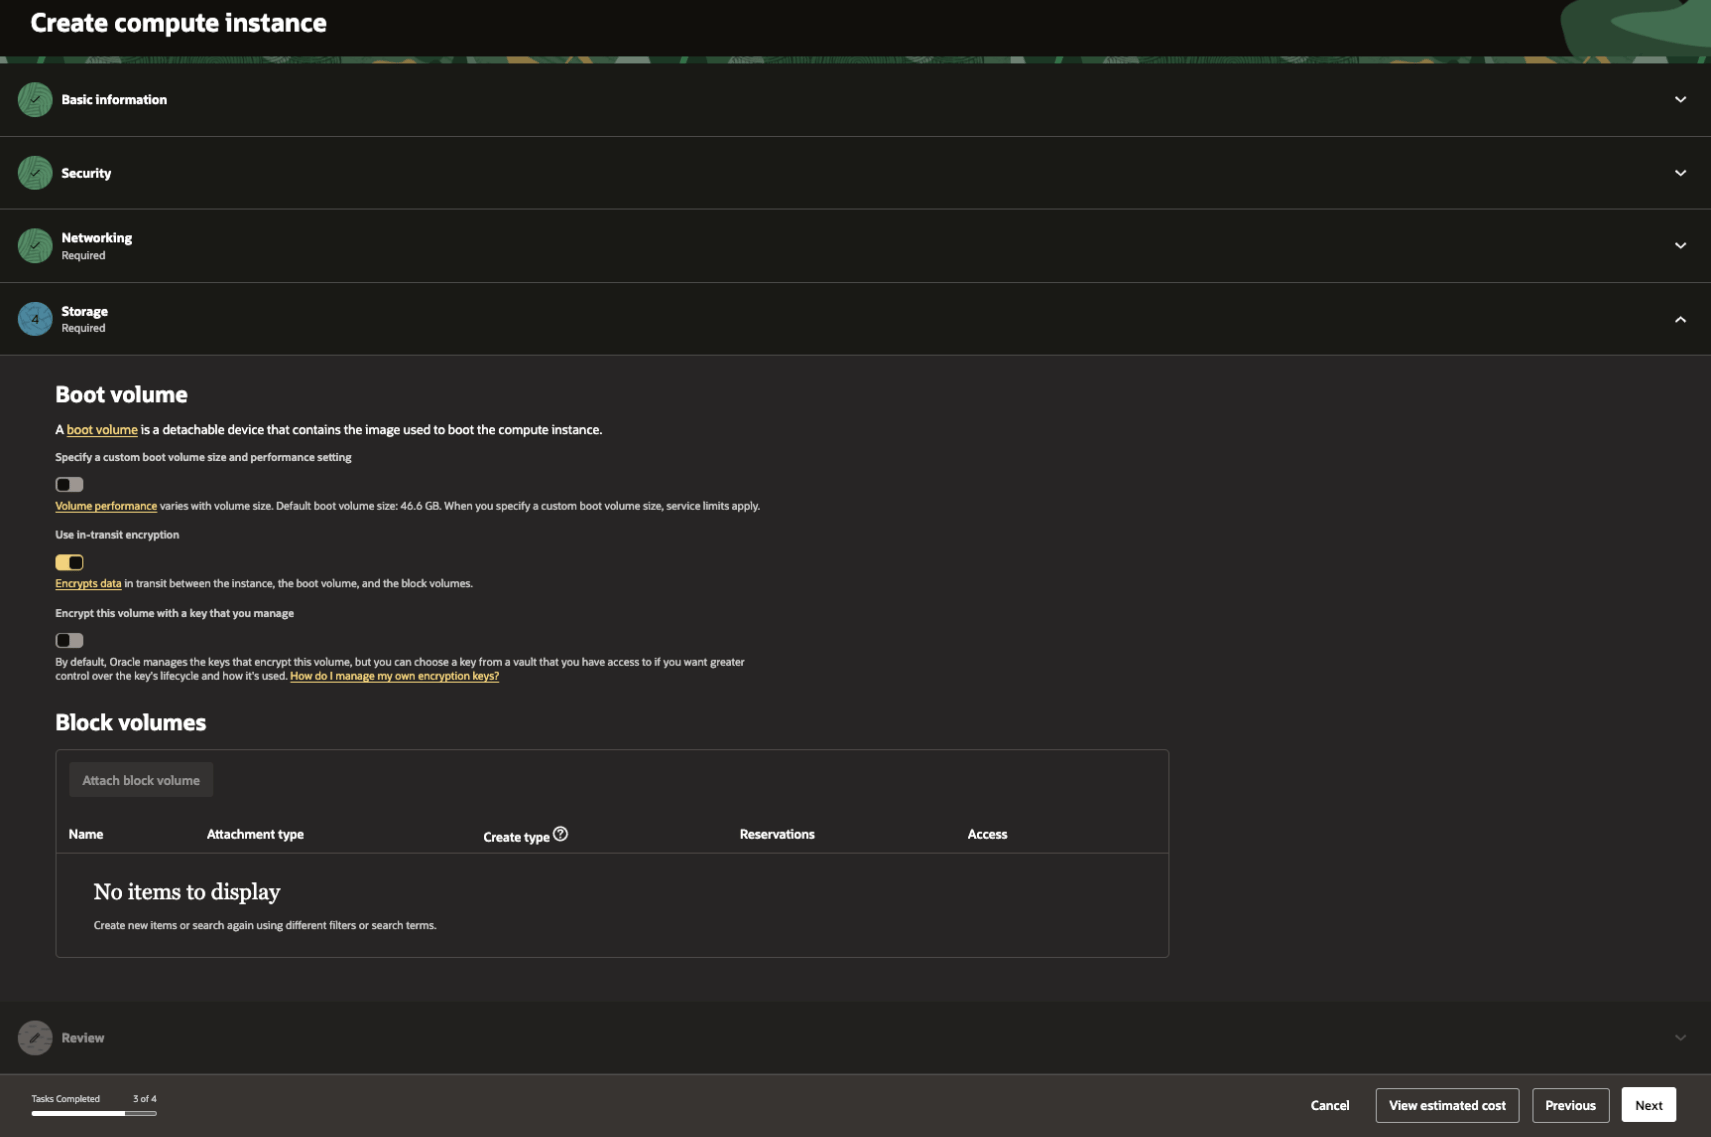
Unless you have a separate storage requirement, keep the boot-volume settings at their defaults.
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/22.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=40cb0b8bce30a32aeec48d60a1519185" alt="Picture 22. Boot Volume settings - keep the defaults unless required otherwise" width="1711" height="1137" data-path="images/oci/22.png" />

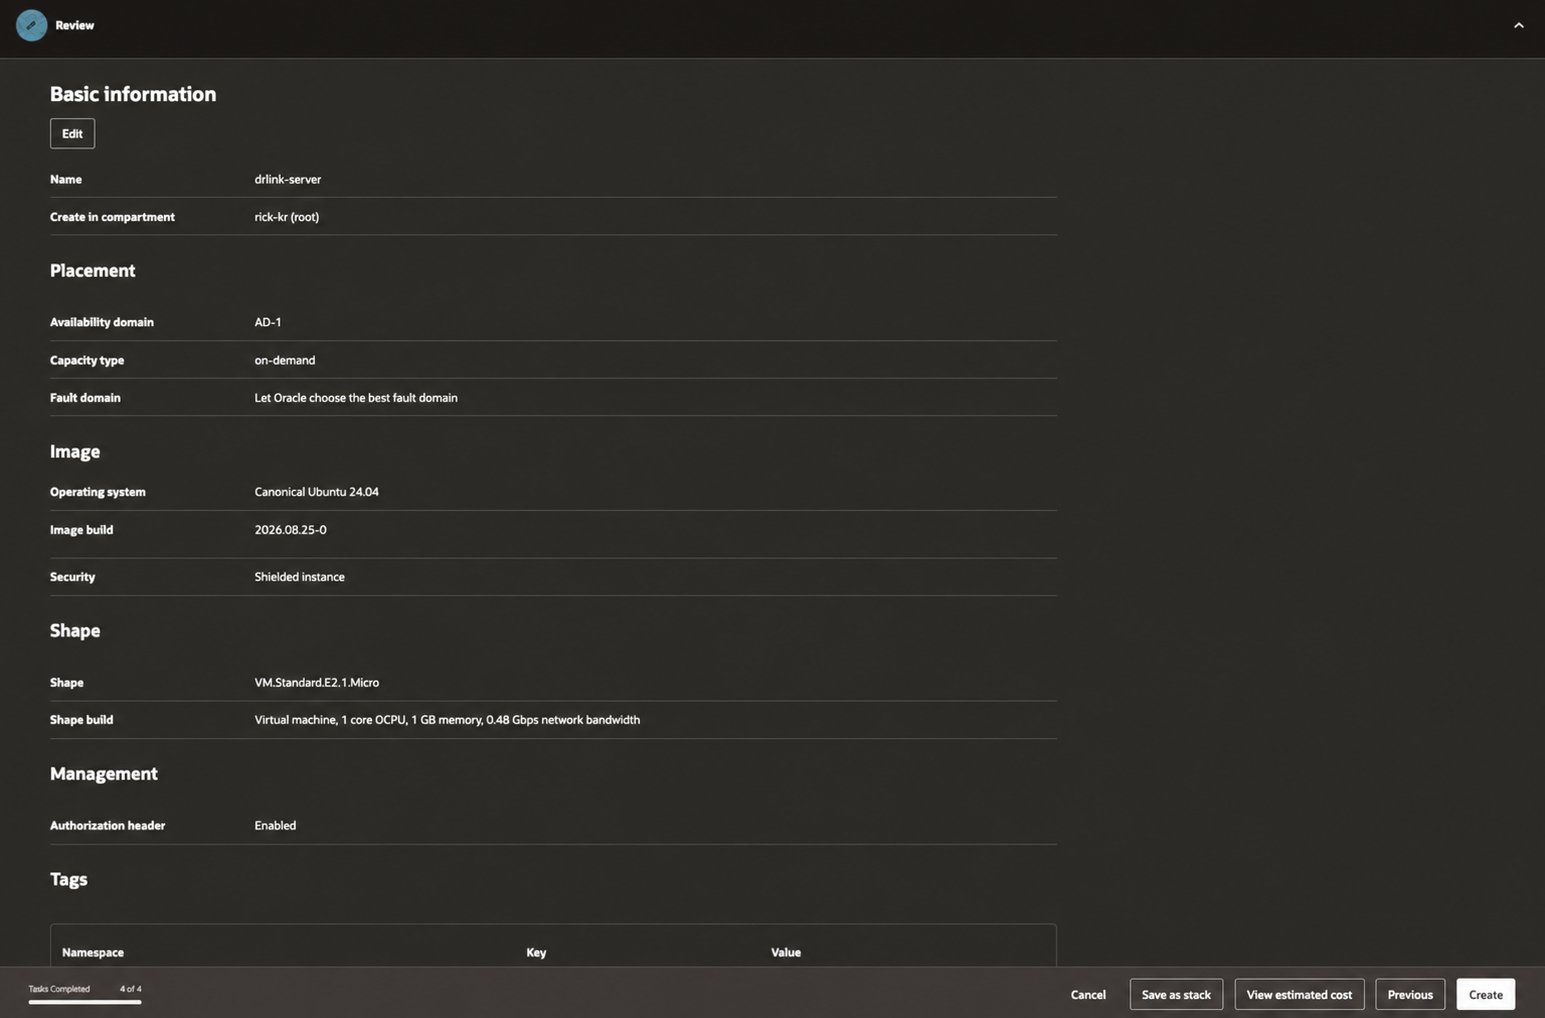
### 3-6. Review before creating the instance

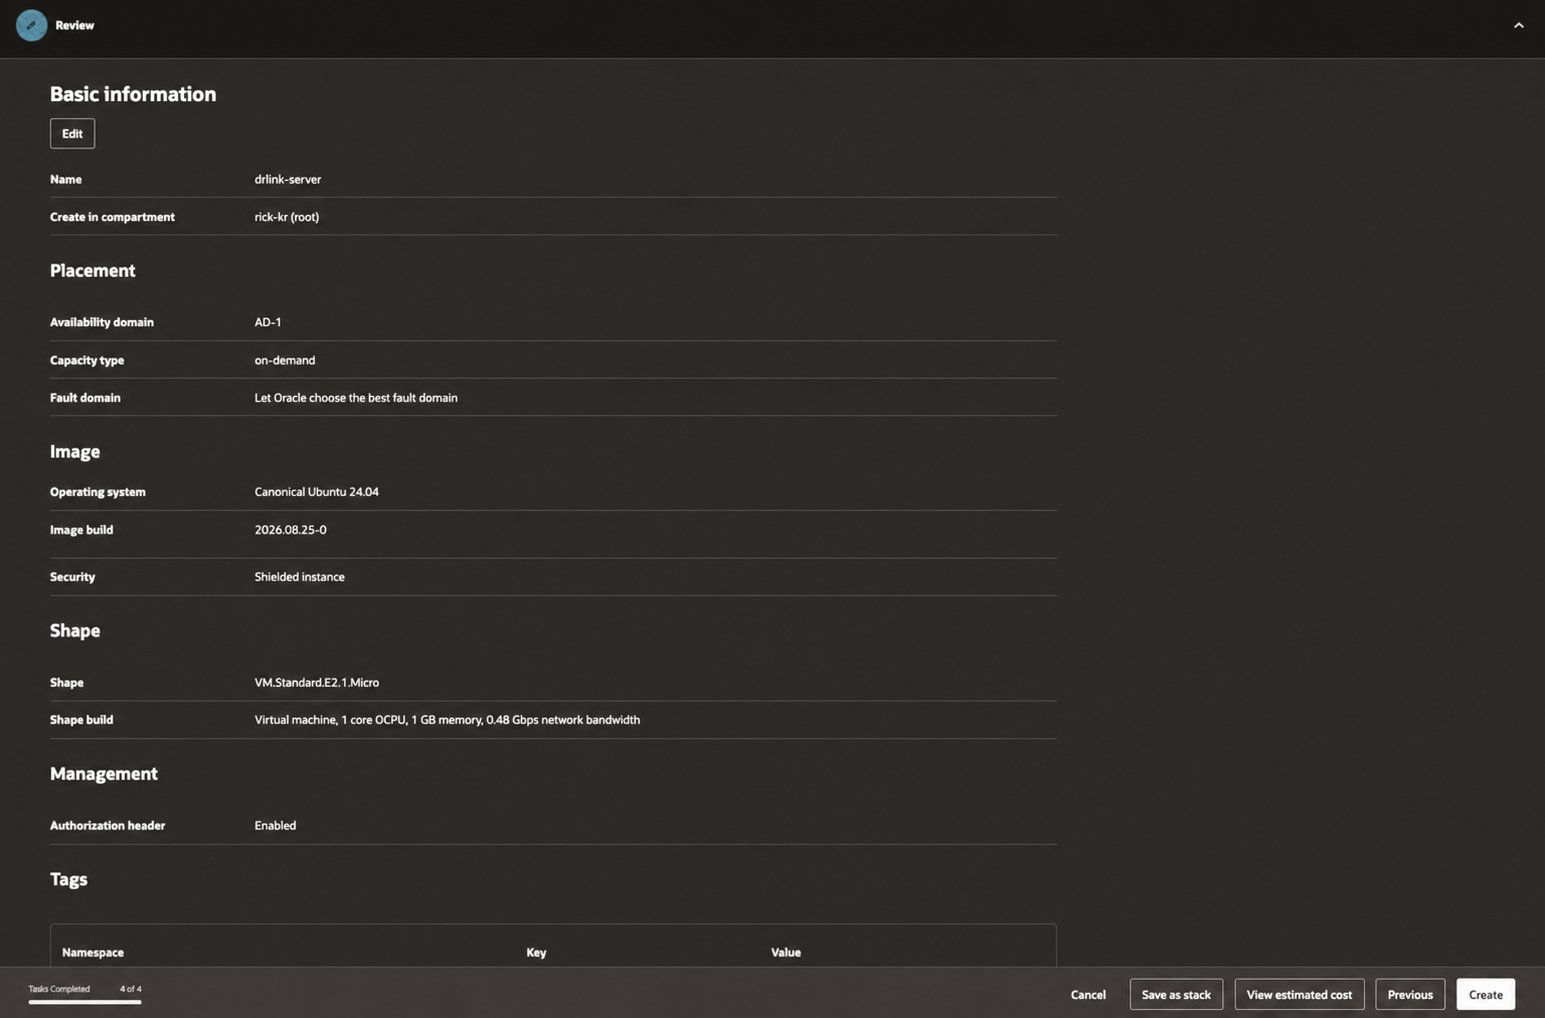
Confirm that the image is Ubuntu 24.04 and that the shape, VCN/subnet, and SSH key match the intended configuration before creating the instance.
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/23.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=e35e72d36e54e2c9a4aedf4fca9a7940" alt="Picture 23. Review the Ubuntu 24.04 and VM.Standard.E2.1.Micro configuration" width="1545" height="1018" data-path="images/oci/23.png" />

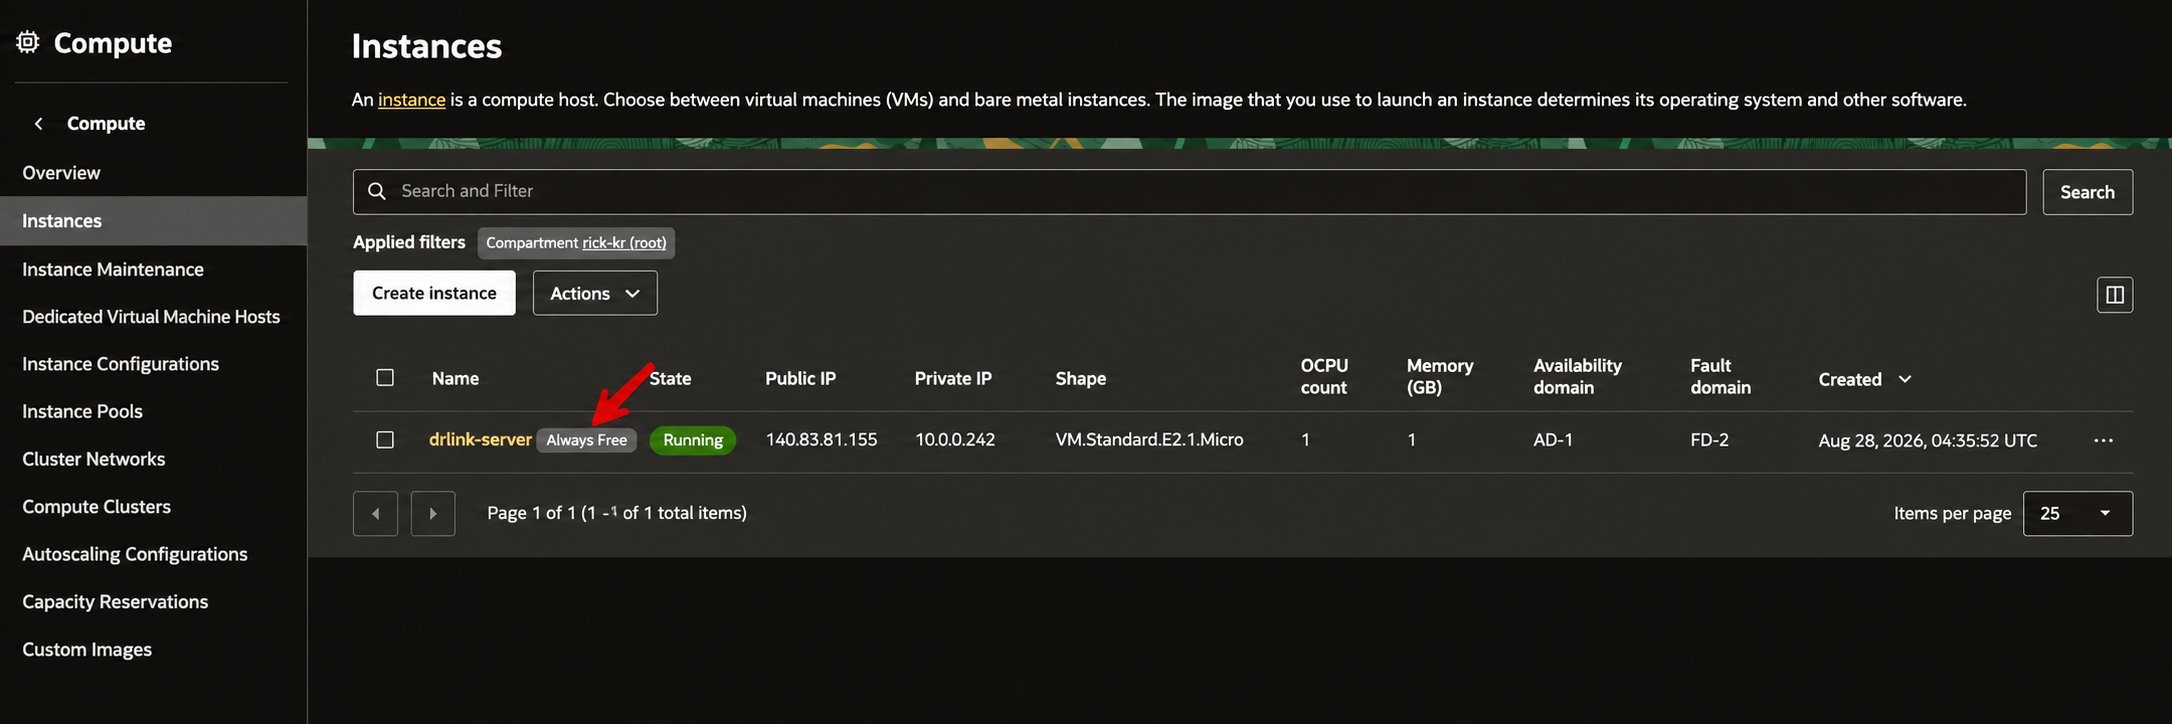
### 3-7. Confirm the created instance and Free/Eligible indicator

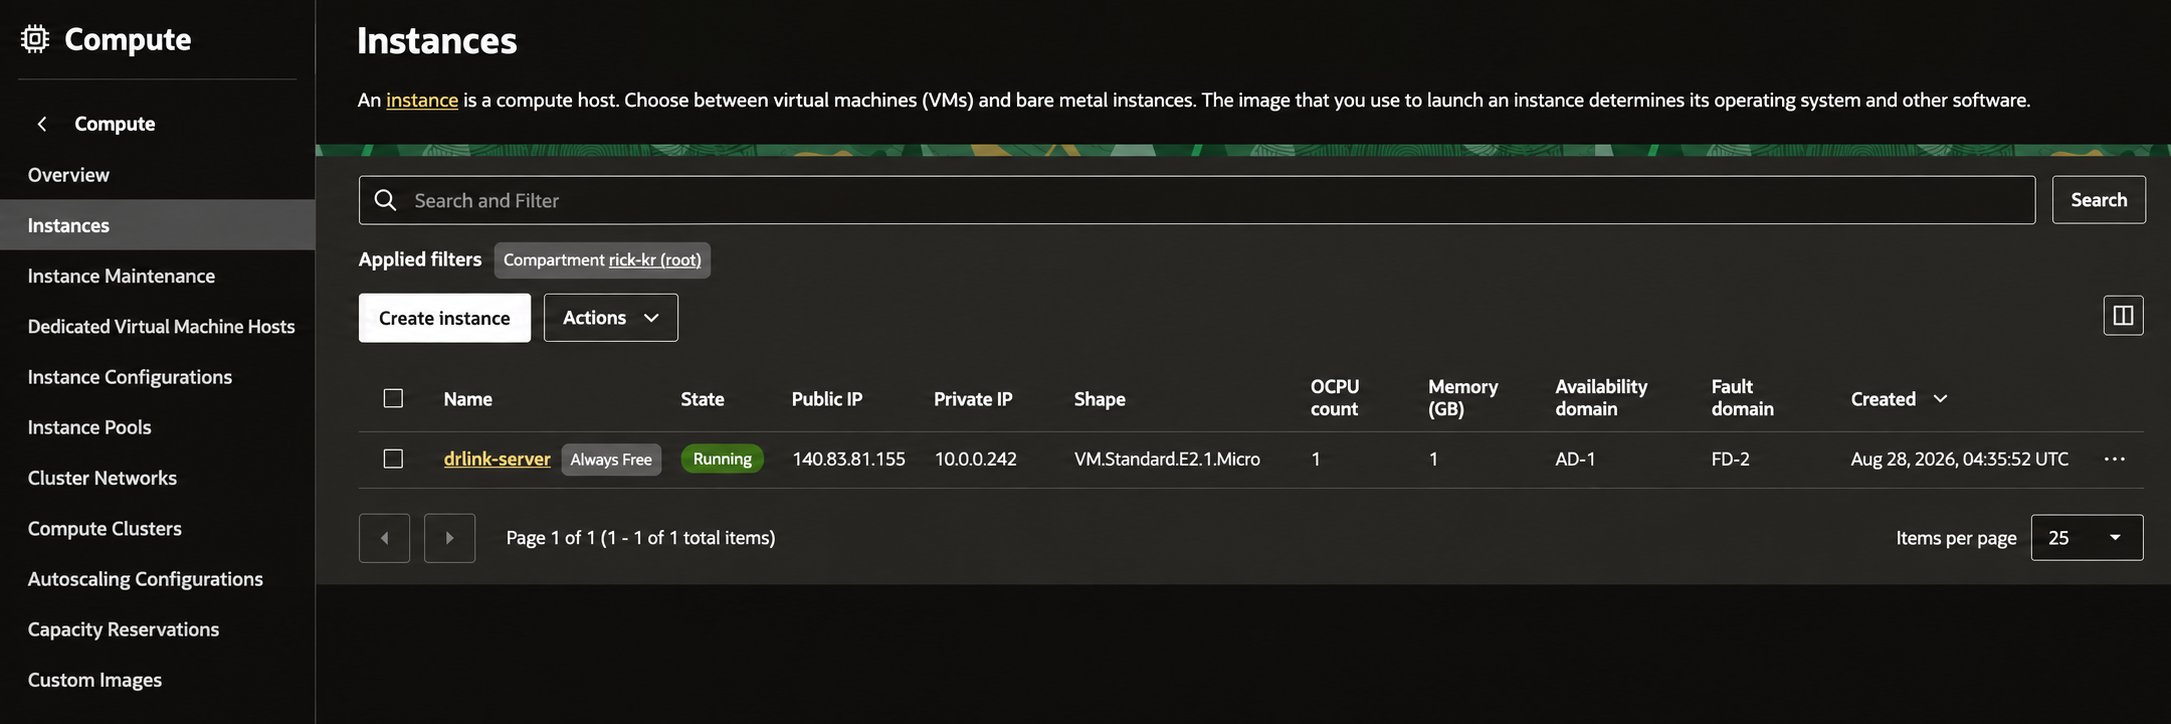
Confirm the instance state in the Compute Instances list.
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/24.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=c0831d6cda98ed948cdfac5b5c5e47ce" alt="Picture 24. Confirm the created instance in the instance list" width="2171" height="724" data-path="images/oci/24.png" />

The **Always Free** indicator shown in the original screenshot reflects the OCI Console at the time of the field deployment. Current Free Tier/Eligible status can vary by region and tenancy, so use the current Console's eligibility and cost display as the final authority.
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/25.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=31873aaef1d307e48242582b133bbd61" alt="Picture 25. Confirm the Always Free indicator and select the created instance" width="2172" height="724" data-path="images/oci/25.png" />

Important points from the original deployment:

* choose the existing `data-relay-vcn`
* choose `data-relay-public-subnet`
* allow OCI to assign the **private IPv4** automatically
* turn off **Automatically assign public IPv4 address** for the final persistent-IP design
* generate/download or upload an SSH public key
* if OCI generated the key pair, store the private key securely; do not assume it can be downloaded again later
* keep the boot volume simple unless you have another storage requirement

<Warning>
  `VM.Standard.E2.1.Micro` availability and Free Tier treatment are tenancy/region dependent. If the Console does not show it as eligible at creation time, do not assume this guide makes it free.
</Warning>

## 4. Attach a Reserved Public IPv4

From the instance details page, open **Networking → Primary VNIC**.
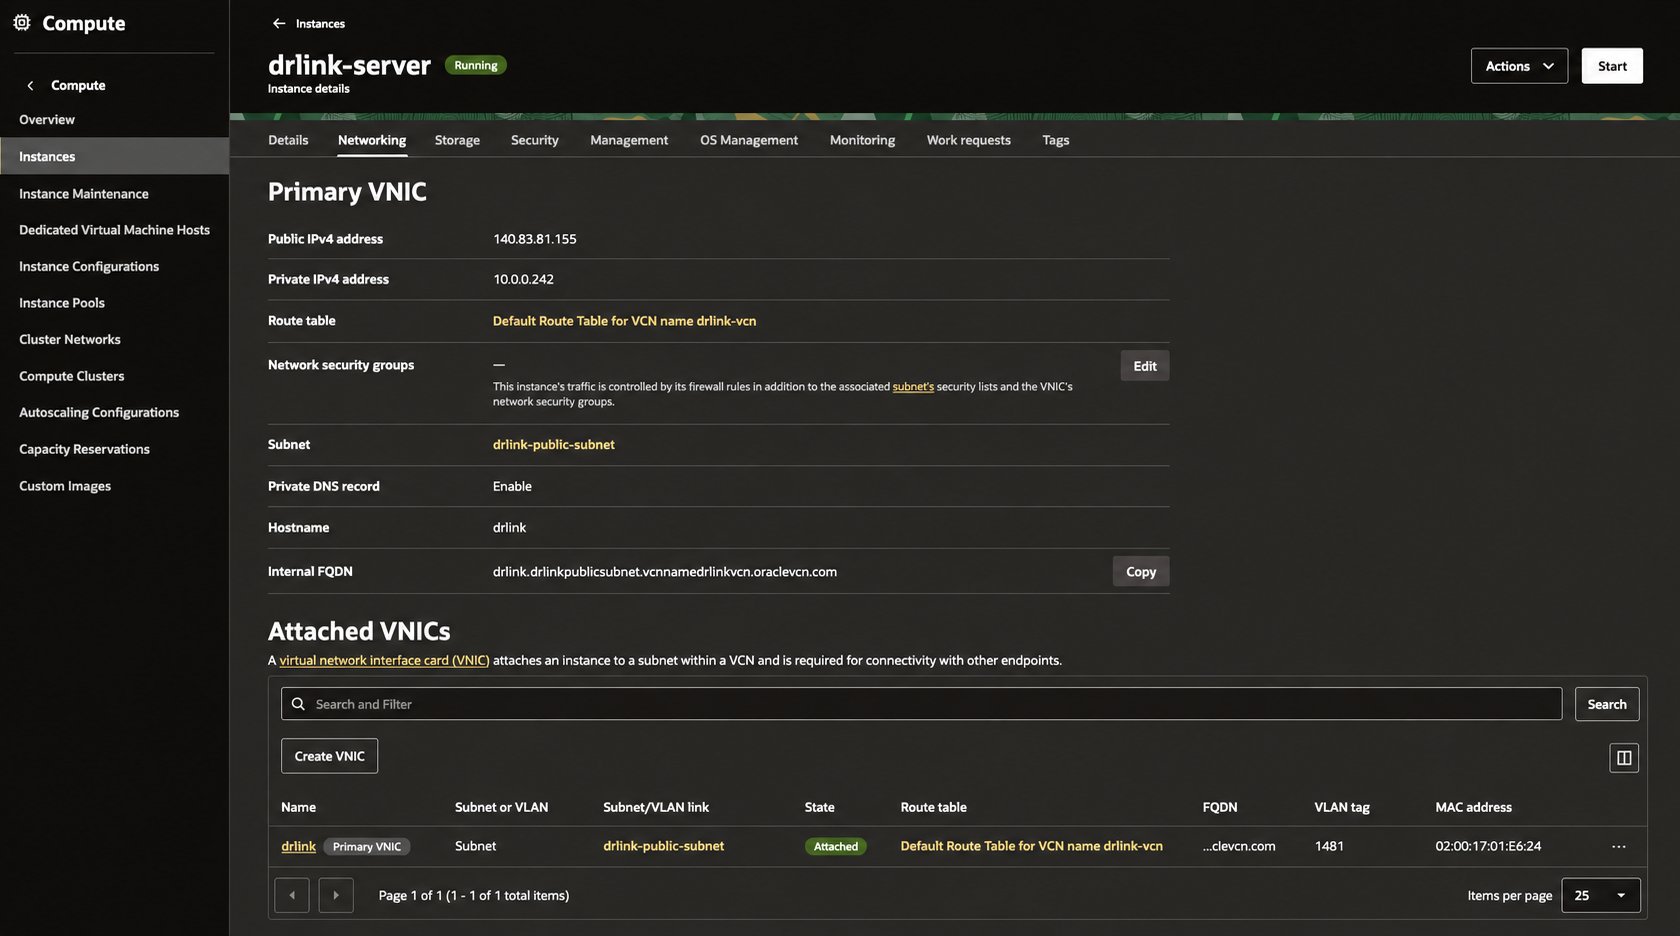
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/26.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=15760bc61d004be7f2e296d9b676390f" alt="Picture 26. Open the instance Networking page and Primary VNIC" width="1680" height="936" data-path="images/oci/26.png" />

In the VNIC, open **IP administration → Primary Private IP**.
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/27.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=d4270cae474e9315157ae439ac6e8866" alt="Picture 27. Open VNIC IP administration and the Primary Private IP" width="1545" height="1018" data-path="images/oci/27.png" />

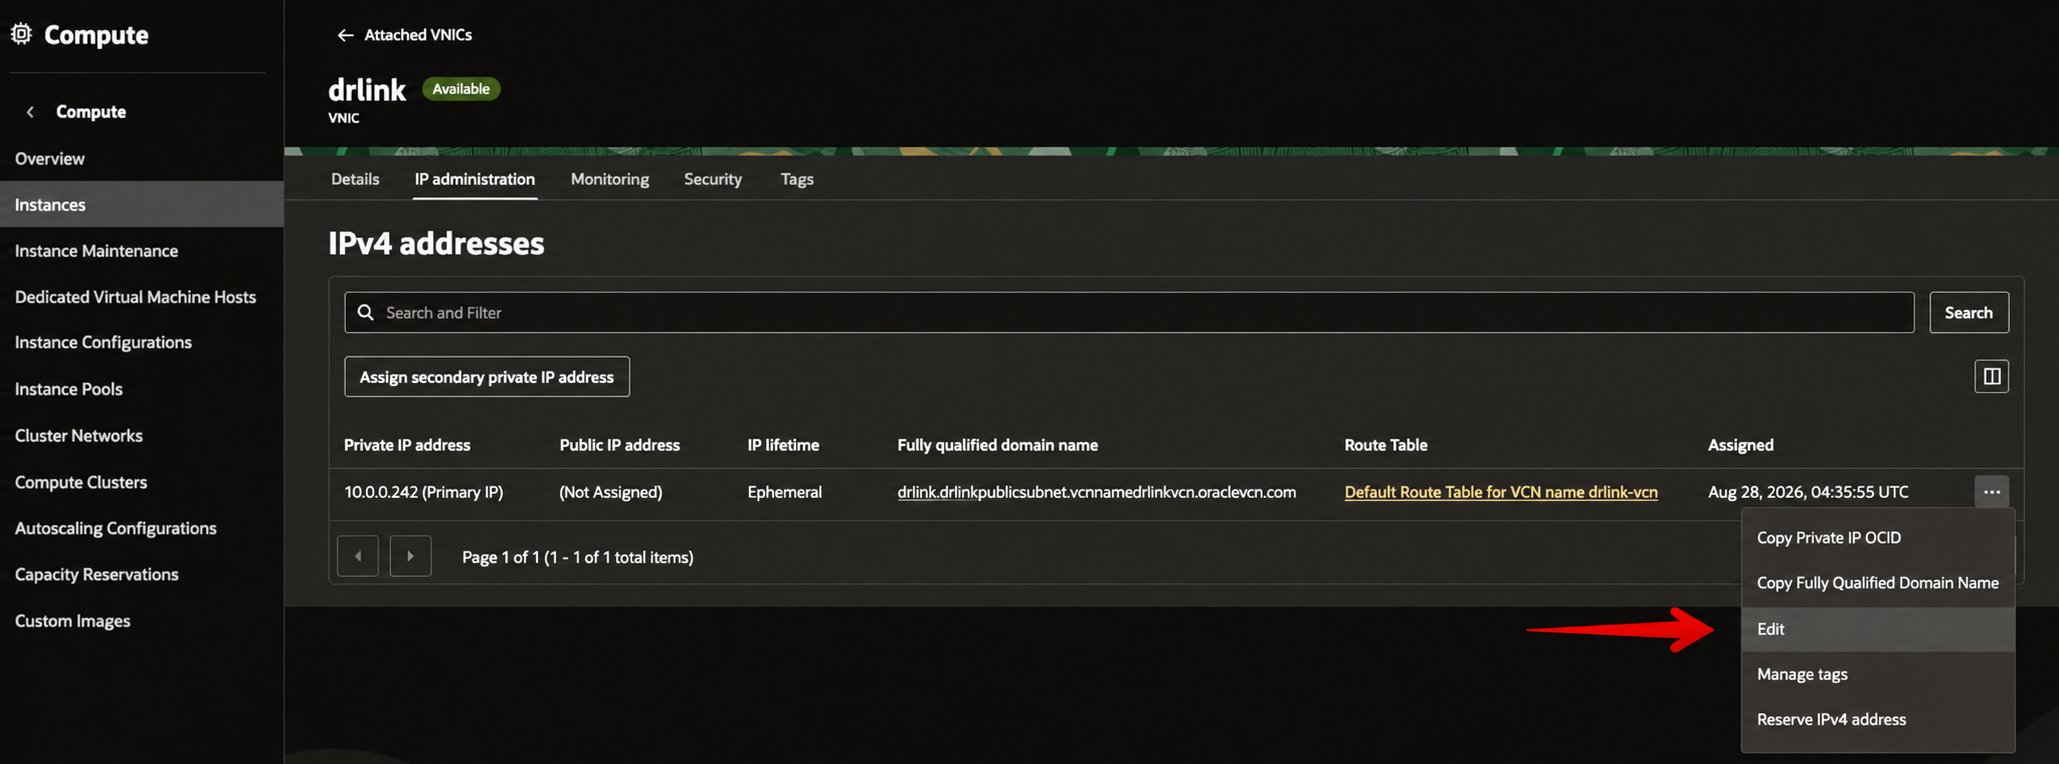
If an ephemeral public IP is currently attached, edit the private IP and select **No public IP** first.
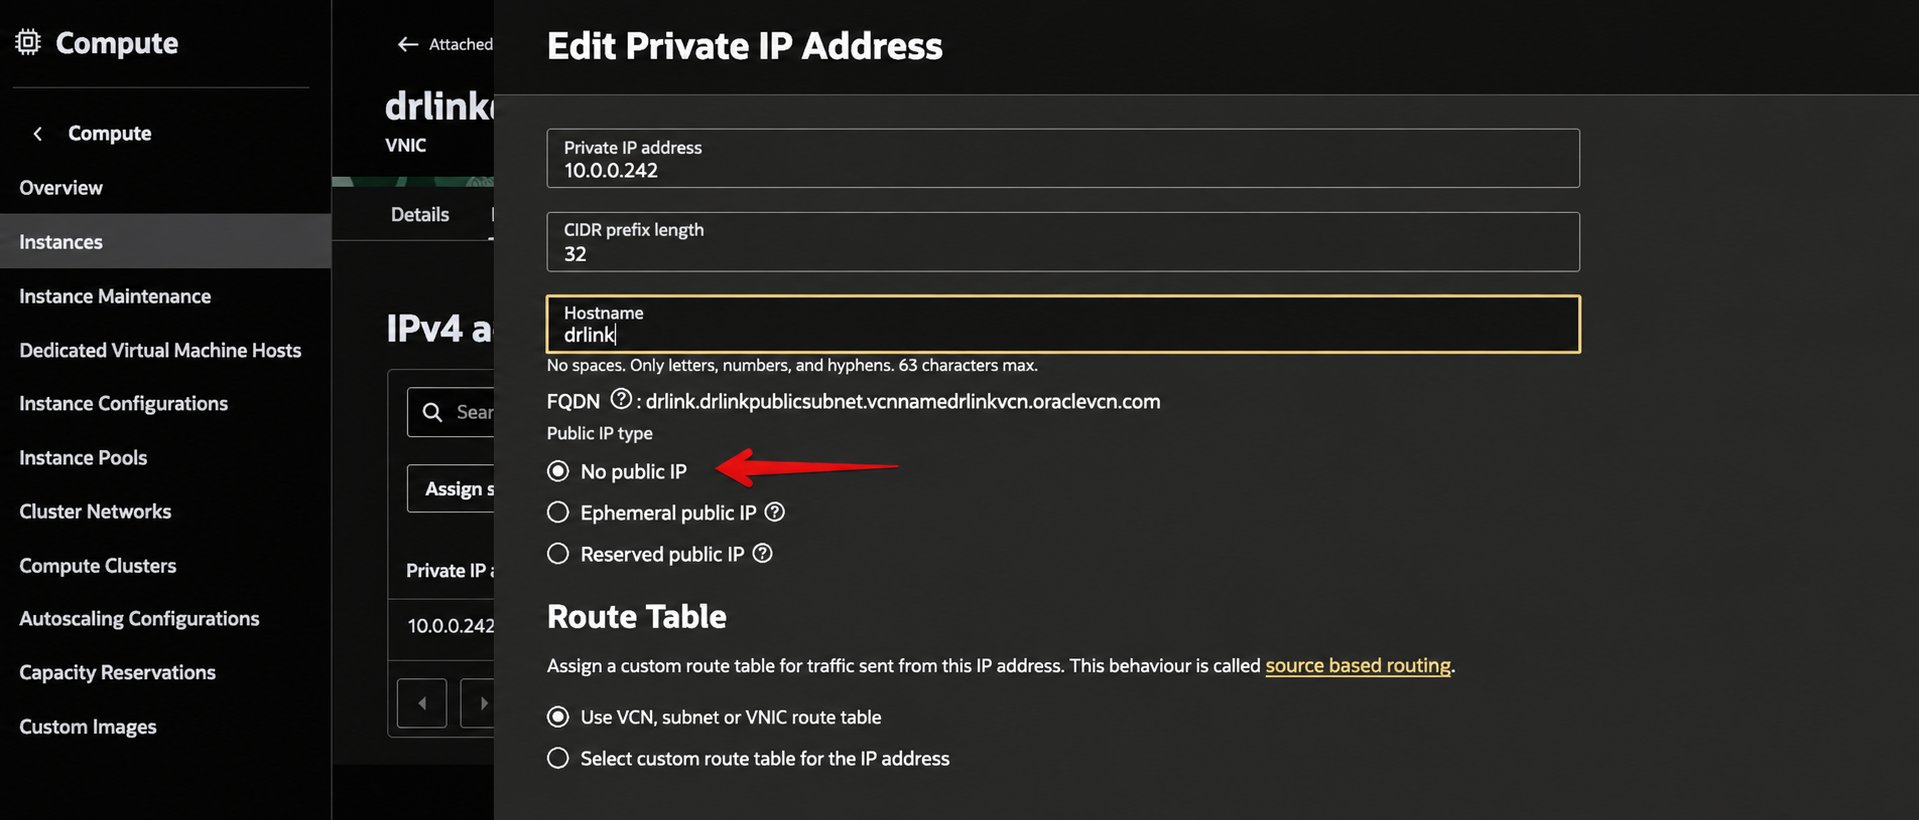
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/28.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=59c4abefe71b958ca16238b8316fee70" alt="Picture 28. Select No public IP in Edit Private IP Address" width="1919" height="820" data-path="images/oci/28.png" />

Confirm that no public IP is currently assigned.
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/29.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=544dc609eac909473846bb8130b7f43b" alt="Picture 29. Confirm that the public IP is unassigned" width="2059" height="764" data-path="images/oci/29.png" />

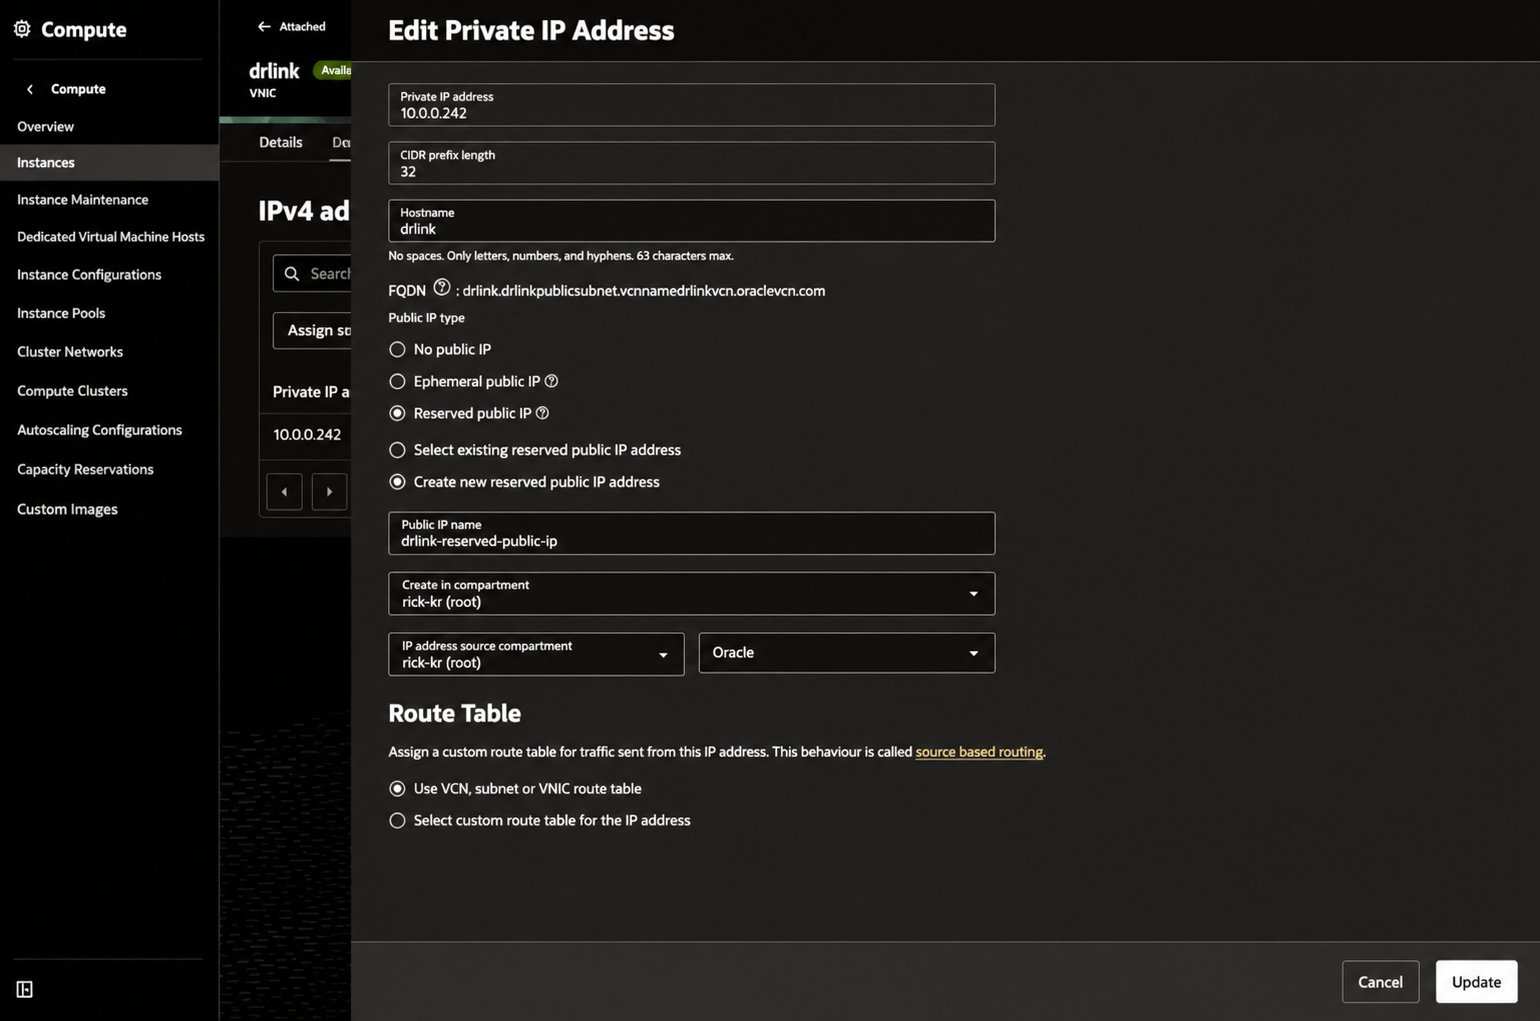
Edit the private IP again and choose:

```text theme={null}
Public IP type        Reserved public IP
Option                Create new Reserved IP Address
Name                  data-relay-reserved-public-ip
```
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/30.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=81dc02eefac188ccbe350d7b04b7d3dd" alt="Picture 30. Create and attach a new Reserved Public IP" width="1540" height="1021" data-path="images/oci/30.png" />

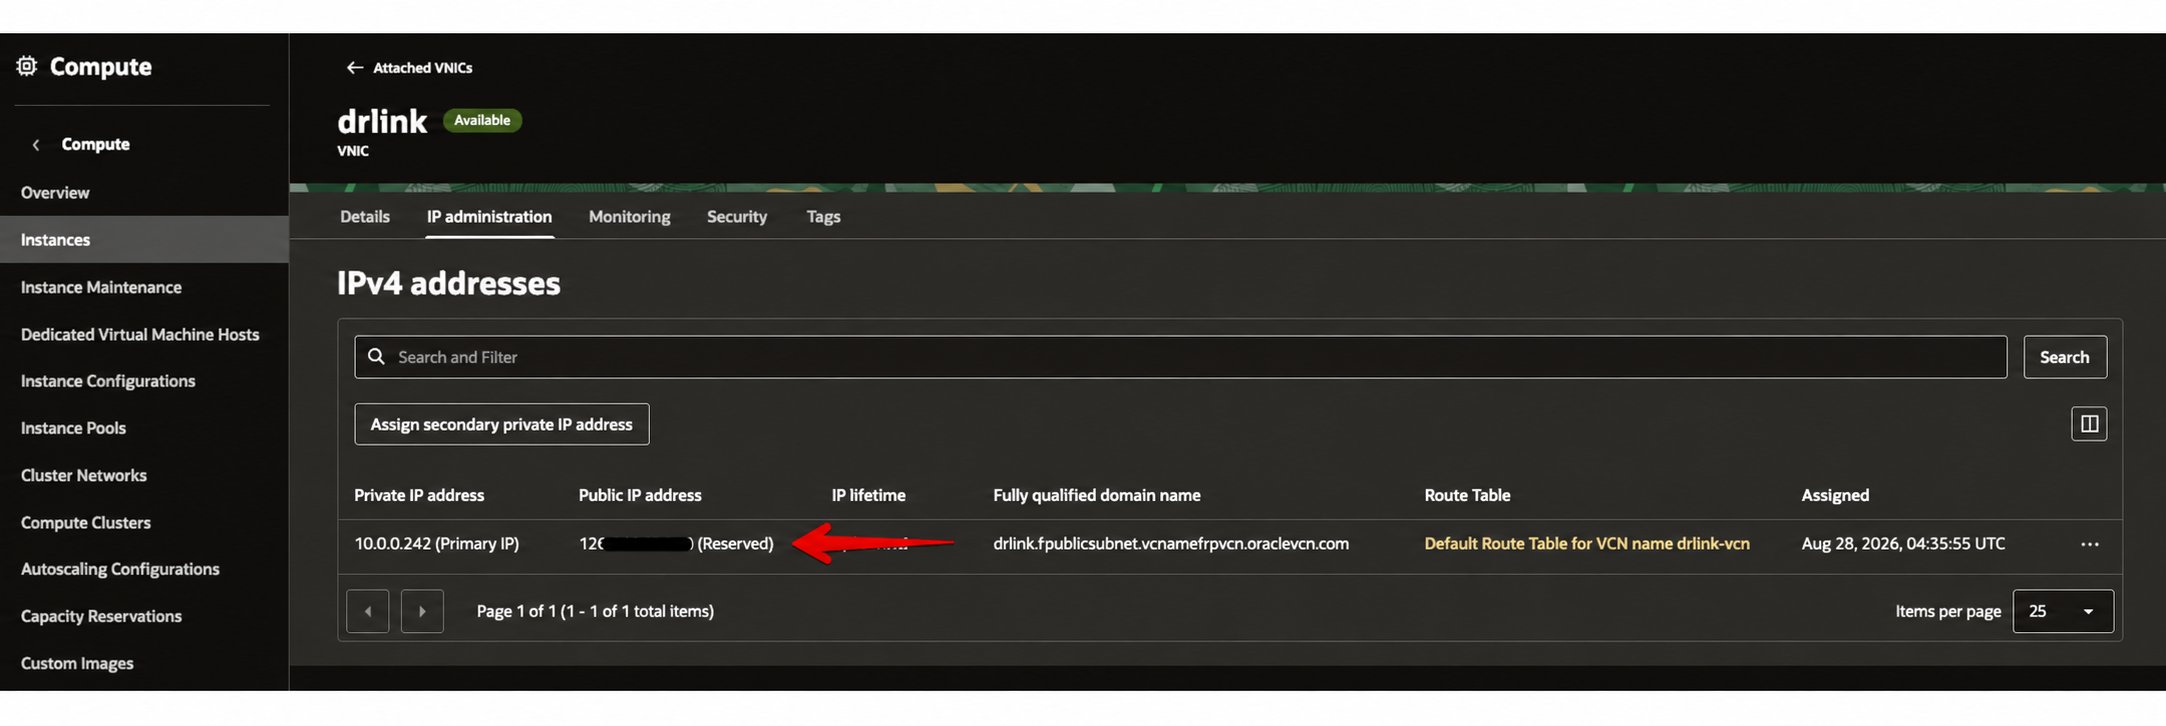
A Reserved Public IP is the address you should treat as the persistent public entry point for DataRelay Link. OCI performs the public/private mapping outside the Ubuntu guest, so `ip addr` on the VM normally shows the private `10.x.x.x` address rather than the public address.

Confirm that the Reserved Public IP is attached to the Primary Private IP. The public IP value in this screenshot has been masked before publication.
<img src="https://mintcdn.com/data-relay/GMgXaeifjTKi3w1Y/images/oci/31.png?fit=max&auto=format&n=GMgXaeifjTKi3w1Y&q=85&s=9caf9e95071e74a750af96c18287838b" alt="Picture 31. Confirm the Reserved Public IP is attached" width="2166" height="726" data-path="images/oci/31.png" />

<Note>
  Picture 32 (successful SSH session) from the original Word guide is still not published because it contains field connection details. The SSH procedure below uses the `<RESERVED-PUBLIC-IP>` placeholder instead.
</Note>

## 5. Test SSH access

For OCI Ubuntu images the default account is normally `ubuntu`:

```bash theme={null}
chmod 600 ~/Downloads/<private-key-file>
ssh -i ~/Downloads/<private-key-file> ubuntu@<RESERVED-PUBLIC-IP>
```

Then verify the host:

```bash theme={null}
uname -m
cat /etc/os-release
systemctl --version
```

Expected for this guide:

```text theme={null}
Architecture   x86_64
OS             Ubuntu 24.04 LTS
PID 1          systemd
```
