Roll out reviewed policy with a ConfigurationBundle
Outcome: A Server administrator creates narrowly scoped network/service objects and an Internet Access WHITELIST in one validated configuration transaction, without directly editing internal files.
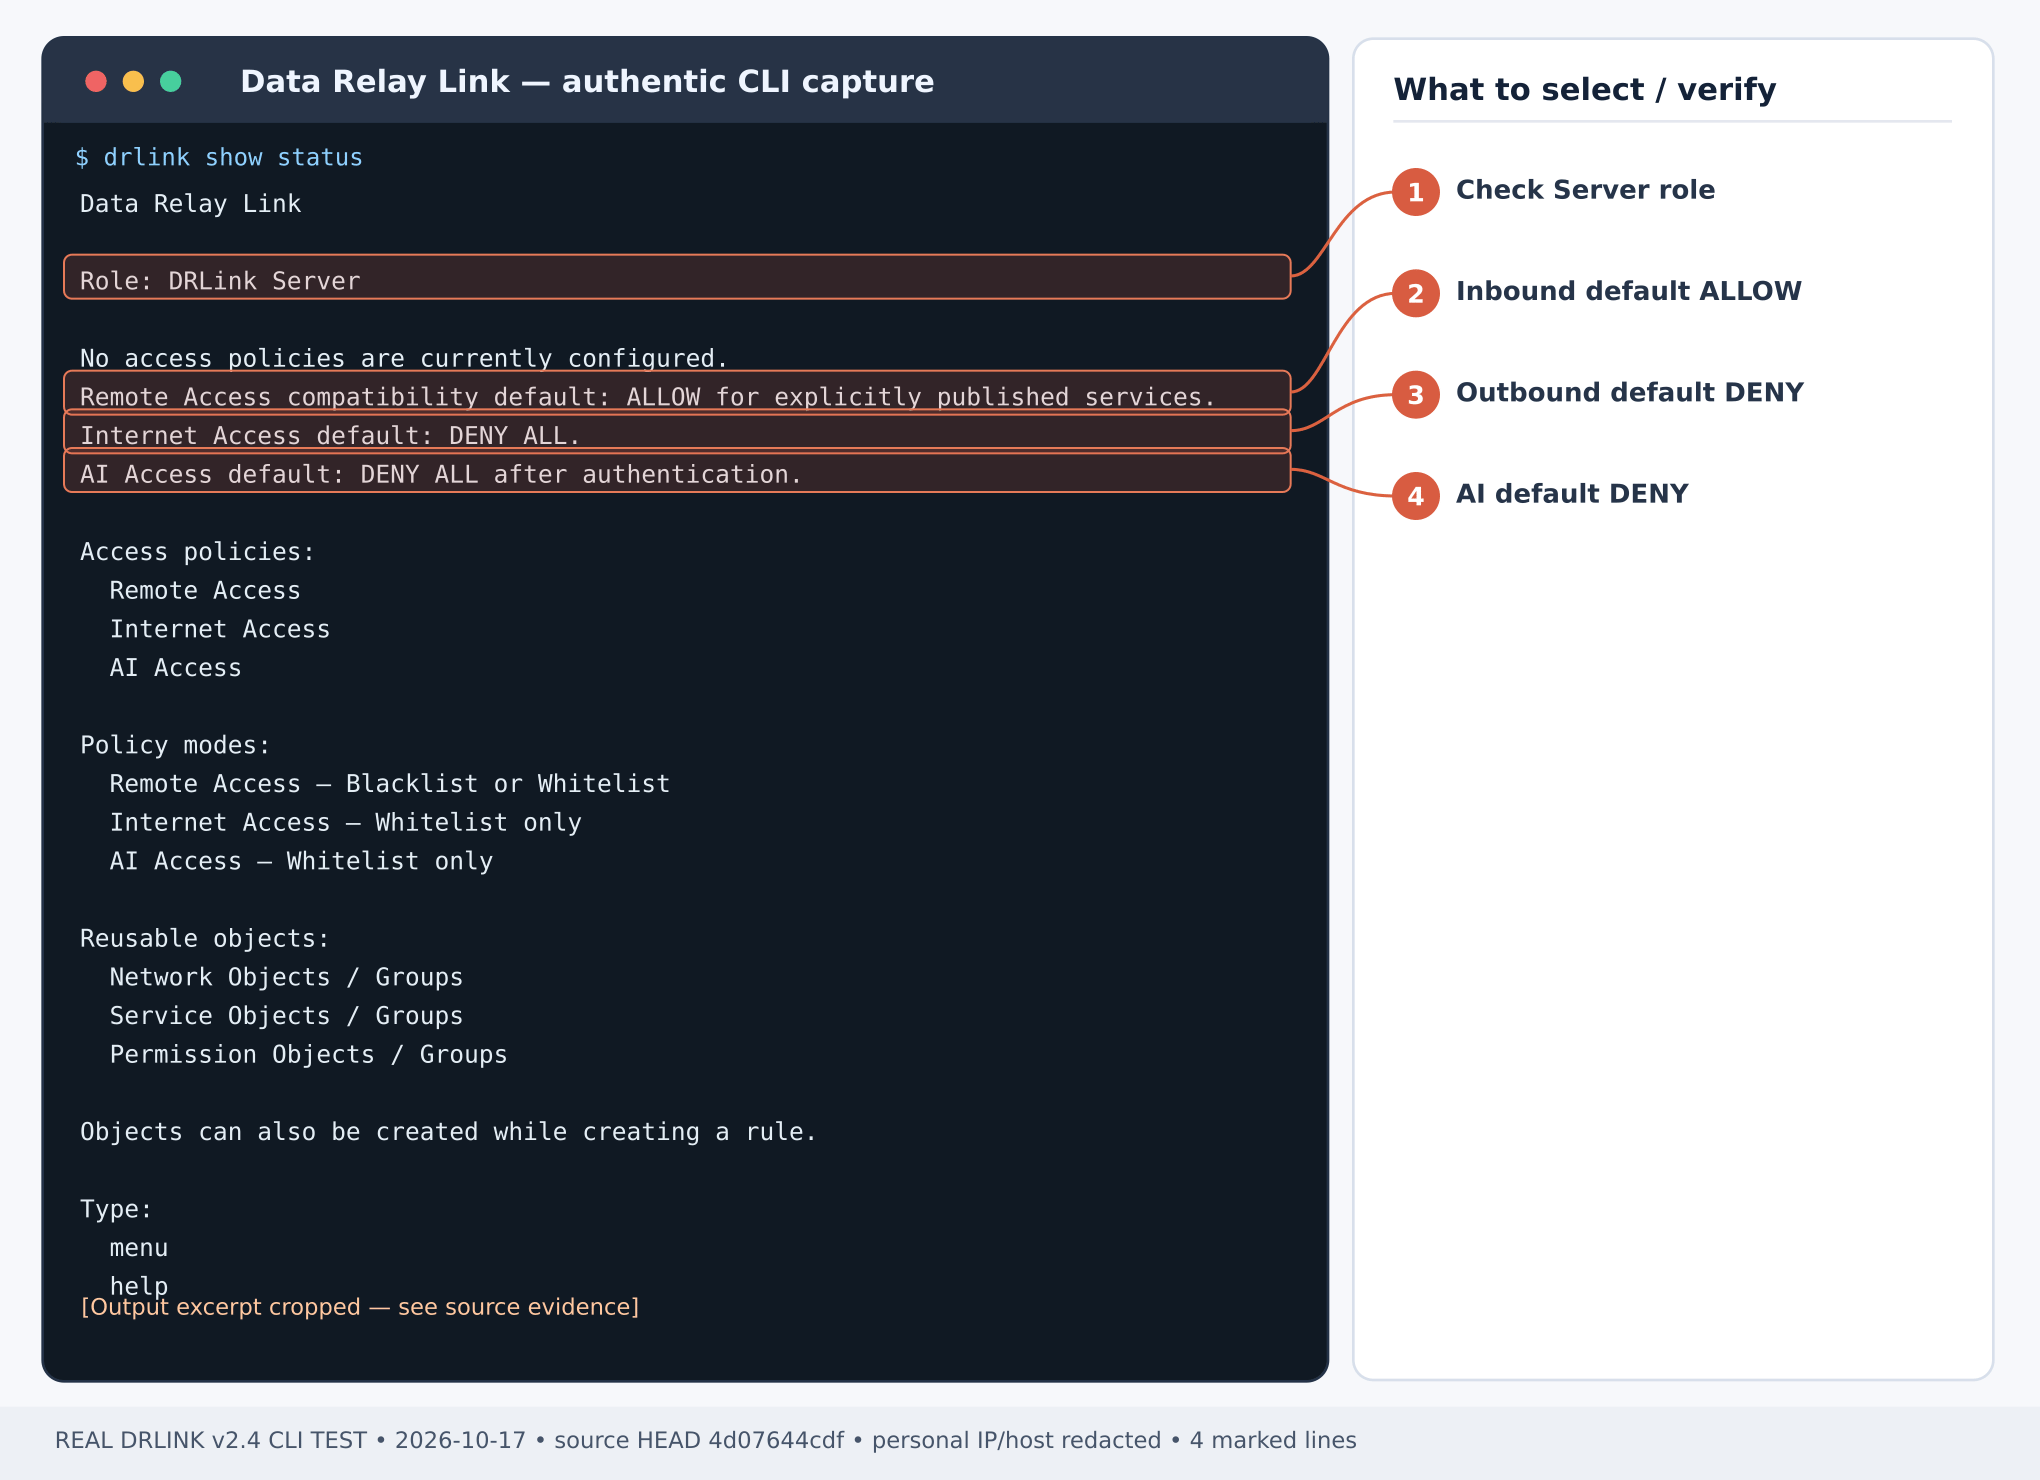
Figure 1. Real Server CLI status: verify Server role and the different initial ALLOW/DENY policy modes before editing a bundle. Pre-configuration test capture; sensitive details masked.Server shell:
sudo drlink system versionsudo drlink show statussudo drlink system revisionssudo drlink system export configuration /tmp/drlink-before.yaml
Keep the baseline privately, as exported config may include sensitive operational material. Do not commit the export to a public repository.
On the Server shell, create /tmp/drlink-allow-github.yaml with this content. Replace the example source IP with the real proxy-visible source:The YAML below illustrates the resource changes. First obtain configurationBundle.sourceRevision from a fresh system export configuration <FILE>, and copy that field and its exact value immediately below context: server in the file you will apply. Omitting it from a copied example does not bind apply to the revision you reviewed. Replace references such as ubuntu-prod with actual existing selectors.
This is the Server bundle schema. Do not add apiVersion/kind or Agent-only remoteServices here. Resources omitted from the bundle remain unchanged, but existing Internet Access rules also remain unless deliberately changed. Review them before applying.
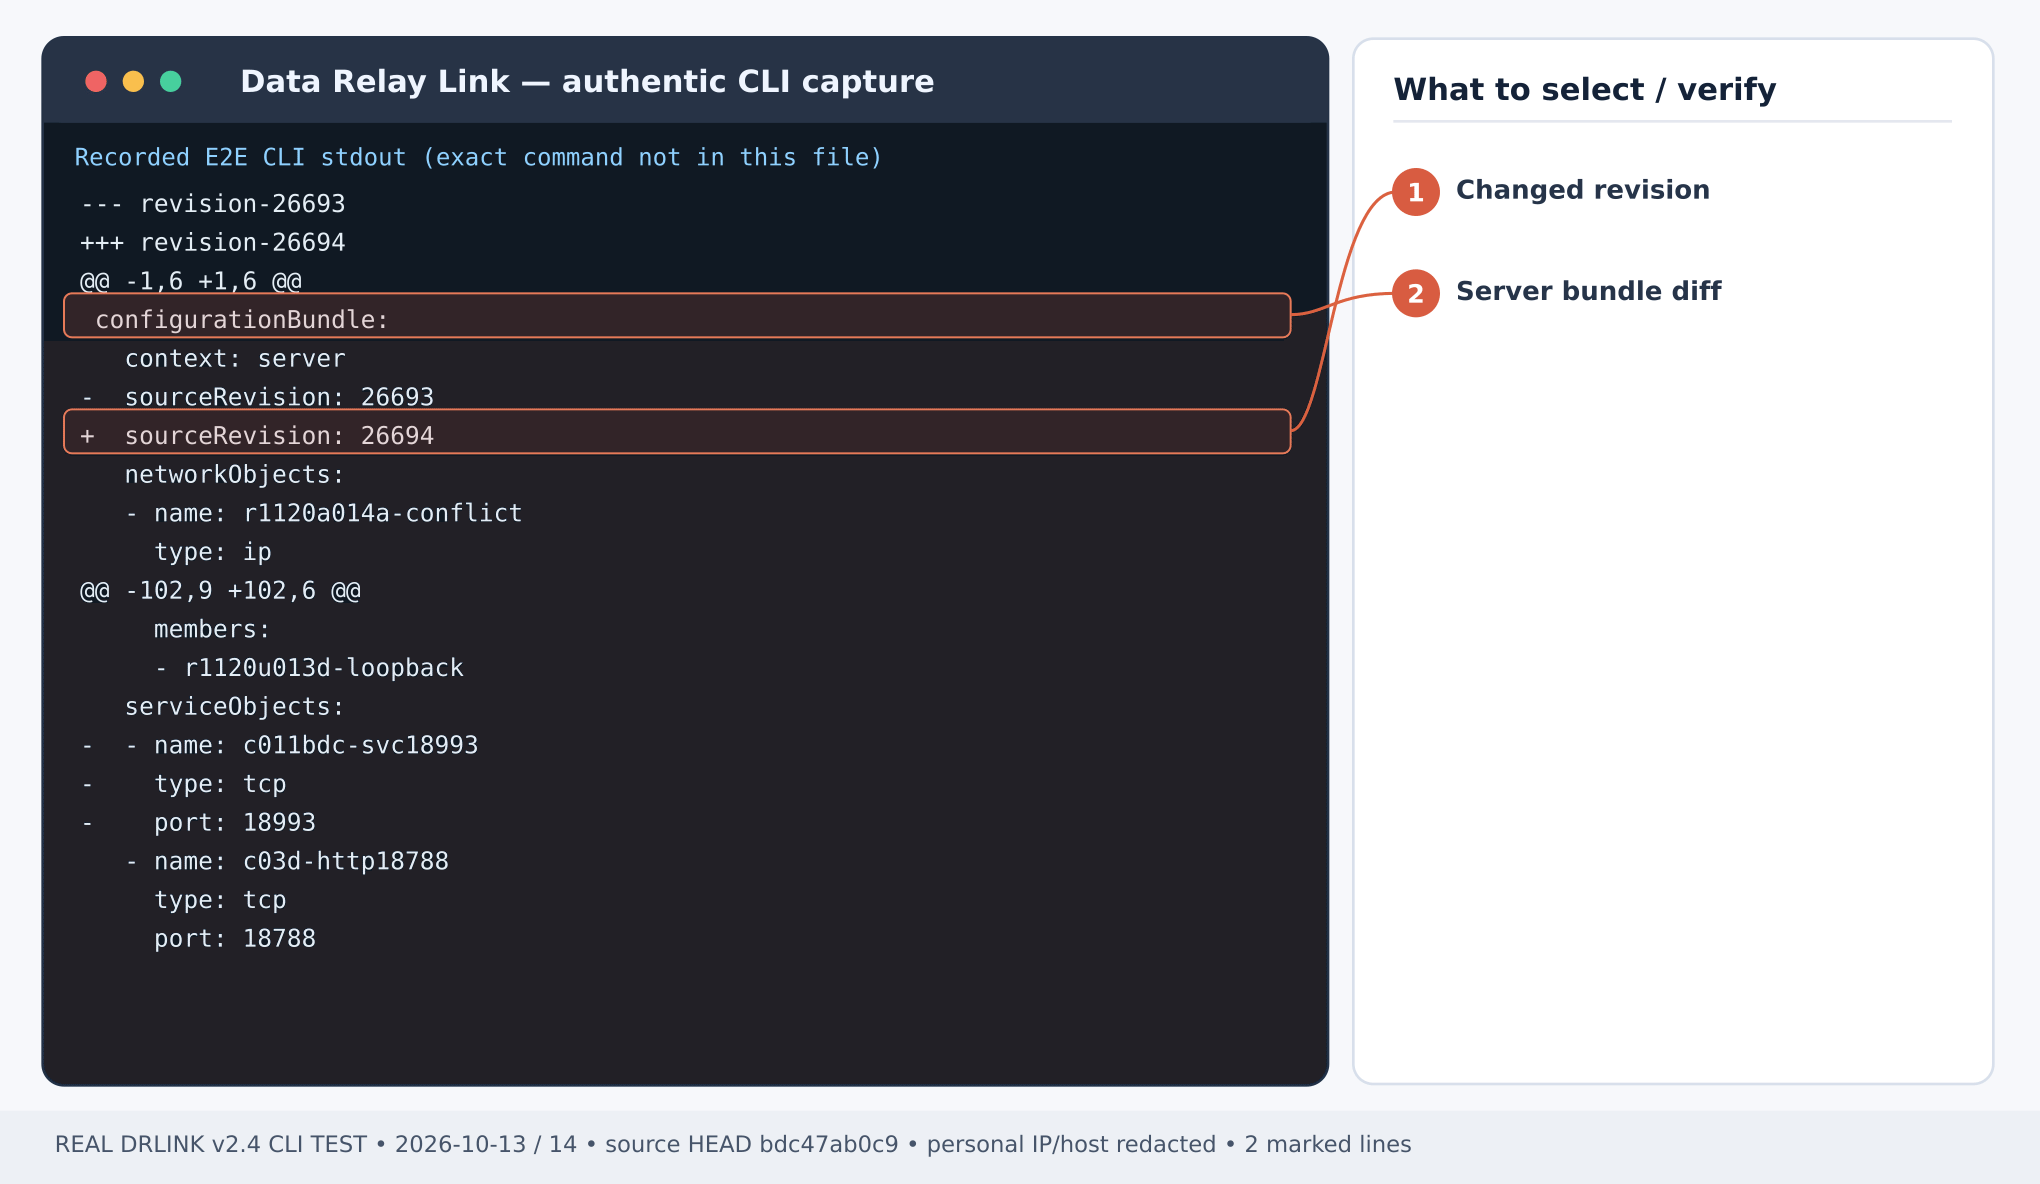
Figure 2. Real configuration revision diff: compare the changes and sourceRevision before applying a bundle. CLI output example; sensitive addresses and hostnames are masked.Server shell:
sudo drlink test configuration /tmp/drlink-allow-github.yamlsudo drlink system diff configuration /tmp/drlink-allow-github.yamlsudo drlink show internet-access
Expected: syntax/context valid, an understandable change diff and no unintended broadening. If the source revision has changed since the export, re-export and reconcile the new state. A valid test is not permission to apply a stale bundle.
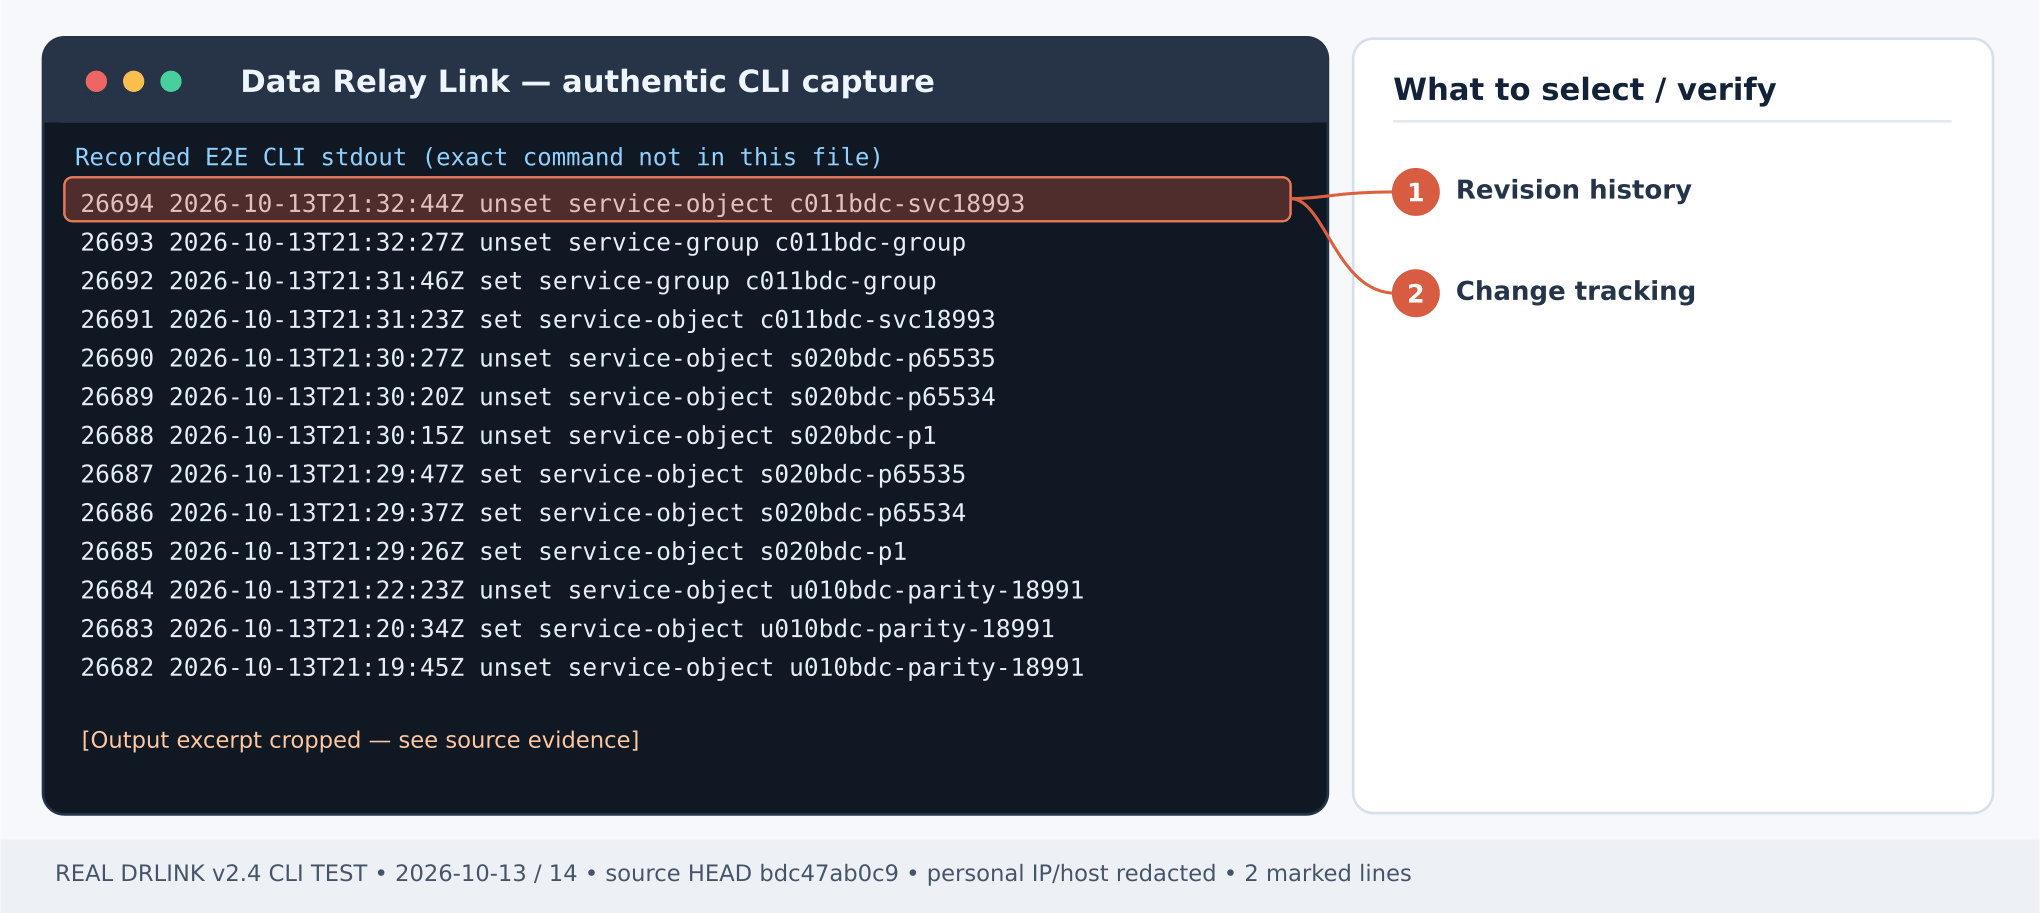
Figure 3. Real revision history: inspect previous set/unset operations and revision IDs before planned rollback. CLI output example; sensitive addresses and hostnames are masked.After inspecting the security-impact confirmation and having the necessary operator authorization:
sudo drlink system apply configuration /tmp/drlink-allow-github.yamlsudo drlink show internet-accesssudo drlink system revisions
Expected: the new objects/rule appear and are effective for new connections; the same bundle applied again should result in NO CHANGE when state and revision permit. A Server bundle is atomic within Server context, not a distributed Server+Agent transaction.
test internet-access source office-admin destination github service httpssystem audit
From the actually approved protected host, configure the standard HTTP(S) proxy and test a real HTTPS Git or curl request using the GitHub egress playbook. A policy ALLOW result alone is not traffic E2E.
If validation or apply rejects the bundle, no partial configuration change is expected; inspect the reported error rather than bypassing transaction guards. Compare the recorded revisions with system diff <REVISION_A> <REVISION_B> and plan a reviewed system rollback <REVISION> only if required. Avoid treating a blind rollback as risk-free: it can change current access. Keep exported files in protected storage and remove temporary copies after the approved work.
Carry sourceRevision from a fresh export into the reviewed change. A stale apply is rejected even if test/diff previously looked valid; re-export and reconcile before retrying. Same-state reapply can be NO CHANGE, but an old export is not a reusable force-overwrite mechanism.Current CLI inventory · MCP compatibility
Last modified on October 29, 2026
{"docsConfig":{"theme":"mint","$schema":"https://mintlify.com/docs.json","name":"DataRelay Link","description":"Lightweight secure connectivity for isolated and restricted networks with controlled remote access and agentless outbound egress.","colors":{"primary":"#C2410C","light":"#FB923C","dark":"#C75A00"},"logo":{"light":"https://mintcdn.com/data-relay/QdSvVfPZ7NEJSOWl/logo/light.svg?fit=max\u0026auto=format\u0026n=QdSvVfPZ7NEJSOWl\u0026q=85\u0026s=888463e35ab49f73f9b174030b3263d6","dark":"https://mintcdn.com/data-relay/QdSvVfPZ7NEJSOWl/logo/dark.svg?fit=max\u0026auto=format\u0026n=QdSvVfPZ7NEJSOWl\u0026q=85\u0026s=78944f5be2786c960ab6daaaf7ca870b","href":"https://link.datarelay.run"},"favicon":"https://mintcdn.com/data-relay/QdSvVfPZ7NEJSOWl/favicon.svg?fit=max\u0026auto=format\u0026n=QdSvVfPZ7NEJSOWl\u0026q=85\u0026s=d6f1dea7850d21b0c157e4be3317c226","appearance":{"default":"system","strict":false},"navbar":{"links":[{"href":"https://datarelay.run/","label":"DataRelay"},{"href":"https://link.datarelay.run/","label":"Link"},{"href":"https://control.datarelay.run/","label":"Control"},{"href":"https://grant.datarelay.run/","label":"Grant"},{"href":"https://engineering.datarelay.run/","label":"Engineering"},{"href":"https://github.com/datarelay-labs/datarelay-link","type":"github"}]},"search":{"prompt":"Search DataRelay Link docs..."},"seo":{"metatags":{"canonical":"https://link.datarelay.run"},"indexing":"navigable"},"metadata":{"timestamp":true},"styling":{"latex":false},"navigation":{"languages":[{"language":"en","href":""},{"language":"ko","href":"ko"}]}},"deployment":{"deploymentMetadataValue":{"subdomain":"data-relay","hasAudioNarration":false,"actualSubdomain":"data-relay","customDomains":["link.datarelay.run"],"gitSource":{"type":"github","owner":"datarelay-labs","repo":"datarelay-link-docs","deployBranch":"main","contentDirectory":"","isPrivate":false,"mountPath":"","label":""},"chroma":{"latestBuiltDeploymentHistoryId":"6ae2b51eefa5e7bcbb87bc8e","collectionId":"a1f69361-66ae-435c-96ea-5f84e3b497ae","liveDeploymentHistoryId":"6ae2b51eefa5e7bcbb87bc8e","schemaVersion":"v3"},"entitlements":{"AI_CHAT":{"status":"DISABLED"}},"buildId":"6ae2b51eefa5e7bcbb87bc8e","clientVersion":"0.0.4044","searchFilterCounts":[{"language":"en","tag":"Practical Use Cases","count":13},{"language":"ko","tag":"실습: 활용 사례","count":13},{"language":"en","tag":"Getting Started","count":11},{"language":"ko","tag":"시작하기","count":10},{"language":"en","tag":"Security \u0026 Reference","count":9},{"language":"ko","tag":"보안 \u0026 참고","count":8},{"language":"en","tag":"Operations","count":7},{"language":"ko","tag":"운영 \u0026 문제 해결","count":7},{"language":"en","tag":"Remote Services \u0026 Access","count":5},{"language":"ko","tag":"Remote Service \u0026 Access","count":5},{"language":"en","tag":"AI Access","count":4},{"language":"ko","tag":"AI Access","count":4},{"language":"en","tag":"Deployment","count":3},{"language":"en","tag":"CLI \u0026 Configuration","count":3},{"language":"en","tag":"Managed Hosts \u0026 Objects","count":3},{"language":"ko","tag":"배포","count":3},{"language":"ko","tag":"CLI \u0026 Configuration","count":3},{"language":"ko","tag":"Managed Host \u0026 Object","count":3},{"language":"en","tag":"Internet Access","count":1},{"language":"ko","tag":"Internet Access","count":1}]},"assistantConfig":{"enableAskAiButton":false,"enableStarterQuestions":false,"enableContextualStarterQuestions":false,"enableAskAiSearchBar":true},"basePath":"","hasChatPermissions":false,"hasWebMcpPermissions":false,"toggles":[{"name":"kill-isr","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"agent-mintlify-slack","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"agent-integrations-settings","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automations-pr-grouping","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"custom-prefix","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"analytics-v7","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"user-flows-analytics","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"no-publish-flow","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-onboarding","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"llms-txt-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"snapshot-serving-live","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"stripTemperatureMiddleware","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"support-platform-pylon-zendesk","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"snapshot-serving","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"instant-rollback","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"granular-notifications-server","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"granular-notifications","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automations-fable","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"fixed-ai-action-pricing","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automation-resolve-merge-conflict","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"scoped-publishing","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"mintql","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"page-level-analytics","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"editor-version-history-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"billing-page-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"full-page-search","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workspace-projects","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"assistant-v5","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"byok-sep-25","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"fork-pr-previews","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"revalidation-jwt","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"vite-origin","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"billing-updated-9-15","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-sso-scim","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"hobby-abuse-scan","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"dashboard-inbox","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-signup","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"turbopuffer-dual-write","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-enabled","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"approve-review-flow","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"sso-setup-deadline-banner","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false}],"googleFontsInlined":false},"customCss":[{"filePath":"style.css","content":":root{--dr-brand:#C2410C;--dr-brand-hover:#9A3412;--dr-brand-soft:#FFF7ED;--dr-product-accent:#0369A1;--dr-bg:#FFFFFF;--dr-surface:#FFFFFF;--dr-surface-subtle:#FAFAF9;--dr-ink:#1C1917;--dr-muted:#57534E;--dr-border:#E7E5E4;--dr-border-strong:#D6D3D1;--dr-shadow-sm:0 1px 2px rgb(28 25 23 / 0.05);--dr-shadow-md:0 14px 34px rgb(28 25 23 / 0.09);--dr-radius-sm:10px;--dr-radius-md:16px;--dr-radius-lg:24px}.dark{--dr-brand:#FB923C;--dr-brand-hover:#FDBA74;--dr-brand-soft:#2A160D;--dr-product-accent:#38BDF8;--dr-bg:#0C0A09;--dr-surface:#141210;--dr-surface-subtle:#1C1917;--dr-ink:#FAFAF9;--dr-muted:#C7C2BC;--dr-border:#292524;--dr-border-strong:#44403C;--dr-shadow-sm:0 1px 2px rgb(0 0 0 / 0.25);--dr-shadow-md:0 18px 42px rgb(0 0 0 / 0.32)}html{scroll-behavior:smooth}body{text-rendering:optimizeLegibility;-webkit-font-smoothing:antialiased}#navbar-transition{background:rgb(255 255 255/.9)!important;border-color:rgb(120 113 108/.16)!important;backdrop-filter:blur(16px) saturate(150%);-webkit-backdrop-filter:blur(16px) saturate(150%)}.dark #navbar-transition{background:rgb(12 10 9/.88)!important;border-color:rgb(231 229 228/.1)!important}.nav-logo{height:2rem!important}body,main h1,main h2{color:var(--dr-ink)}main h1{letter-spacing:-.038em;font-weight:760;line-height:1.08}main h2{letter-spacing:-.025em;font-weight:700}main h3{letter-spacing:-.015em}main li,main p{line-height:1.72}main blockquote{border-left:3px solid var(--dr-product-accent)!important;background:var(--dr-surface-subtle);border-radius:0 var(--dr-radius-sm) var(--dr-radius-sm) 0;padding:.8rem 1rem}main pre{border:1px solid var(--dr-border)!important;border-radius:var(--dr-radius-md)!important;box-shadow:var(--dr-shadow-sm)}main table{border-color:var(--dr-border)!important;border-radius:var(--dr-radius-sm)}.dr-hero-kicker{display:inline-flex;align-items:center;gap:.5rem;margin:0 0 1rem;padding:.42rem .7rem;border:1px solid #fed7aa;border-radius:999px;background:#fff7ed;color:#9a3412;font-size:.72rem;font-weight:760;letter-spacing:.12em;text-transform:uppercase}.dark .dr-hero-kicker{border-color:#7c2d12;background:#2a160d;color:#fdba74}.dr-hero-kicker+h1{max-width:950px;margin-top:0!important;font-size:clamp(2.7rem,6vw,4.85rem)!important;line-height:.98!important;letter-spacing:-.055em!important}.dr-hero-actions{display:flex;flex-wrap:wrap;gap:.7rem;margin:1.55rem 0 1.35rem}.dr-button{display:inline-flex;min-height:2.75rem;align-items:center;justify-content:center;border-radius:.72rem;padding:.68rem 1rem;border:1px solid transparent;font-size:.9rem;font-weight:680;line-height:1;text-decoration:none!important;transition:transform 150ms ease,border-color 150ms ease,background-color 150ms ease,box-shadow 150ms ease}.dr-button:hover{transform:translateY(-1px)}.dr-button-primary{background:var(--dr-brand);color:#fff!important;box-shadow:0 6px 18px rgb(194 65 12/.2)}.dr-button-primary:hover{background:var(--dr-brand-hover)}.dark .dr-button-primary{color:#1c1917!important}.dr-button-secondary{background:var(--dr-surface);color:var(--dr-ink)!important;border-color:var(--dr-border-strong);box-shadow:var(--dr-shadow-sm)}.dr-button-secondary:hover{border-color:var(--dr-product-accent)}.dr-family-strip{display:flex;align-items:center;gap:.35rem;margin:0 0 2rem;padding:.4rem;width:fit-content;max-width:100%;overflow-x:auto;border:1px solid var(--dr-border);border-radius:.85rem;background:var(--dr-surface-subtle);scrollbar-width:none}.dr-family-strip::-webkit-scrollbar{display:none}.dr-family-strip .dr-family-current,.dr-family-strip a{display:inline-flex;align-items:center;min-height:2rem;padding:.42rem .68rem;border-radius:.56rem;white-space:nowrap;color:var(--dr-muted)!important;font-size:.78rem;font-weight:650;text-decoration:none!important}.dr-family-strip a:hover{color:var(--dr-ink)!important;background:var(--dr-surface)}.dr-family-strip .dr-family-current{color:#fff!important;background:var(--dr-product-accent);box-shadow:var(--dr-shadow-sm)}.dark .dr-family-strip .dr-family-current{color:#0c0a09!important}.card{border-color:var(--dr-border)!important;border-radius:var(--dr-radius-md)!important;background:var(--dr-surface)!important;box-shadow:var(--dr-shadow-sm);transition:transform 160ms ease,box-shadow 160ms ease,border-color 160ms ease!important}.card:hover{transform:translateY(-2px);border-color:var(--dr-product-accent)!important;box-shadow:var(--dr-shadow-md)}[data-component-part=card-title]{letter-spacing:-.012em}[data-component-part=card-icon]{color:var(--dr-product-accent)!important}.callout{border-radius:var(--dr-radius-md)!important}footer{border-top-color:var(--dr-border)!important}:where(a, button, input, select, textarea):focus-visible{outline:3px solid var(--dr-product-accent)!important;outline-offset:3px!important}@media (max-width:768px){.dr-hero-kicker+h1{font-size:clamp(2.35rem,13vw,3.55rem)!important}.dr-hero-actions{display:grid;grid-template-columns:1fr}.dr-button,.dr-family-strip{width:100%}}@media (prefers-reduced-motion:reduce){html{scroll-behavior:auto}.card,.dr-button{transition:none!important}.card:hover,.dr-button:hover{transform:none}}"}],"page":{"pagePath":"use-cases/configuration-bundle","slug":"/use-cases/configuration-bundle","pageMetadata":{"title":"Use case: ConfigurationBundle safely","description":"Validate, diff, apply and export a reviewed v2.4 Server configuration change.","href":"/use-cases/configuration-bundle"},"description":{"compiledSource":"\"use strict\";\nconst {jsx: _jsx} = arguments[0];\nconst {useMDXComponents: _provideComponents} = arguments[0];\nfunction _createMdxContent(props) {\n const _components = {\n p: \"p\",\n ..._provideComponents(),\n ...props.components\n };\n return _jsx(_components.p, {\n children: \"Validate, diff, apply and export a reviewed v2.4 Server configuration change.\"\n });\n}\nfunction MDXContent(props = {}) {\n const {wrapper: MDXLayout} = {\n ..._provideComponents(),\n ...props.components\n };\n return MDXLayout ? _jsx(MDXLayout, {\n ...props,\n children: _jsx(_createMdxContent, {\n ...props\n })\n }) : _createMdxContent(props);\n}\nreturn {\n default: MDXContent\n};\n","frontmatter":{},"scope":{}},"pageType":"default","mdx":{"mdxSource":{"compiledSource":"\"use strict\";const{Fragment:_Fragment,jsx:_jsx,jsxs:_jsxs}=arguments[0];const{useMDXComponents:_provideComponents}=arguments[0];function _createMdxContent(props){const _components={a:`a`,code:`code`,em:`em`,p:`p`,pre:`pre`,span:`span`,strong:`strong`,..._provideComponents(),...props.components},{CodeBlock,Heading,OptimizedImage}=_components;if(!CodeBlock)_missingMdxReference(`CodeBlock`,true);if(!Heading)_missingMdxReference(`Heading`,true);if(!OptimizedImage)_missingMdxReference(`OptimizedImage`,true);return _jsxs(_Fragment,{children:[_jsx(Heading,{level:`1`,id:`roll-out-reviewed-policy-with-a-configurationbundle`,children:`Roll out reviewed policy with a ConfigurationBundle`}),`\n`,_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Outcome:`}),` A Server administrator creates narrowly scoped network/service objects and an Internet Access WHITELIST in one validated configuration transaction, without directly editing internal files.`]}),`\n`,_jsx(Heading,{level:`2`,id:`step-1-—-confirm-server-role-and-baseline`,children:`Step 1 — confirm Server role and baseline`}),`\n`,_jsx(OptimizedImage,{src:`https://mintcdn.com/data-relay/RzAl7zFhuZCRSIKj/images/cli-captures/server-status.png?fit=max\u0026auto=format\u0026n=RzAl7zFhuZCRSIKj\u0026q=85\u0026s=bfe6b188996c8ea2078dfe6c01145c28`,alt:`Actual DRLink Server CLI status — verify Server role and plane-specific initial access behavior`,\"data-og-width\":`2040`,width:`2040`,\"data-og-height\":`1480`,height:`1480`,\"data-path\":`images/cli-captures/server-status.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/data-relay/RzAl7zFhuZCRSIKj/images/cli-captures/server-status.png?w=280\u0026fit=max\u0026auto=format\u0026n=RzAl7zFhuZCRSIKj\u0026q=85\u0026s=20267251278d32518f19bf9225c2faa5 280w, https://mintcdn.com/data-relay/RzAl7zFhuZCRSIKj/images/cli-captures/server-status.png?w=560\u0026fit=max\u0026auto=format\u0026n=RzAl7zFhuZCRSIKj\u0026q=85\u0026s=86dd2e3c892129b3cc69eec8f1a5cae0 560w, https://mintcdn.com/data-relay/RzAl7zFhuZCRSIKj/images/cli-captures/server-status.png?w=840\u0026fit=max\u0026auto=format\u0026n=RzAl7zFhuZCRSIKj\u0026q=85\u0026s=b66e88f3c4bda6694d8293b9f76a7208 840w, https://mintcdn.com/data-relay/RzAl7zFhuZCRSIKj/images/cli-captures/server-status.png?w=1100\u0026fit=max\u0026auto=format\u0026n=RzAl7zFhuZCRSIKj\u0026q=85\u0026s=82e4cfc06673eadd6058ad50f162be14 1100w, https://mintcdn.com/data-relay/RzAl7zFhuZCRSIKj/images/cli-captures/server-status.png?w=1650\u0026fit=max\u0026auto=format\u0026n=RzAl7zFhuZCRSIKj\u0026q=85\u0026s=ecff66162e0c94a05dd15d7df44fa7ce 1650w, https://mintcdn.com/data-relay/RzAl7zFhuZCRSIKj/images/cli-captures/server-status.png?w=2500\u0026fit=max\u0026auto=format\u0026n=RzAl7zFhuZCRSIKj\u0026q=85\u0026s=e84b59995fdcc64a0204e45acf40b7d9 2500w`}),`\n`,_jsx(_components.p,{children:_jsx(_components.em,{children:`Figure 1. Real Server CLI status: verify Server role and the different initial ALLOW/DENY policy modes before editing a bundle. Pre-configuration test capture; sensitive details masked.`})}),`\n`,_jsx(_components.p,{children:_jsx(_components.strong,{children:`Server shell:`})}),`\n`,_jsx(CodeBlock,{filename:``,numberOfLines:`4`,language:`shellscript`,children:_jsx(_components.pre,{className:`shiki shiki-themes github-light-default dark-plus`,style:{backgroundColor:`#ffffff`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#1f2328`,\"--shiki-dark\":`#D4D4D4`},language:`shellscript`,children:_jsxs(_components.code,{language:`shellscript`,numberOfLines:`4`,children:[_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#DCDCAA`},children:`sudo`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` drlink`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` system`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` version`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#DCDCAA`},children:`sudo`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` drlink`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` show`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` status`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#DCDCAA`},children:`sudo`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` drlink`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` system`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` revisions`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#DCDCAA`},children:`sudo`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` drlink`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` system`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` export`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` configuration`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` /tmp/drlink-before.yaml`})]}),`\n`]})})}),`\n`,_jsx(_components.p,{children:`Keep the baseline privately, as exported config may include sensitive operational material. Do not commit the export to a public repository.`}),`\n`,_jsx(Heading,{level:`2`,id:`step-2-—-write-a-complete-desired-change-bundle`,children:`Step 2 — write a complete desired-change bundle`}),`\n`,_jsxs(_components.p,{children:[`On the `,_jsx(_components.strong,{children:`Server shell`}),`, create `,_jsx(_components.strong,{children:`/tmp/drlink-allow-github.yaml`}),` with this content. Replace the example source IP with the real `,_jsx(_components.strong,{children:`proxy-visible`}),` source:`]}),`\n`,_jsxs(_components.p,{children:[`The YAML below illustrates the resource changes. First obtain `,_jsx(_components.code,{children:`configurationBundle.sourceRevision`}),` from a fresh `,_jsx(_components.code,{children:`system export configuration \u003cFILE>`}),`, and copy `,_jsx(_components.strong,{children:`that field and its exact value`}),` immediately below `,_jsx(_components.code,{children:`context: server`}),` in the file you will apply. Omitting it from a copied example does not bind apply to the revision you reviewed. Replace references such as `,_jsx(_components.code,{children:`ubuntu-prod`}),` with actual existing selectors.`]}),`\n`,_jsx(CodeBlock,{filename:``,numberOfLines:`22`,language:`yaml`,children:_jsx(_components.pre,{className:`shiki shiki-themes github-light-default dark-plus`,style:{backgroundColor:`#ffffff`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#1f2328`,\"--shiki-dark\":`#D4D4D4`},language:`yaml`,children:_jsxs(_components.code,{language:`yaml`,numberOfLines:`22`,children:[_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:`configurationBundle`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`:`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:` context`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`server`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:` networkObjects`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`:`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:` - `}),_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:`name`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`office-admin`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:` type`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`ip`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:` value`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#B5CEA8`},children:`203.0.113.10`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:` - `}),_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:`name`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`github`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:` type`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`fqdn`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:` value`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`github.com`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:` serviceObjects`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`:`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:` - `}),_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:`name`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`https`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:` type`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`tcp`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:` port`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#B5CEA8`},children:`443`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:` internetAccess`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`:`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:` mode`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`whitelist`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:` enforcement`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`enabled`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:` rules`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`:`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:` - `}),_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:`name`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`github-https`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:` source`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`office-admin`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:` destination`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`github`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:` service`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`https`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#116329`,\"--shiki-dark\":`#569CD6`},children:` enabled`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`: `}),_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#569CD6`},children:`true`})]}),`\n`]})})}),`\n`,_jsxs(_components.p,{children:[`This is the `,_jsx(_components.strong,{children:`Server`}),` bundle schema. Do not add `,_jsx(_components.strong,{children:`apiVersion`}),`/`,_jsx(_components.strong,{children:`kind`}),` or Agent-only `,_jsx(_components.strong,{children:`remoteServices`}),` here. Resources omitted from the bundle remain unchanged, but existing Internet Access rules also remain unless deliberately changed. Review them before applying.`]}),`\n`,_jsx(Heading,{level:`2`,id:`step-3-—-validate-and-compare-before-mutation`,children:`Step 3 — validate and compare before mutation`}),`\n`,_jsx(OptimizedImage,{src:`https://mintcdn.com/data-relay/RzAl7zFhuZCRSIKj/images/cli-captures/config-revision-diff.png?fit=max\u0026auto=format\u0026n=RzAl7zFhuZCRSIKj\u0026q=85\u0026s=092795979a6378b6e0eb5ae45b61f9e6`,alt:`Real Data Relay Link CLI capture — Real configuration revision diff: compare the changes and sourceRevision before applying a bundle.`,\"data-og-width\":`2040`,width:`2040`,\"data-og-height\":`1184`,height:`1184`,\"data-path\":`images/cli-captures/config-revision-diff.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/data-relay/RzAl7zFhuZCRSIKj/images/cli-captures/config-revision-diff.png?w=280\u0026fit=max\u0026auto=format\u0026n=RzAl7zFhuZCRSIKj\u0026q=85\u0026s=7b2644367b84c43c326780baf2591dfa 280w, https://mintcdn.com/data-relay/RzAl7zFhuZCRSIKj/images/cli-captures/config-revision-diff.png?w=560\u0026fit=max\u0026auto=format\u0026n=RzAl7zFhuZCRSIKj\u0026q=85\u0026s=8e005b8d303f2c0f2a9c062eb9870994 560w, https://mintcdn.com/data-relay/RzAl7zFhuZCRSIKj/images/cli-captures/config-revision-diff.png?w=840\u0026fit=max\u0026auto=format\u0026n=RzAl7zFhuZCRSIKj\u0026q=85\u0026s=ef6db58d328b30acb5b0611c922beaf5 840w, https://mintcdn.com/data-relay/RzAl7zFhuZCRSIKj/images/cli-captures/config-revision-diff.png?w=1100\u0026fit=max\u0026auto=format\u0026n=RzAl7zFhuZCRSIKj\u0026q=85\u0026s=796f04a44b0b96504ef91b1dbc6deb4a 1100w, https://mintcdn.com/data-relay/RzAl7zFhuZCRSIKj/images/cli-captures/config-revision-diff.png?w=1650\u0026fit=max\u0026auto=format\u0026n=RzAl7zFhuZCRSIKj\u0026q=85\u0026s=1ec68eb817f25aada42c1499a93a9d50 1650w, https://mintcdn.com/data-relay/RzAl7zFhuZCRSIKj/images/cli-captures/config-revision-diff.png?w=2500\u0026fit=max\u0026auto=format\u0026n=RzAl7zFhuZCRSIKj\u0026q=85\u0026s=bfec0770888ca8c970b62341c339cd3b 2500w`}),`\n`,_jsx(_components.p,{children:_jsx(_components.em,{children:`Figure 2. Real configuration revision diff: compare the changes and sourceRevision before applying a bundle. CLI output example; sensitive addresses and hostnames are masked.`})}),`\n`,_jsx(_components.p,{children:_jsx(_components.strong,{children:`Server shell:`})}),`\n`,_jsx(CodeBlock,{filename:``,numberOfLines:`3`,language:`shellscript`,children:_jsx(_components.pre,{className:`shiki shiki-themes github-light-default dark-plus`,style:{backgroundColor:`#ffffff`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#1f2328`,\"--shiki-dark\":`#D4D4D4`},language:`shellscript`,children:_jsxs(_components.code,{language:`shellscript`,numberOfLines:`3`,children:[_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#DCDCAA`},children:`sudo`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` drlink`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` test`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` configuration`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` /tmp/drlink-allow-github.yaml`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#DCDCAA`},children:`sudo`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` drlink`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` system`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` diff`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` configuration`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` /tmp/drlink-allow-github.yaml`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#DCDCAA`},children:`sudo`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` drlink`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` show`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` internet-access`})]}),`\n`]})})}),`\n`,_jsxs(_components.p,{children:[`Expected: syntax/context valid, an understandable change diff and no unintended broadening. If the source revision has changed since the export, `,_jsx(_components.strong,{children:`re-export`}),` and reconcile the new state. A valid test is not permission to apply a stale bundle.`]}),`\n`,_jsx(Heading,{level:`2`,id:`step-4-—-apply-the-reviewed-change`,children:`Step 4 — apply the reviewed change`}),`\n`,_jsx(OptimizedImage,{src:`https://mintcdn.com/data-relay/RzAl7zFhuZCRSIKj/images/cli-captures/configuration-revisions.png?fit=max\u0026auto=format\u0026n=RzAl7zFhuZCRSIKj\u0026q=85\u0026s=7297d568222a96916265ebea13b96e5e`,alt:`Real Data Relay Link CLI capture — Real revision history: inspect previous set/unset operations and revision IDs before planned rollback.`,\"data-og-width\":`2040`,width:`2040`,\"data-og-height\":`913`,height:`913`,\"data-path\":`images/cli-captures/configuration-revisions.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/data-relay/RzAl7zFhuZCRSIKj/images/cli-captures/configuration-revisions.png?w=280\u0026fit=max\u0026auto=format\u0026n=RzAl7zFhuZCRSIKj\u0026q=85\u0026s=5389ce98843d318cb6a1eea0b7231455 280w, https://mintcdn.com/data-relay/RzAl7zFhuZCRSIKj/images/cli-captures/configuration-revisions.png?w=560\u0026fit=max\u0026auto=format\u0026n=RzAl7zFhuZCRSIKj\u0026q=85\u0026s=d6c9dd8ee1b7be1e68b9f49e73df0ad2 560w, https://mintcdn.com/data-relay/RzAl7zFhuZCRSIKj/images/cli-captures/configuration-revisions.png?w=840\u0026fit=max\u0026auto=format\u0026n=RzAl7zFhuZCRSIKj\u0026q=85\u0026s=79d4c78d1c0a33bd8e9072740ba9393a 840w, https://mintcdn.com/data-relay/RzAl7zFhuZCRSIKj/images/cli-captures/configuration-revisions.png?w=1100\u0026fit=max\u0026auto=format\u0026n=RzAl7zFhuZCRSIKj\u0026q=85\u0026s=139a07e3fb3790f82ed6a5d245ef3e8f 1100w, https://mintcdn.com/data-relay/RzAl7zFhuZCRSIKj/images/cli-captures/configuration-revisions.png?w=1650\u0026fit=max\u0026auto=format\u0026n=RzAl7zFhuZCRSIKj\u0026q=85\u0026s=b381ec7aedd8954f3b0b1b588f9ae7c1 1650w, https://mintcdn.com/data-relay/RzAl7zFhuZCRSIKj/images/cli-captures/configuration-revisions.png?w=2500\u0026fit=max\u0026auto=format\u0026n=RzAl7zFhuZCRSIKj\u0026q=85\u0026s=d3c7ea8d96e0e5ba35a8cf35b4251f09 2500w`}),`\n`,_jsx(_components.p,{children:_jsx(_components.em,{children:`Figure 3. Real revision history: inspect previous set/unset operations and revision IDs before planned rollback. CLI output example; sensitive addresses and hostnames are masked.`})}),`\n`,_jsx(_components.p,{children:`After inspecting the security-impact confirmation and having the necessary operator authorization:`}),`\n`,_jsx(CodeBlock,{filename:``,numberOfLines:`3`,language:`shellscript`,children:_jsx(_components.pre,{className:`shiki shiki-themes github-light-default dark-plus`,style:{backgroundColor:`#ffffff`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#1f2328`,\"--shiki-dark\":`#D4D4D4`},language:`shellscript`,children:_jsxs(_components.code,{language:`shellscript`,numberOfLines:`3`,children:[_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#DCDCAA`},children:`sudo`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` drlink`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` system`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` apply`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` configuration`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` /tmp/drlink-allow-github.yaml`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#DCDCAA`},children:`sudo`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` drlink`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` show`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` internet-access`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#DCDCAA`},children:`sudo`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` drlink`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` system`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` revisions`})]}),`\n`]})})}),`\n`,_jsxs(_components.p,{children:[`Expected: the new objects/rule appear and are effective for new connections; the same bundle applied again should result in `,_jsx(_components.strong,{children:`NO CHANGE`}),` when state and revision permit. A Server bundle is atomic within `,_jsx(_components.strong,{children:`Server`}),` context, not a distributed Server+Agent transaction.`]}),`\n`,_jsx(Heading,{level:`2`,id:`step-5-—-prove-policy-plus-traffic`,children:`Step 5 — prove policy plus traffic`}),`\n`,_jsx(_components.p,{children:_jsx(_components.strong,{children:`Server REPL:`})}),`\n`,_jsx(CodeBlock,{filename:``,numberOfLines:`3`,language:`text`,children:_jsx(_components.pre,{className:`shiki shiki-themes github-light-default dark-plus`,style:{backgroundColor:`#ffffff`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#1f2328`,\"--shiki-dark\":`#D4D4D4`},language:`text`,children:_jsxs(_components.code,{language:`text`,numberOfLines:`3`,children:[_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{children:`test internet-access source office-admin destination github service https`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{children:`system audit`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{})})]})})}),`\n`,_jsxs(_components.p,{children:[`From the actually approved protected host, configure the standard HTTP(S) proxy and test a real HTTPS Git or curl request using the `,_jsx(_components.a,{href:`/use-cases/github-egress`,children:`GitHub egress playbook`}),`. A policy ALLOW result alone is not traffic E2E.`]}),`\n`,_jsx(Heading,{level:`2`,id:`recovery-and-cleanup`,children:`Recovery and cleanup`}),`\n`,_jsxs(_components.p,{children:[`If validation or apply rejects the bundle, `,_jsx(_components.strong,{children:`no partial configuration change`}),` is expected; inspect the reported error rather than bypassing transaction guards. Compare the recorded revisions with `,_jsx(_components.code,{children:`system diff \u003cREVISION_A> \u003cREVISION_B>`}),` and plan a reviewed `,_jsx(_components.code,{children:`system rollback \u003cREVISION>`}),` only if required. Avoid treating a blind rollback as risk-free: it can change current access. Keep exported files in protected storage and remove temporary copies after the approved work.`]}),`\n`,_jsx(Heading,{level:`2`,id:`current-behavior-check-—-2026-10-28`,children:`Current behavior check — 2026-10-28`}),`\n`,_jsx(_components.p,{children:`Carry sourceRevision from a fresh export into the reviewed change. A stale apply is rejected even if test/diff previously looked valid; re-export and reconcile before retrying. Same-state reapply can be NO CHANGE, but an old export is not a reusable force-overwrite mechanism.`}),`\n`,_jsxs(_components.p,{children:[_jsx(_components.a,{href:`/drlink/cli-reference`,children:`Current CLI inventory`}),` · `,_jsx(_components.a,{href:`/reference/mcp-validation`,children:`MCP compatibility`})]})]})}function MDXContent(props={}){const{wrapper:MDXLayout}={..._provideComponents(),...props.components};return MDXLayout?_jsx(MDXLayout,{...props,children:_jsx(_createMdxContent,{...props})}):_createMdxContent(props)}return{default:MDXContent};function _missingMdxReference(id,component){throw new Error(`Expected `+(component?`component`:`object`)+\" `\"+id+\"` to be defined: you likely forgot to import, pass, or provide it.\")}","frontmatter":{},"scope":{"config":{},"pageMetadata":{"title":"Use case: ConfigurationBundle safely","description":"Validate, diff, apply and export a reviewed v2.4 Server configuration change.","href":"/use-cases/configuration-bundle"}}},"mdxSourceWithNoJs":null},"mdxExtracts":{"tableOfContents":[{"title":"Roll out reviewed policy with a ConfigurationBundle","slug":"roll-out-reviewed-policy-with-a-configurationbundle","depth":1,"children":[]},{"title":"Step 1 — confirm Server role and baseline","slug":"step-1-—-confirm-server-role-and-baseline","depth":2,"children":[]},{"title":"Step 2 — write a complete desired-change bundle","slug":"step-2-—-write-a-complete-desired-change-bundle","depth":2,"children":[]},{"title":"Step 3 — validate and compare before mutation","slug":"step-3-—-validate-and-compare-before-mutation","depth":2,"children":[]},{"title":"Step 4 — apply the reviewed change","slug":"step-4-—-apply-the-reviewed-change","depth":2,"children":[]},{"title":"Step 5 — prove policy plus traffic","slug":"step-5-—-prove-policy-plus-traffic","depth":2,"children":[]},{"title":"Recovery and cleanup","slug":"recovery-and-cleanup","depth":2,"children":[]},{"title":"Current behavior check — 2026-10-28","slug":"current-behavior-check-—-2026-10-28","depth":2,"children":[]}],"codeExamples":{}},"jsLinks":[],"subdomain":"data-relay","siteName":"DataRelay Link","title":"Use case: ConfigurationBundle safely - DataRelay Link","navMaps":{"firstHrefInVersion":{},"firstHrefInLanguage":{"en":{"href":"/use-cases/configuration-bundle","matchLevel":0},"ko":{"href":"/ko/use-cases/configuration-bundle","matchLevel":1}}},"lastModified":"2026-10-29T02:38:37.986Z","gitLastModified":"2026-10-29T02:38:30.000Z","originalFileLocation":"use-cases/configuration-bundle.mdx","locale":"en"},"headHtml":"\u003cscript data-mint-head>(function(){var d=document.documentElement,p=null;if(!p){try{p=localStorage.getItem(\"isDarkMode\")}catch(e){}if(p==='true')p='dark';else if(p==='false')p='light';if(p!=='light'\u0026\u0026p!=='dark'\u0026\u0026p!=='system')p=\"system\"}var r=p==='system'?(matchMedia(\"(prefers-color-scheme: dark)\").matches?'dark':'light'):p;d.classList.remove(r==='dark'?'light':'dark');d.classList.add(r);d.setAttribute(\"data-theme-preference\",p)})();\u003c/script>\u003cmeta data-mint-head name=\"description\" content=\"Validate, diff, apply and export a reviewed v2.4 Server configuration change.\">\u003cmeta data-mint-head name=\"application-name\" content=\"DataRelay Link\">\u003cmeta data-mint-head name=\"generator\" content=\"Mintlify\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"192x192\" href=\"/mintlify-assets/_mintlify/favicons/data-relay/gMMMsFWCyqO9qwwH/_generated/favicon/android-chrome-192x192.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"apple-touch-icon\" type=\"image/png\" sizes=\"180x180\" href=\"/mintlify-assets/_mintlify/favicons/data-relay/gMMMsFWCyqO9qwwH/_generated/favicon/apple-touch-icon.png\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"16x16\" href=\"/mintlify-assets/_mintlify/favicons/data-relay/gMMMsFWCyqO9qwwH/_generated/favicon/favicon-16x16.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"32x32\" href=\"/mintlify-assets/_mintlify/favicons/data-relay/gMMMsFWCyqO9qwwH/_generated/favicon/favicon-32x32.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"shortcut icon\" type=\"image/x-icon\" href=\"/mintlify-assets/_mintlify/favicons/data-relay/gMMMsFWCyqO9qwwH/_generated/favicon/favicon.ico\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"192x192\" href=\"/mintlify-assets/_mintlify/favicons/data-relay/gMMMsFWCyqO9qwwH/_generated/favicon-dark/android-chrome-192x192.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"16x16\" href=\"/mintlify-assets/_mintlify/favicons/data-relay/gMMMsFWCyqO9qwwH/_generated/favicon-dark/favicon-16x16.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"32x32\" href=\"/mintlify-assets/_mintlify/favicons/data-relay/gMMMsFWCyqO9qwwH/_generated/favicon-dark/favicon-32x32.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"shortcut icon\" type=\"image/x-icon\" href=\"/mintlify-assets/_mintlify/favicons/data-relay/gMMMsFWCyqO9qwwH/_generated/favicon-dark/favicon.ico\" media=\"(prefers-color-scheme: dark)\">\u003cmeta data-mint-head property=\"og:title\" content=\"Use case: ConfigurationBundle safely - DataRelay Link\">\u003cmeta data-mint-head property=\"og:description\" content=\"Validate, diff, apply and export a reviewed v2.4 Server configuration change.\">\u003cmeta data-mint-head property=\"og:site_name\" content=\"DataRelay Link\">\u003cmeta data-mint-head property=\"og:url\" content=\"https://link.datarelay.run/use-cases/configuration-bundle\">\u003cmeta data-mint-head property=\"og:type\" content=\"website\">\u003cmeta data-mint-head property=\"og:image\" content=\"https://data-relay.mintlify.app/_mintlify/api/og/v2?division=Practical+Use+Cases\u0026amp;title=Use+case%3A+ConfigurationBundle+safely\u0026amp;description=Validate%2C+diff%2C+apply+and+export+a+reviewed+v2.4+Server+configuration+change.\u0026amp;theme=60d049ab3c70b24e2c2b6ae4\u0026amp;signature=7575f2cbb7310a2207e748e2f3611cd1be336ecce0c51e325f90b19fd4f12140\">\u003cmeta data-mint-head property=\"og:image:width\" content=\"1200\">\u003cmeta data-mint-head property=\"og:image:height\" content=\"630\">\u003cmeta data-mint-head name=\"twitter:card\" content=\"summary_large_image\">\u003cmeta data-mint-head name=\"twitter:title\" content=\"Use case: ConfigurationBundle safely - DataRelay Link\">\u003cmeta data-mint-head name=\"twitter:description\" content=\"Validate, diff, apply and export a reviewed v2.4 Server configuration change.\">\u003cmeta data-mint-head name=\"twitter:image\" content=\"https://data-relay.mintlify.app/_mintlify/api/og/v2?division=Practical+Use+Cases\u0026amp;title=Use+case%3A+ConfigurationBundle+safely\u0026amp;description=Validate%2C+diff%2C+apply+and+export+a+reviewed+v2.4+Server+configuration+change.\u0026amp;theme=60d049ab3c70b24e2c2b6ae4\u0026amp;signature=7575f2cbb7310a2207e748e2f3611cd1be336ecce0c51e325f90b19fd4f12140\">\u003cmeta data-mint-head name=\"twitter:image:width\" content=\"1200\">\u003cmeta data-mint-head name=\"twitter:image:height\" content=\"630\">\u003cmeta data-mint-head name=\"msapplication-config\" content=\"/mintlify-assets/_mintlify/favicons/data-relay/gMMMsFWCyqO9qwwH/_generated/favicon/browserconfig.xml\">\u003cmeta data-mint-head name=\"apple-mobile-web-app-title\" content=\"DataRelay Link\">\u003cmeta data-mint-head name=\"msapplication-TileColor\" content=\"#C2410C\">\u003clink data-mint-head rel=\"canonical\" href=\"https://link.datarelay.run/use-cases/configuration-bundle\">\u003clink data-mint-head rel=\"alternate\" type=\"application/xml\" href=\"/sitemap.xml\">\u003clink data-mint-head rel=\"alternate\" type=\"text/markdown\" href=\"/use-cases/configuration-bundle.md\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"en\" href=\"https://link.datarelay.run/use-cases/configuration-bundle\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"ko\" href=\"https://link.datarelay.run/ko/use-cases/configuration-bundle\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"x-default\" href=\"https://link.datarelay.run/use-cases/configuration-bundle\">\u003cscript data-mint-head type=\"application/ld+json\">{\"@context\":\"https://schema.org\",\"@graph\":[{\"@type\":\"Organization\",\"@id\":\"https://link.datarelay.run/#organization\",\"name\":\"DataRelay Link\",\"url\":\"https://link.datarelay.run\",\"logo\":{\"@type\":\"ImageObject\",\"url\":\"https://mintcdn.com/data-relay/QdSvVfPZ7NEJSOWl/logo/light.svg?fit=max\u0026auto=format\u0026n=QdSvVfPZ7NEJSOWl\u0026q=85\u0026s=888463e35ab49f73f9b174030b3263d6\"}},{\"@type\":\"WebSite\",\"@id\":\"https://link.datarelay.run#website\",\"name\":\"DataRelay Link\",\"url\":\"https://link.datarelay.run\",\"publisher\":{\"@id\":\"https://link.datarelay.run/#organization\"}},{\"@type\":\"WebPage\",\"@id\":\"https://link.datarelay.run/use-cases/configuration-bundle#webpage\",\"url\":\"https://link.datarelay.run/use-cases/configuration-bundle\",\"name\":\"Use case: ConfigurationBundle safely\",\"description\":\"Validate, diff, apply and export a reviewed v2.4 Server configuration change.\",\"dateModified\":\"2026-10-29T02:38:30.000Z\",\"isPartOf\":{\"@id\":\"https://link.datarelay.run#website\"},\"breadcrumb\":{\"@id\":\"https://link.datarelay.run/use-cases/configuration-bundle#breadcrumb\"}},{\"@type\":\"BreadcrumbList\",\"@id\":\"https://link.datarelay.run/use-cases/configuration-bundle#breadcrumb\",\"itemListElement\":[{\"@type\":\"ListItem\",\"position\":1,\"name\":\"Practical Use Cases\",\"item\":\"https://link.datarelay.run/use-cases/index\"},{\"@type\":\"ListItem\",\"position\":2,\"name\":\"Use case: ConfigurationBundle safely\",\"item\":\"https://link.datarelay.run/use-cases/configuration-bundle\"}]},{\"@type\":[\"Article\",\"TechArticle\"],\"@id\":\"https://link.datarelay.run/use-cases/configuration-bundle#article\",\"headline\":\"Use case: ConfigurationBundle safely\",\"name\":\"Use case: ConfigurationBundle safely\",\"description\":\"Validate, diff, apply and export a reviewed v2.4 Server configuration change.\",\"url\":\"https://link.datarelay.run/use-cases/configuration-bundle\",\"mainEntityOfPage\":{\"@id\":\"https://link.datarelay.run/use-cases/configuration-bundle#webpage\"},\"dateModified\":\"2026-10-29T02:38:30.000Z\",\"publisher\":{\"@id\":\"https://link.datarelay.run/#organization\"},\"isPartOf\":{\"@id\":\"https://link.datarelay.run#website\"}}]}\u003c/script>\u003cscript data-mint-head type=\"application/ld+json\">{\"@context\":\"https://schema.org\",\"@type\":\"WebSite\",\"name\":\"DataRelay Link\",\"creator\":{\"@type\":\"Organization\",\"name\":\"Mintlify\",\"url\":\"https://mintlify.com\"}}\u003c/script>","siteName":"DataRelay Link","nav":{"global":null,"languages":[{"language":"en","groups":[{"group":"Getting Started","icon":"rocket","pages":[{"title":"DataRelay Link","href":""},{"title":"What is DataRelay Link?","sidebarTitle":"What is DataRelay Link?","href":"/getting-started/overview"},{"title":"Concepts \u0026 Mental Model","sidebarTitle":"Concepts \u0026 Mental Model","icon":"diagram-project","href":"/getting-started/concepts"},{"title":"OCI Free Tier Server Preparation","sidebarTitle":"OCI Free Tier Server","icon":"cloud","href":"/getting-started/oci-free-tier-server"},{"title":"OCI Network and VM","sidebarTitle":"OCI Network \u0026 VM","icon":"cloud","href":"/getting-started/oci-network-vm"},{"title":"Install DataRelay Link on OCI","sidebarTitle":"Install DataRelay Link","icon":"server","href":"/getting-started/oci-drlink-install"},{"title":"Quick Start","href":"/getting-started/quickstart"},{"title":"Server Installation","href":"/getting-started/server-installation"},{"title":"Linux Agent Host","sidebarTitle":"Linux Agent Host","href":"/getting-started/linux-client"},{"title":"macOS Agent Host","sidebarTitle":"macOS Agent Host","href":"/getting-started/macos-client"},{"title":"Windows Agent Host","sidebarTitle":"Windows Agent Host","href":"/getting-started/windows-client"}]},{"group":"Practical Use Cases","icon":"list-check","pages":[{"title":"Scenario Playbooks","sidebarTitle":"Use Cases","href":"/use-cases/index"},{"title":"Use case: Remote SSH through NAT","href":"/use-cases/remote-ssh"},{"title":"Use case: One LAN gateway, multiple services","href":"/use-cases/lan-relay"},{"title":"Use case: Private HTTPS console","href":"/use-cases/private-web"},{"title":"Use case: Office-only Remote Access","href":"/use-cases/office-allowlist"},{"title":"Use case: Fixed TCP remote database","href":"/use-cases/fixed-tcp-database"},{"title":"Use case: Ubuntu APT in a restricted network","href":"/use-cases/ubuntu-updates"},{"title":"Use case: Git and HTTPS API from a restricted host","href":"/use-cases/github-egress"},{"title":"Use case: Read-only AI / MCP access","href":"/use-cases/ai-readonly"},{"title":"Use case: AI Server files, Git and jobs","href":"/use-cases/ai-server-control"},{"title":"Use case: Enroll multiple branch hosts","description":"Issue multiple one-time Agent enrollments and manage inventory without broad fleet automation.","href":"/use-cases/bulk-onboarding"},{"title":"Use case: ConfigurationBundle safely","href":"/use-cases/configuration-bundle"},{"title":"Use case: Backup and restore","description":"Protect Server identities, policies and service reservations, then verify recovery.","href":"/use-cases/backup-recovery"}]},{"group":"Managed Hosts \u0026 Objects","icon":"network-wired","pages":[{"title":"Managed Host Enrollment","sidebarTitle":"Managed Host Enrollment","href":"/guides/enrollment"},{"title":"Zero-Touch Enrollment","href":"/guides/zero-touch"},{"title":"Objects \u0026 Groups","sidebarTitle":"Objects \u0026 Groups","href":"/guides/groups"}]},{"group":"Remote Services \u0026 Access","icon":"arrow-right-to-bracket","pages":[{"title":"SSH","href":"/guides/ssh"},{"title":"Remote Services","sidebarTitle":"Remote Services","href":"/guides/services"},{"title":"HTTP \u0026 HTTPS","href":"/guides/http-https"},{"title":"Custom TCP \u0026 LAN Targets","href":"/guides/custom-tcp-lan"},{"title":"Remote Access","href":"/guides/remote-access"}]},{"group":"Internet Access","icon":"globe","pages":[{"title":"Internet Access","href":"/guides/internet-access"}]},{"group":"AI Access","icon":"robot","pages":[{"title":"AI Access \u0026 MCP","href":"/guides/ai-access"},{"title":"Claude \u0026 ChatGPT MCP Setup","href":"/guides/mcp-clients"},{"title":"MCP Tool Reference","href":"/reference/mcp-tools"},{"title":"MCP Compatibility","href":"/reference/mcp-validation"}]},{"group":"CLI \u0026 Configuration","icon":"terminal","pages":[{"title":"drlink Guide","href":"/drlink/overview"},{"title":"CLI Reference","href":"/drlink/cli-reference"},{"title":"ConfigurationBundle","href":"/drlink/configuration-bundle"}]},{"group":"Deployment","icon":"route","pages":[{"title":"Deployment Modes","href":"/deployment/modes"},{"title":"Firewall \u0026 NAT","href":"/deployment/firewall-nat"},{"title":"DNS \u0026 Public Hostname","href":"/deployment/dns-hostname"}]},{"group":"Operations","icon":"screwdriver-wrench","pages":[{"title":"Operations Overview","sidebarTitle":"Operations Overview","icon":"screwdriver-wrench","href":"/operations/maintenance"},{"title":"Updates","href":"/operations/updates"},{"title":"Backup \u0026 Restore","href":"/operations/backup-restore"},{"title":"Diagnostics","href":"/operations/diagnostics"},{"title":"Lifecycle Semantics","href":"/operations/lifecycle"},{"title":"Troubleshooting","href":"/troubleshooting/overview"},{"title":"Feedback","href":"/feedback/index"}]},{"group":"Security \u0026 Reference","icon":"shield-halved","pages":[{"title":"Security Overview","href":"/security/overview"},{"title":"Architecture","sidebarTitle":"Architecture","icon":"sitemap","href":"/reference/architecture"},{"title":"DataRelay Link and Managed Alternatives","sidebarTitle":"Compare Alternatives","href":"/reference/alternatives"},{"title":"Supported Platforms","href":"/reference/platforms"},{"title":"Network Ports","href":"/reference/network-ports"},{"title":"Version \u0026 Updates","href":"/reference/release-status"},{"title":"Glossary","sidebarTitle":"Glossary","icon":"book-open","href":"/reference/glossary"},{"title":"Known Limits","href":"/reference/limitations"},{"title":"License","sidebarTitle":"License","icon":"scale-balanced","href":"/reference/license"}]}]},{"language":"ko","pages":[{"title":"ko","href":"/ko/use-cases/configuration-bundle"}]}]},"basePath":"","title":"Use case: ConfigurationBundle safely - DataRelay Link","buildId":"dpl_DeHjVRGfFnhYQwHnfC2pjeXXv8h9","deploymentId":"dpl_DeHjVRGfFnhYQwHnfC2pjeXXv8h9","dynamics":["a74be98ba7"],"chunks":["zoom-image-lightbox-BG6oD64b.js","lightbox-handle-r17bVUz3.js"]}